processing / processing/processing-website
F-Secure finds 3 instances of Java/Blackhole malware exploit in Processing docs zip file
Chưa có ai nhận issue này.
- Ngôn ngữ chính
- MDX
- Star
- 90
- Fork
- 122
- Merge trung bình
- 1 giờ 43 phút
- Pull request đã merge (30 ngày)
- 3
Mô tả
Issue description
Steps to reproduce: (28 November 2020)
OS Windows 10 Pro, latest version;
Microsoft Edge, latest version.
F-Secure anti-virus, fully up-to-date:
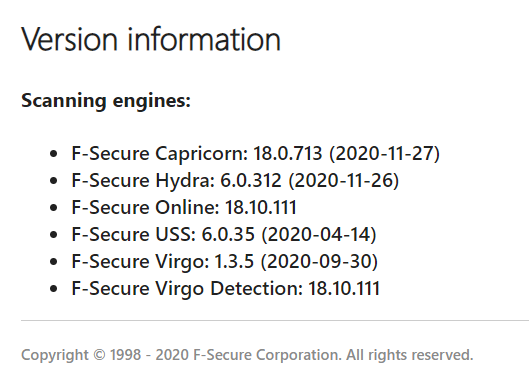
Downloaded zip file of processing/docs (28 November 2020).
Scanned with up-to-date F-Secure anti-virus.
3 instances of the blackhole exploit found:
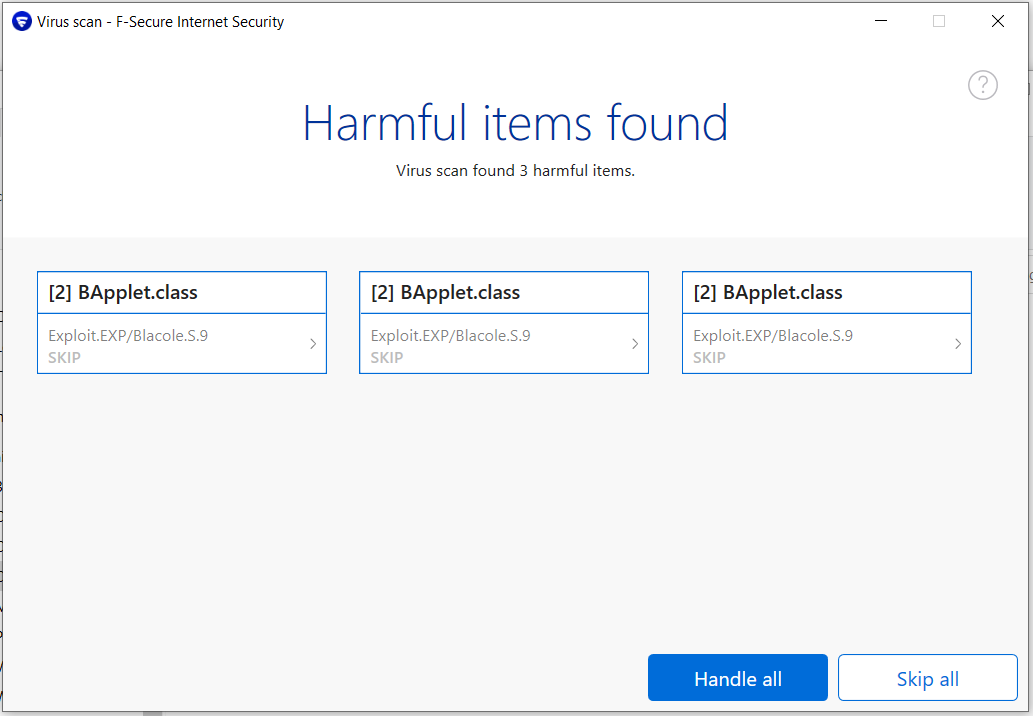
[2] BApplet.class
Exploit.EXP/Blacole.S.9
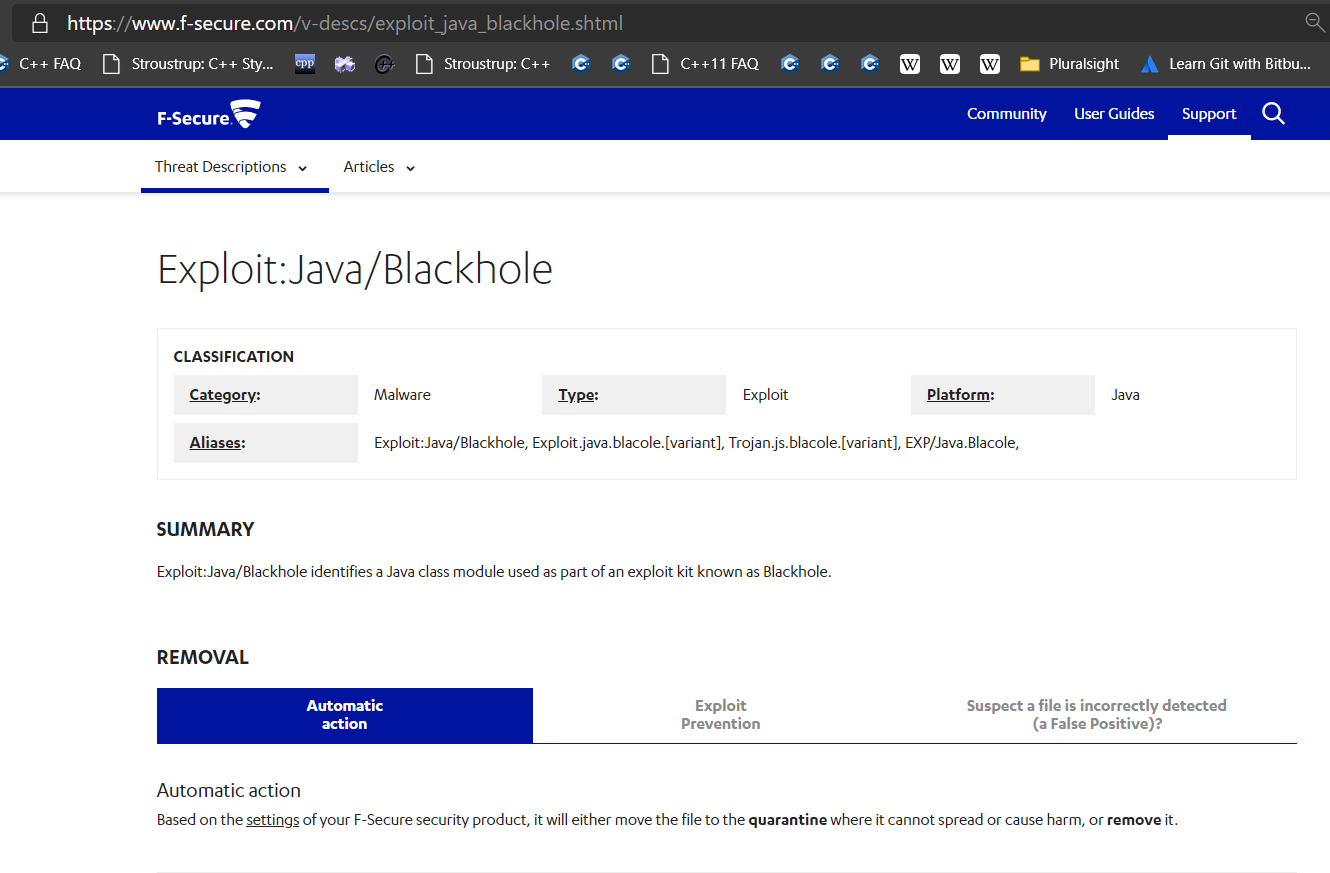
Category: Malware
Type: Exploit
Platform: Java
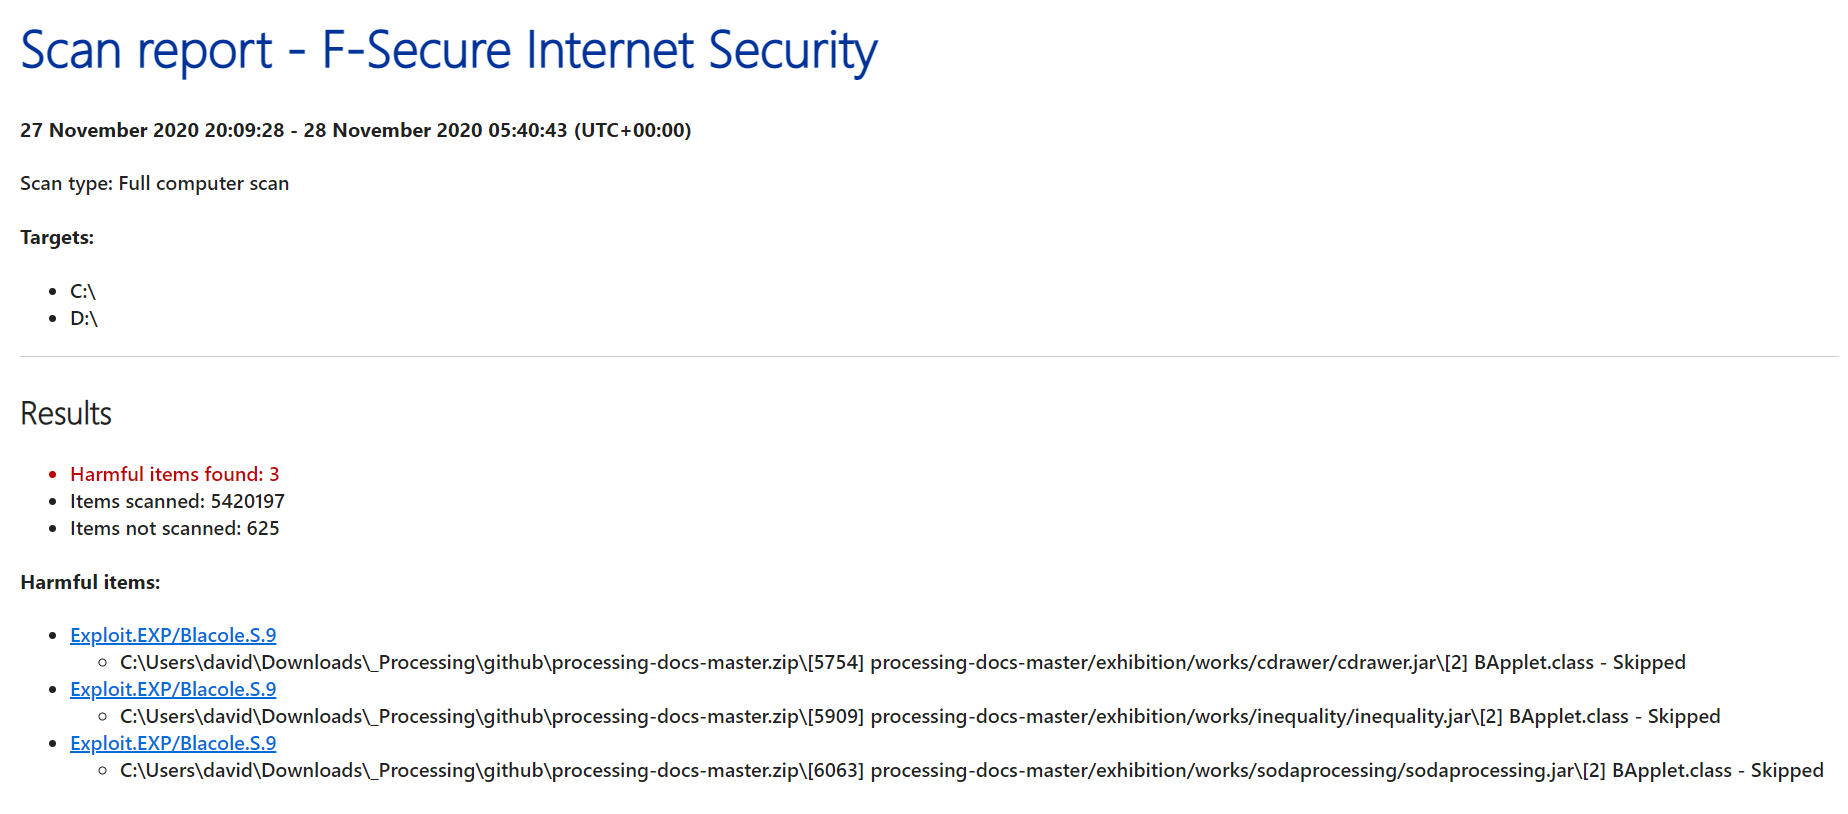
3 specific harmful items found (from the F-Secure report):
Exploit.EXP/Blacole.S.9
processing-docs-master.zip[5754] processing-docs-master/exhibition/works/cdrawer/cdrawer.jar[2] BApplet.class
processing-docs-master.zip[5909] processing-docs-master/exhibition/works/inequality/inequality.jar[2] BApplet.class
processing-docs-master.zip[6063] processing-docs-master/exhibition/works/sodaprocessing/sodaprocessing.jar[2]
Part of an exploit kit: see also:
https://www.f-secure.com/v-descs/exploit_java_blackhole.shtml
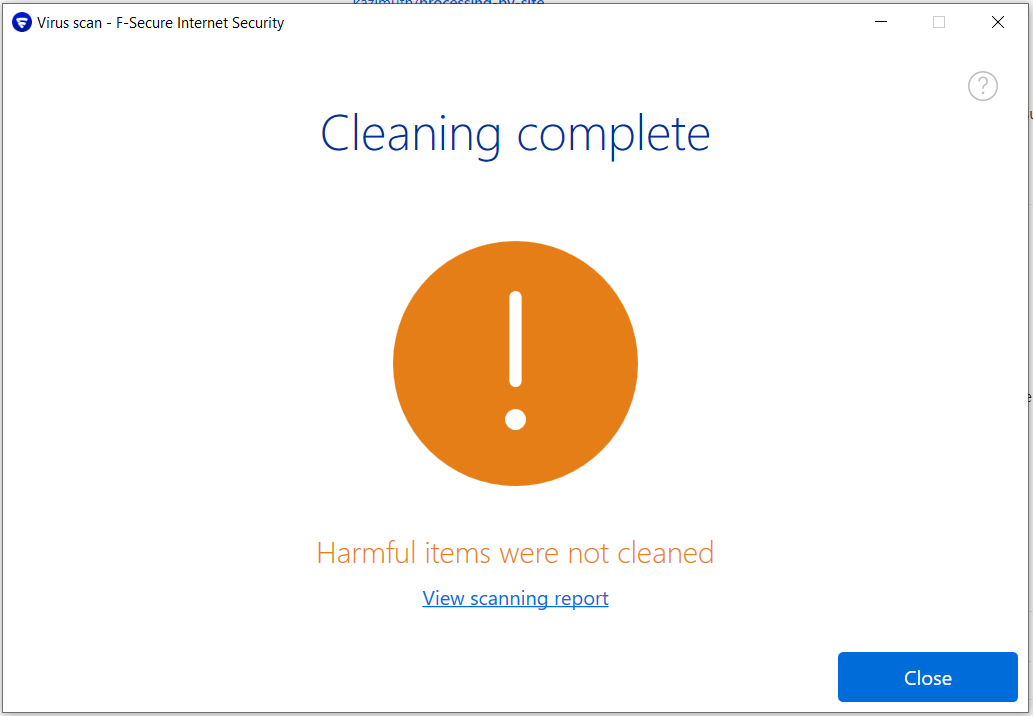
F-Secure reported that it was unable to clean the files. I reverted to deleting the zip file.
URL(s) of affected page(s)
See above note.
Proposed fix
Author to examine original code files, perhaps send individual files to F-Secure for analysis; remove exploit from affected files if the exploit is real, or modify the code to prevent false negative if that's the case, or post notice that such a false negative exists and can be safely ignored.
I would have sent the zip file to F-Secure for analysis myself, but their file-size limit is 30Mb. I'm not opening the zip file myself just in case this is a real issue.
Hướng dẫn đóng góp
Chưa lập chỉ mục được hướng dẫn đóng góp cho kho mã nguồn này
Bắt đầu từ đâu
- Đọc hết issue, rồi đọc hướng dẫn đóng góp của dự án.
- Bình luận trên issue rằng bạn sẽ nhận — tránh hai người làm cùng một việc.
- Fork repository và làm thay đổi trên một nhánh.
- Mở pull request có tham chiếu số hiệu của issue.
Hướng nghiên cứu
Bắt đầu với ba đường dẫn đã được báo cáo trong kho lưu trữ tài liệu: exhibition/works/cdrawer/cdrawer.jar, inequality/inequality.jar và sodaprocessing/sodaprocessing.jar, tập trung vào từng BApplet.class. So sánh các tệp này với mã nguồn gốc của chúng và gửi từng tệp riêng lẻ cho F-Secure để phân tích nếu có thể. Công việc được xem là hoàn tất khi xác nhận các phát hiện là thực hay dương tính giả, sau đó loại bỏ exploit hoặc ghi lại phản hồi an toàn đối với trường hợp dương tính giả.
Do mô hình lập chỉ mục viết ra từ nội dung của issue.
Đánh giá
- Công nghệ
- java
- Lĩnh vực
- documentation, security
- Loại issue
- Lỗi
- Độ khó
- 4/5
- Thời gian dự kiến
- 3-5 ngày
- Mức độ hoạt động
- Đình trệ
- Độ rõ ràng
- Khá rõ ràng
- Mức phù hợp với người mới
- 35/100