processing / processing/processing-website
F-Secure finds 3 instances of Java/Blackhole malware exploit in Processing docs zip file
还没有人认领这个 Issue。
- 主要语言
- MDX
- 星标
- 90
- 派生
- 122
- 平均合并
- 1 小时 43 分钟
- 30 天内合并 PR
- 3
描述
Issue description
Steps to reproduce: (28 November 2020)
OS Windows 10 Pro, latest version;
Microsoft Edge, latest version.
F-Secure anti-virus, fully up-to-date:
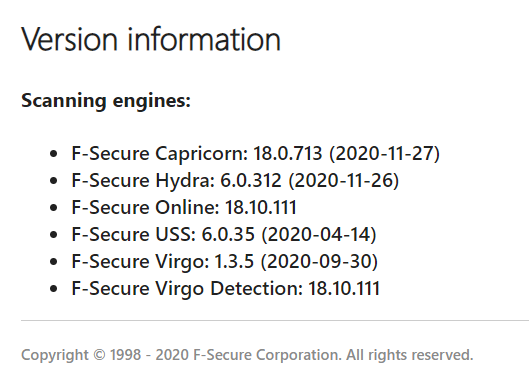
Downloaded zip file of processing/docs (28 November 2020).
Scanned with up-to-date F-Secure anti-virus.
3 instances of the blackhole exploit found:
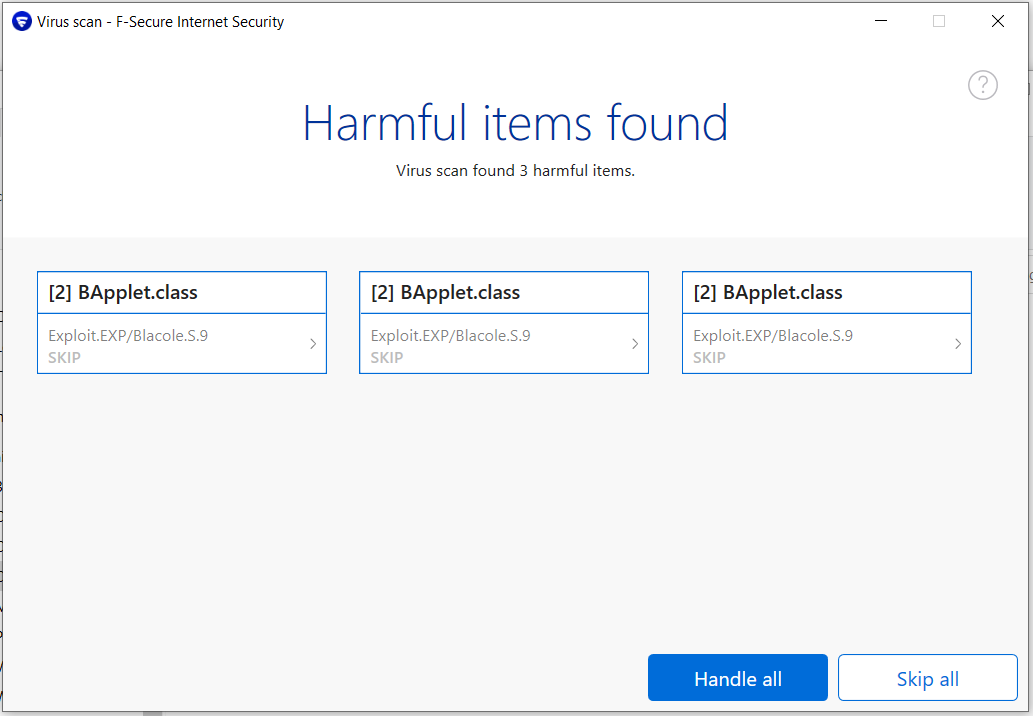
[2] BApplet.class
Exploit.EXP/Blacole.S.9
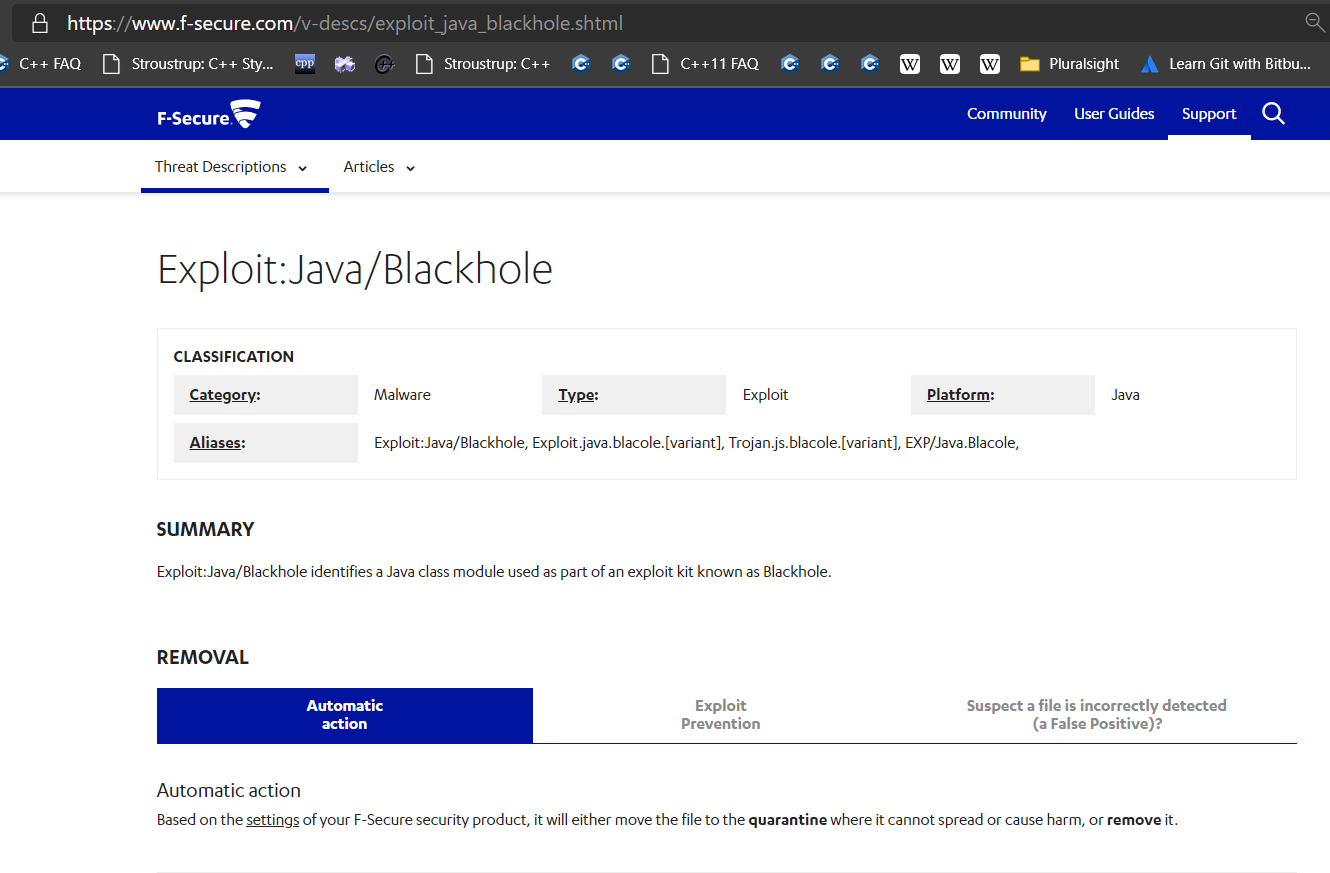
Category: Malware
Type: Exploit
Platform: Java
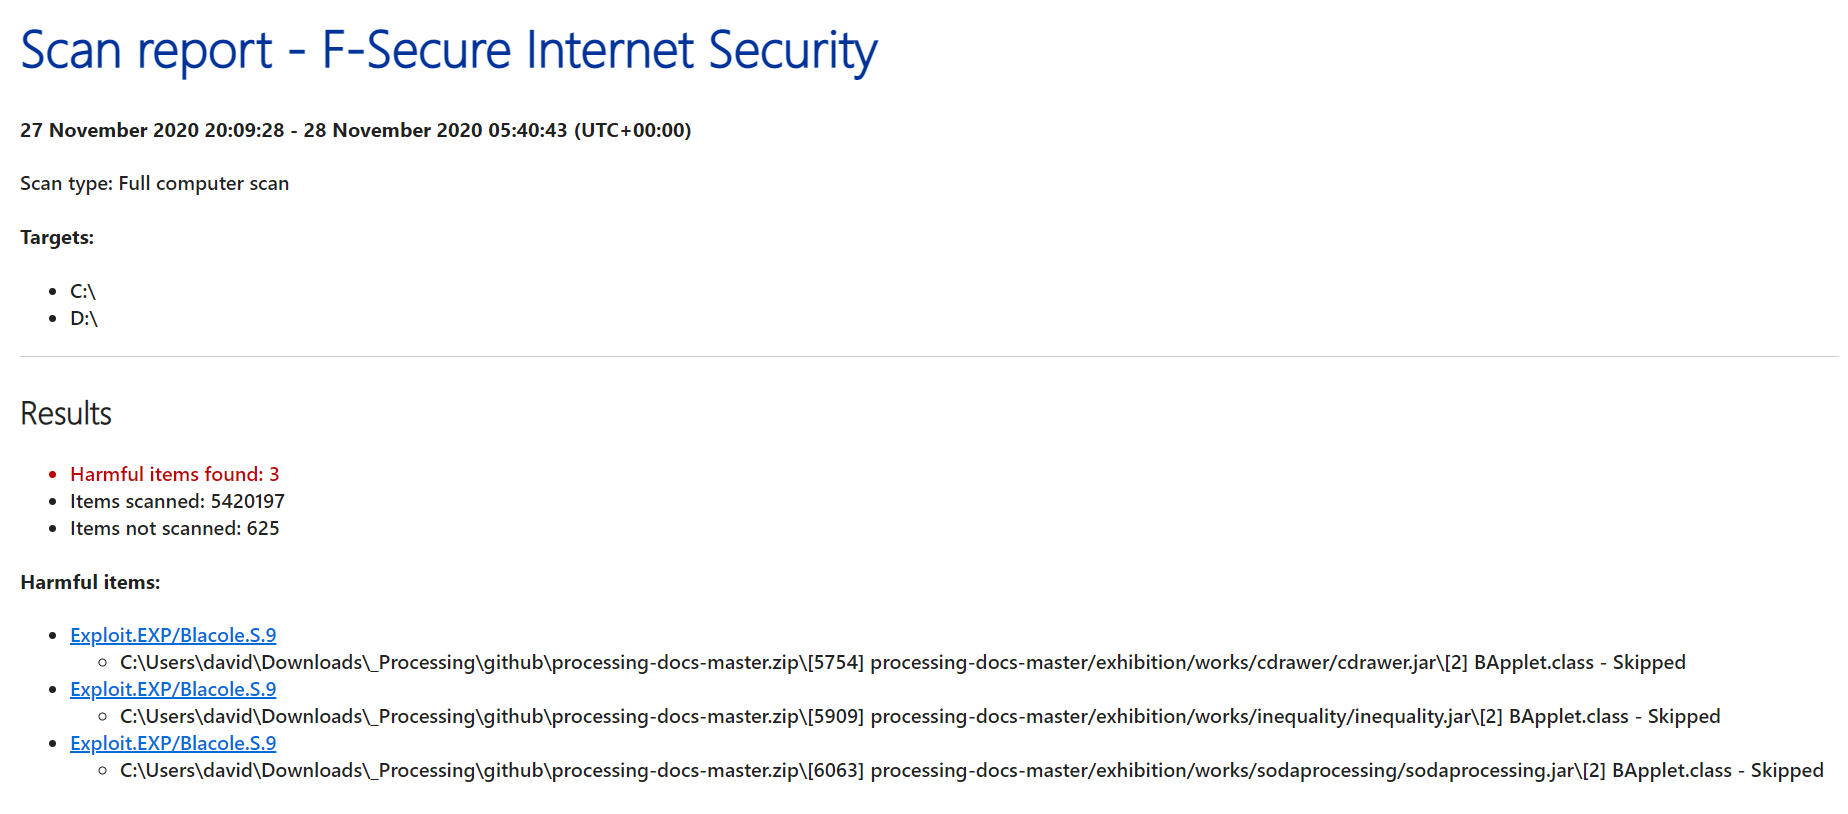
3 specific harmful items found (from the F-Secure report):
Exploit.EXP/Blacole.S.9
processing-docs-master.zip[5754] processing-docs-master/exhibition/works/cdrawer/cdrawer.jar[2] BApplet.class
processing-docs-master.zip[5909] processing-docs-master/exhibition/works/inequality/inequality.jar[2] BApplet.class
processing-docs-master.zip[6063] processing-docs-master/exhibition/works/sodaprocessing/sodaprocessing.jar[2]
Part of an exploit kit: see also:
https://www.f-secure.com/v-descs/exploit_java_blackhole.shtml
F-Secure reported that it was unable to clean the files. I reverted to deleting the zip file.
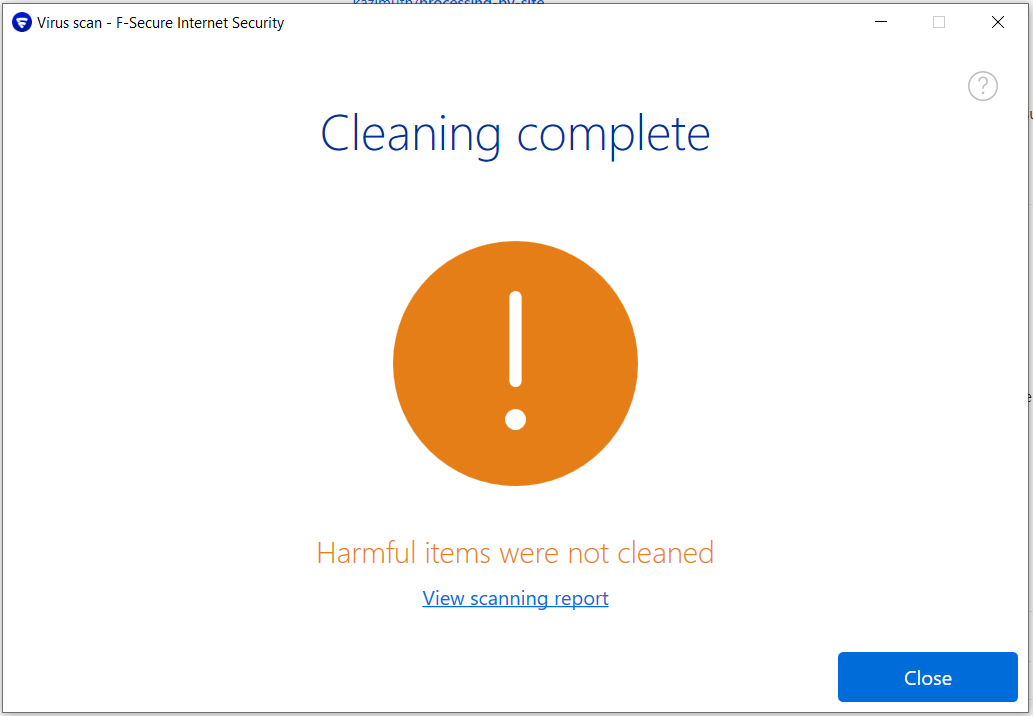
URL(s) of affected page(s)
See above note.
Proposed fix
Author to examine original code files, perhaps send individual files to F-Secure for analysis; remove exploit from affected files if the exploit is real, or modify the code to prevent false negative if that's the case, or post notice that such a false negative exists and can be safely ignored.
I would have sent the zip file to F-Secure for analysis myself, but their file-size limit is 30Mb. I'm not opening the zip file myself just in case this is a real issue.
贡献指南
这个仓库没有索引到贡献指南
从这里开始
- 先读完整个 Issue,再读项目的贡献指南。
- 在 Issue 下留言说明你要接手 —— 这能避免两个人做同样的事。
- Fork 仓库,在一个分支上完成修改。
- 提交 Pull Request,并在描述里引用这个 Issue 编号。
调研方向
从文档归档中报告的三个路径开始:exhibition/works/cdrawer/cdrawer.jar、inequality/inequality.jar 和 sodaprocessing/sodaprocessing.jar,重点检查各自的 BApplet.class。将这些文件与其原始代码进行比较,并在可能的情况下将单个文件提交给 F-Secure 进行分析。完成的标准是确认这些检测结果是真实问题还是误报,然后移除 exploit,或记录安全的误报响应。
由索引模型根据 Issue 内容生成。
评估
- 技术栈
- java
- 领域
- documentation, security
- Issue 类型
- 缺陷
- 难度
- 4/5
- 预计耗时
- 3-5 天
- 活跃度
- 停滞
- 描述清晰度
- 基本清楚
- 新手友好度
- 35/100