processing / processing/processing-website
F-Secure finds 3 instances of Java/Blackhole malware exploit in Processing docs zip file
Dieses Issue hat noch niemand übernommen.
- Vorherrschende Sprache
- MDX
- Sterne
- 90
- Forks
- 122
- Ø Merge
- 1 Std. 43 Min.
- Gemergte PRs (30 T.)
- 3
Beschreibung
Issue description
Steps to reproduce: (28 November 2020)
OS Windows 10 Pro, latest version;
Microsoft Edge, latest version.
F-Secure anti-virus, fully up-to-date:
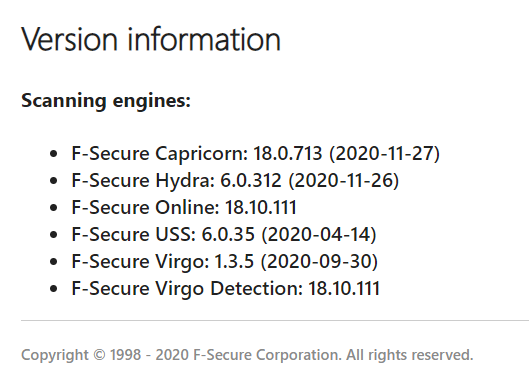
Downloaded zip file of processing/docs (28 November 2020).
Scanned with up-to-date F-Secure anti-virus.
3 instances of the blackhole exploit found:
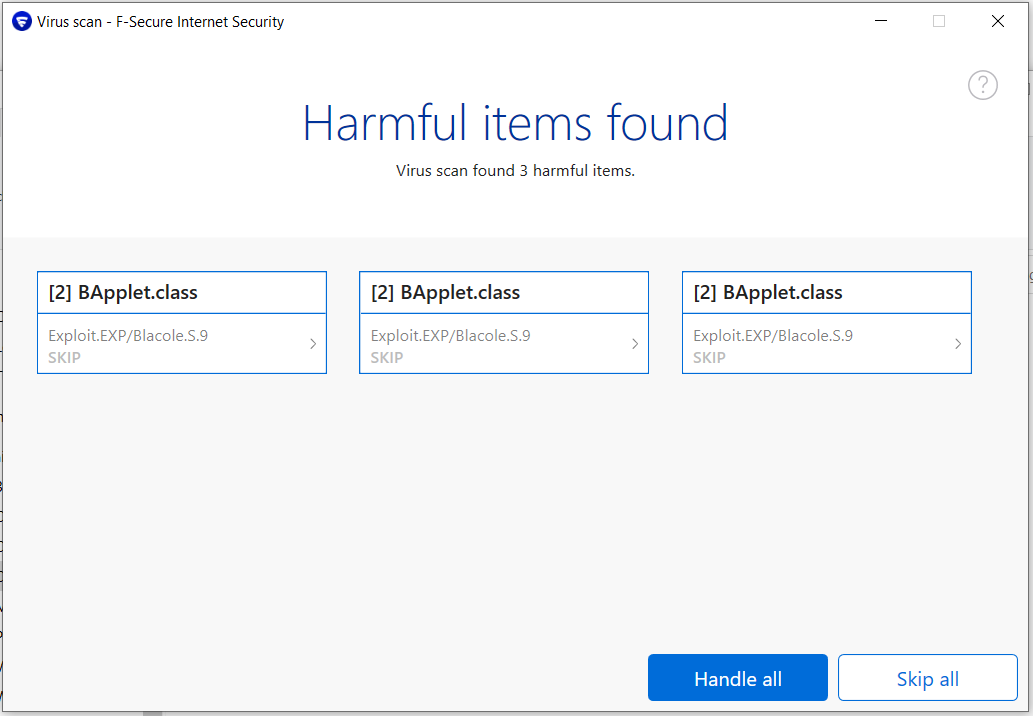
[2] BApplet.class
Exploit.EXP/Blacole.S.9
Category: Malware
Type: Exploit
Platform: Java
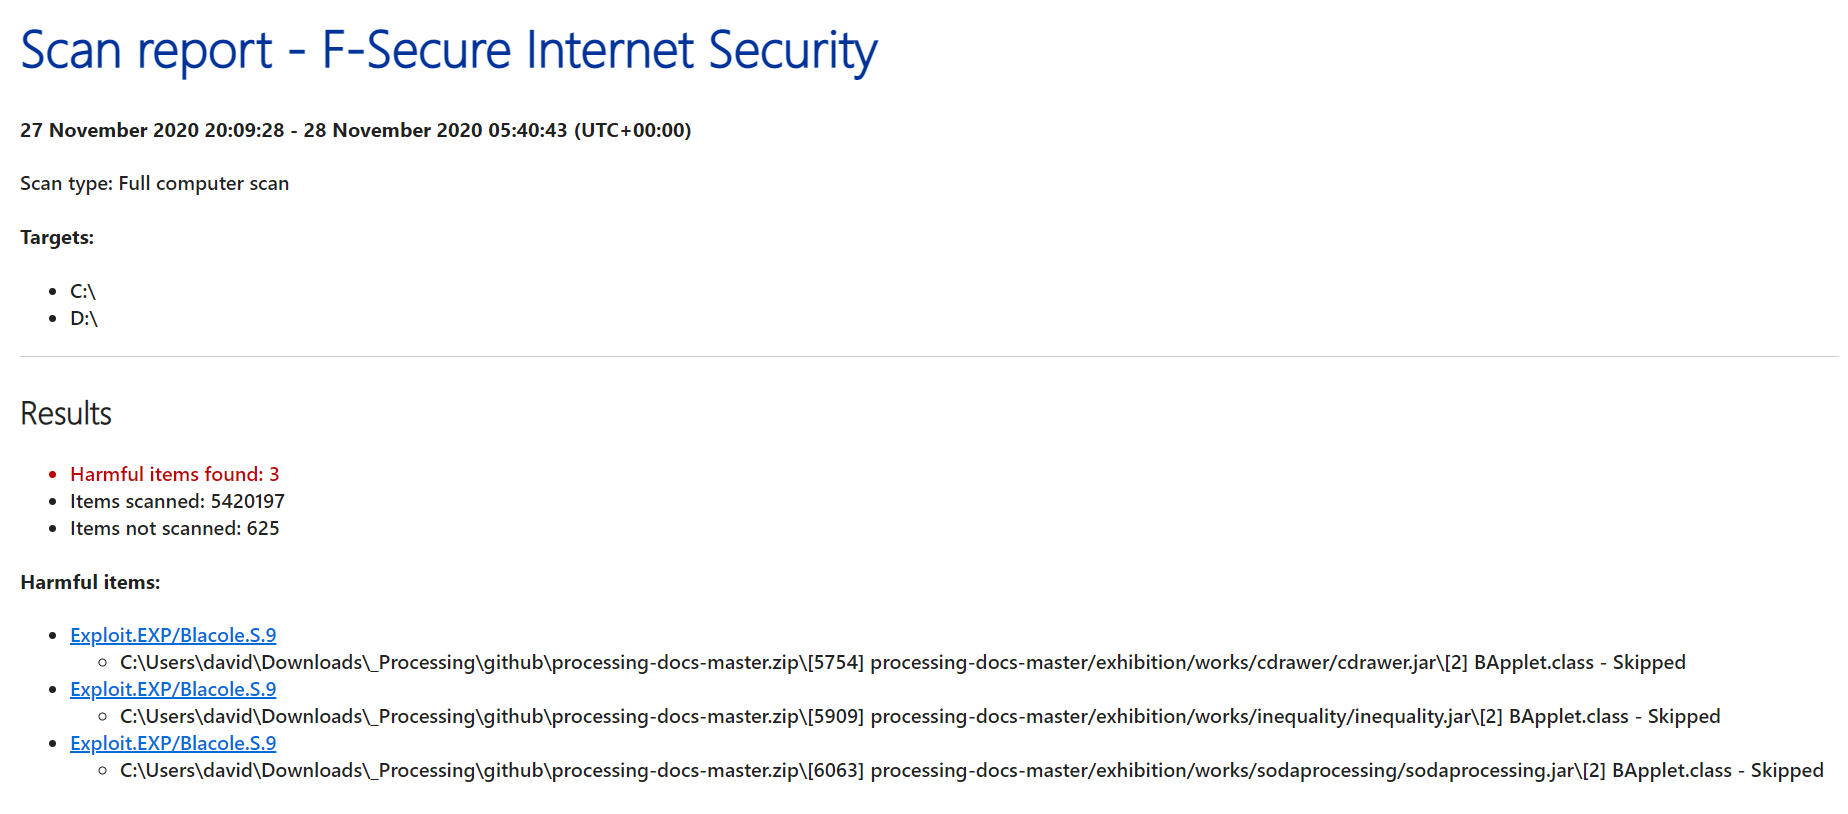
3 specific harmful items found (from the F-Secure report):
Exploit.EXP/Blacole.S.9
processing-docs-master.zip[5754] processing-docs-master/exhibition/works/cdrawer/cdrawer.jar[2] BApplet.class
processing-docs-master.zip[5909] processing-docs-master/exhibition/works/inequality/inequality.jar[2] BApplet.class
processing-docs-master.zip[6063] processing-docs-master/exhibition/works/sodaprocessing/sodaprocessing.jar[2]
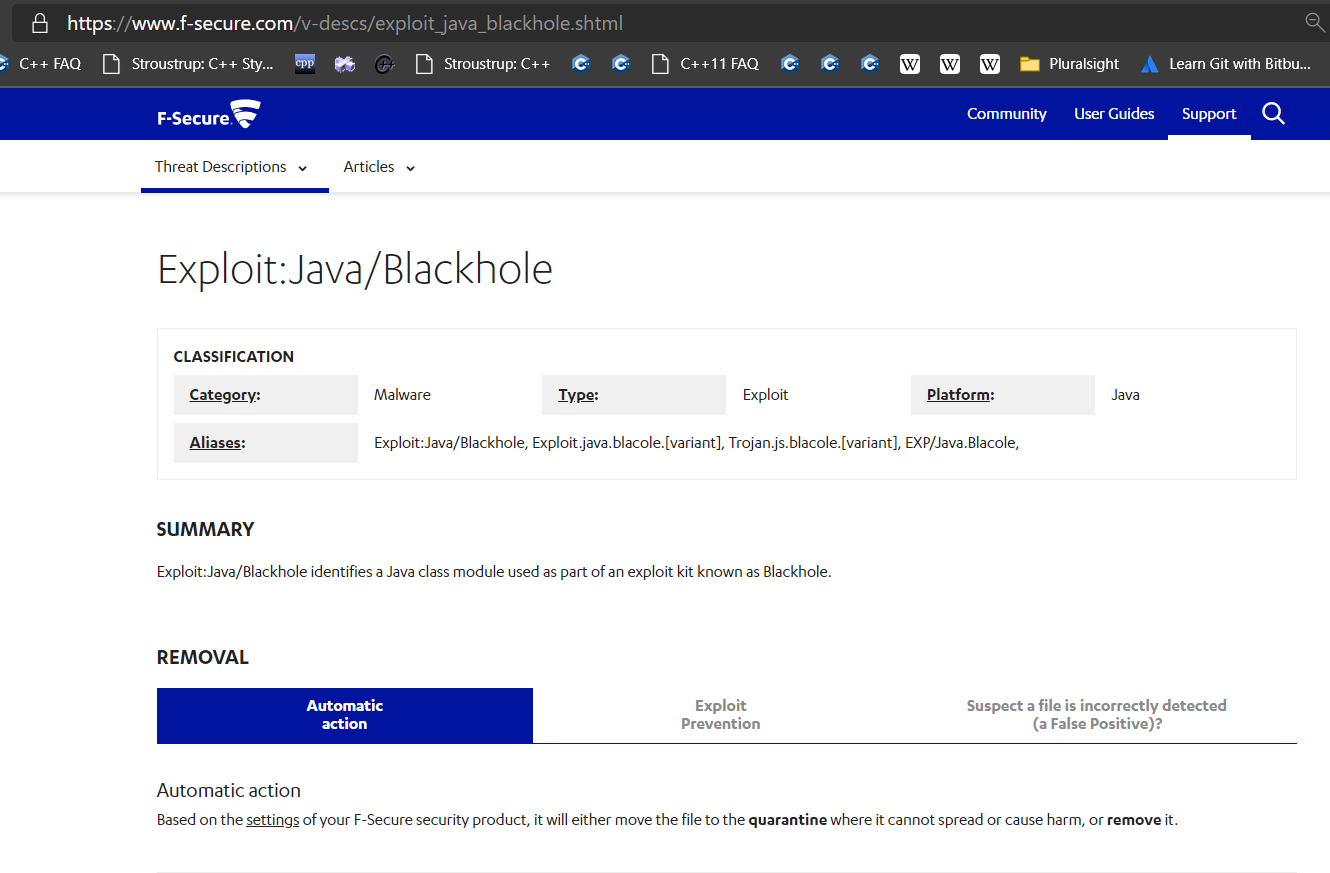
Part of an exploit kit: see also:
https://www.f-secure.com/v-descs/exploit_java_blackhole.shtml
F-Secure reported that it was unable to clean the files. I reverted to deleting the zip file.
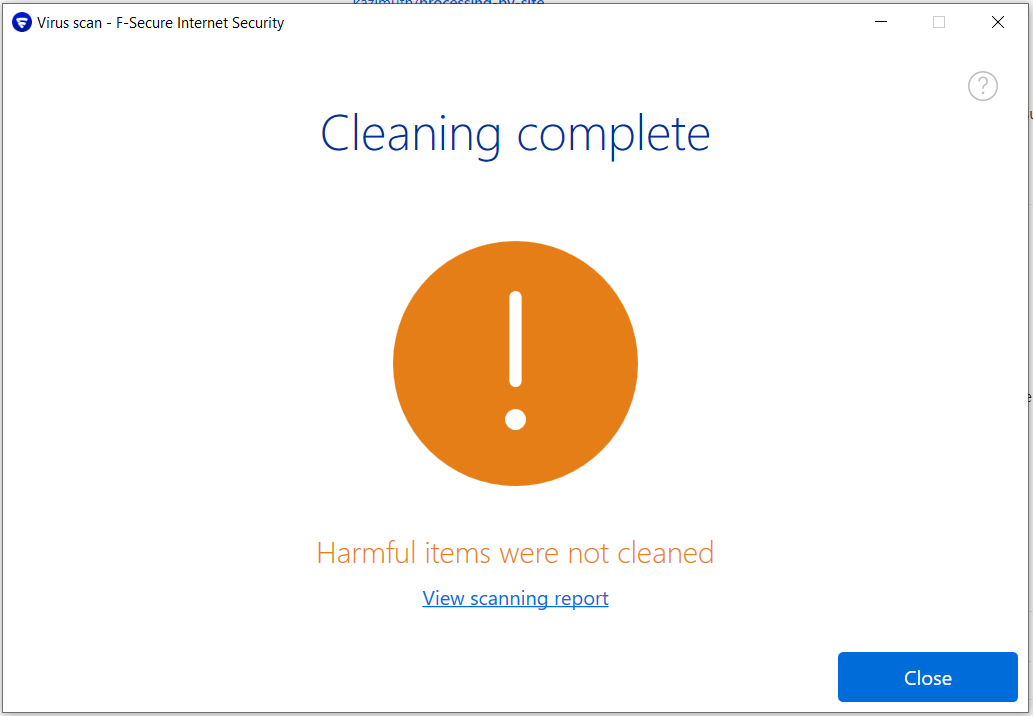
URL(s) of affected page(s)
See above note.
Proposed fix
Author to examine original code files, perhaps send individual files to F-Secure for analysis; remove exploit from affected files if the exploit is real, or modify the code to prevent false negative if that's the case, or post notice that such a false negative exists and can be safely ignored.
I would have sent the zip file to F-Secure for analysis myself, but their file-size limit is 30Mb. I'm not opening the zip file myself just in case this is a real issue.
Beitragsleitfaden
Für dieses Repository ist kein Beitragsleitfaden indexiert
Erste Schritte
- Lies das ganze Issue und danach den Beitragsleitfaden des Projekts.
- Schreib ins Issue, dass du es übernimmst — das erspart doppelte Arbeit.
- Forke das Repository und arbeite in einem Branch.
- Öffne einen Pull Request, der die Issue-Nummer nennt.
Rechercherichtung
Beginne mit den drei gemeldeten Pfaden im Dokumentationsarchiv: exhibition/works/cdrawer/cdrawer.jar, inequality/inequality.jar und sodaprocessing/sodaprocessing.jar, und konzentriere dich auf die jeweilige BApplet.class. Vergleiche diese Dateien mit ihrem ursprünglichen Code und reiche die einzelnen Dateien nach Möglichkeit zur Analyse bei F-Secure ein. Als abgeschlossen gilt die Bestätigung, ob die Erkennungen echt oder Fehlalarme sind, und anschließend das Entfernen des Exploits oder die Dokumentation einer sicheren Antwort auf den Fehlalarm.
Vom Indexierungsmodell aus dem Issue-Text verfasst.
Bewertung
- Tech-Stack
- java
- Bereich
- documentation, security
- Issue-Typ
- Bug
- Schwierigkeit
- 4/5
- Geschätzter Aufwand
- 3-5 Tage
- Aktivitätsstatus
- Veraltet
- Klarheit
- Größtenteils klar
- Anfängerfreundlichkeit
- 35/100