processing / processing/processing-website
F-Secure finds 3 instances of Java/Blackhole malware exploit in Processing docs zip file
まだ誰も着手していません。
- 主要言語
- MDX
- スター
- 90
- フォーク
- 122
- 平均マージ
- 1時間 43分
- マージ済み PR(30日)
- 3
説明
Issue description
Steps to reproduce: (28 November 2020)
OS Windows 10 Pro, latest version;
Microsoft Edge, latest version.
F-Secure anti-virus, fully up-to-date:
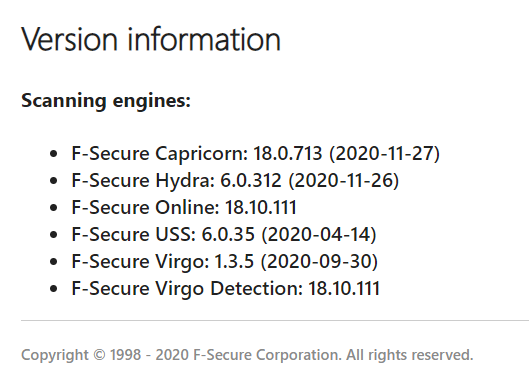
Downloaded zip file of processing/docs (28 November 2020).
Scanned with up-to-date F-Secure anti-virus.
3 instances of the blackhole exploit found:
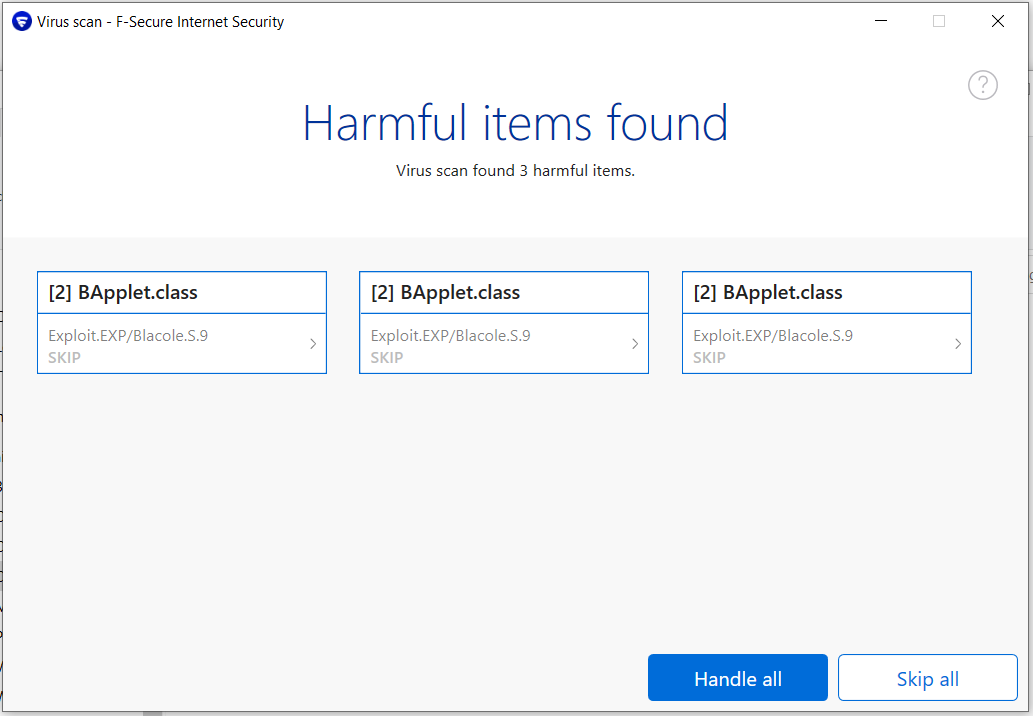
[2] BApplet.class
Exploit.EXP/Blacole.S.9
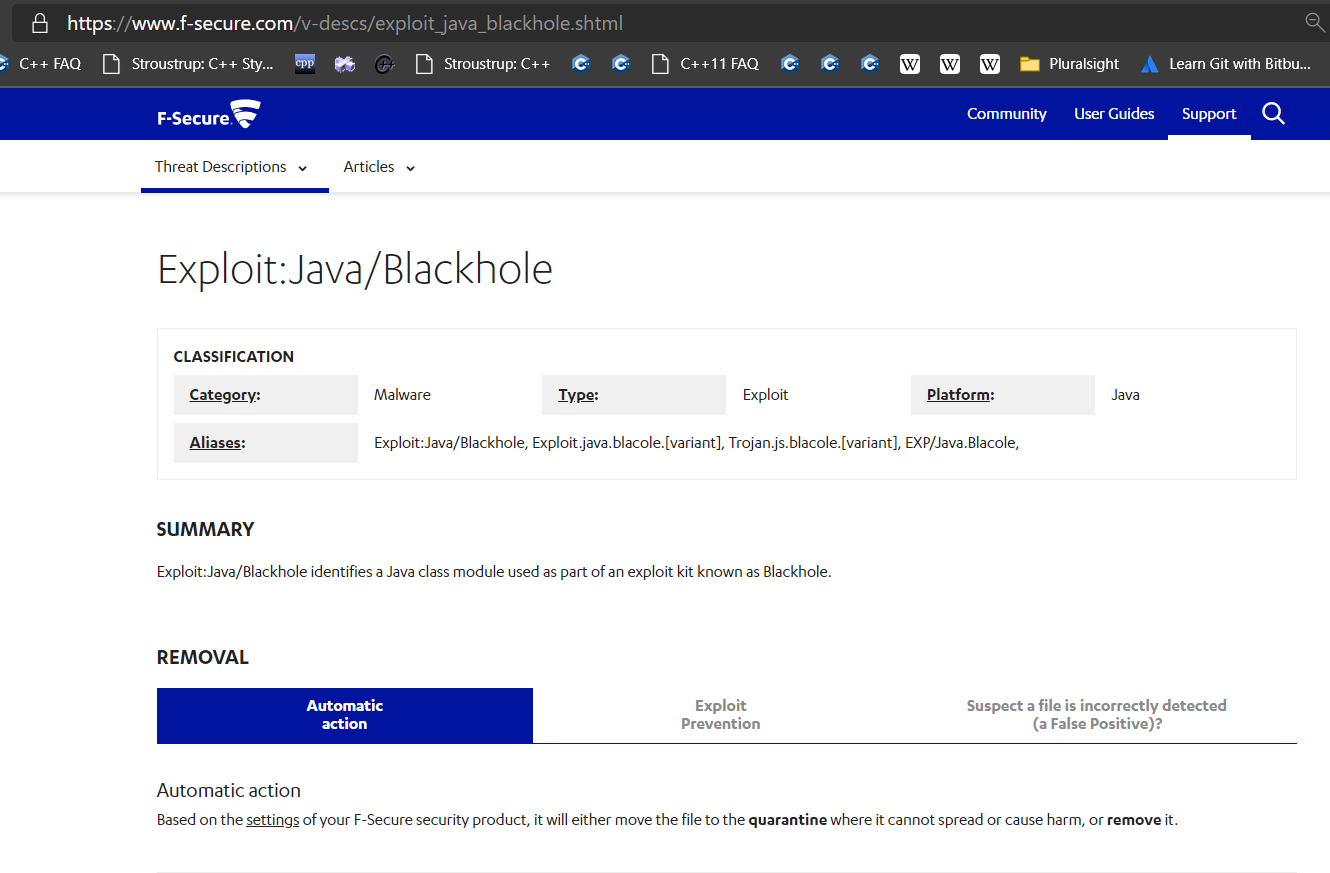
Category: Malware
Type: Exploit
Platform: Java
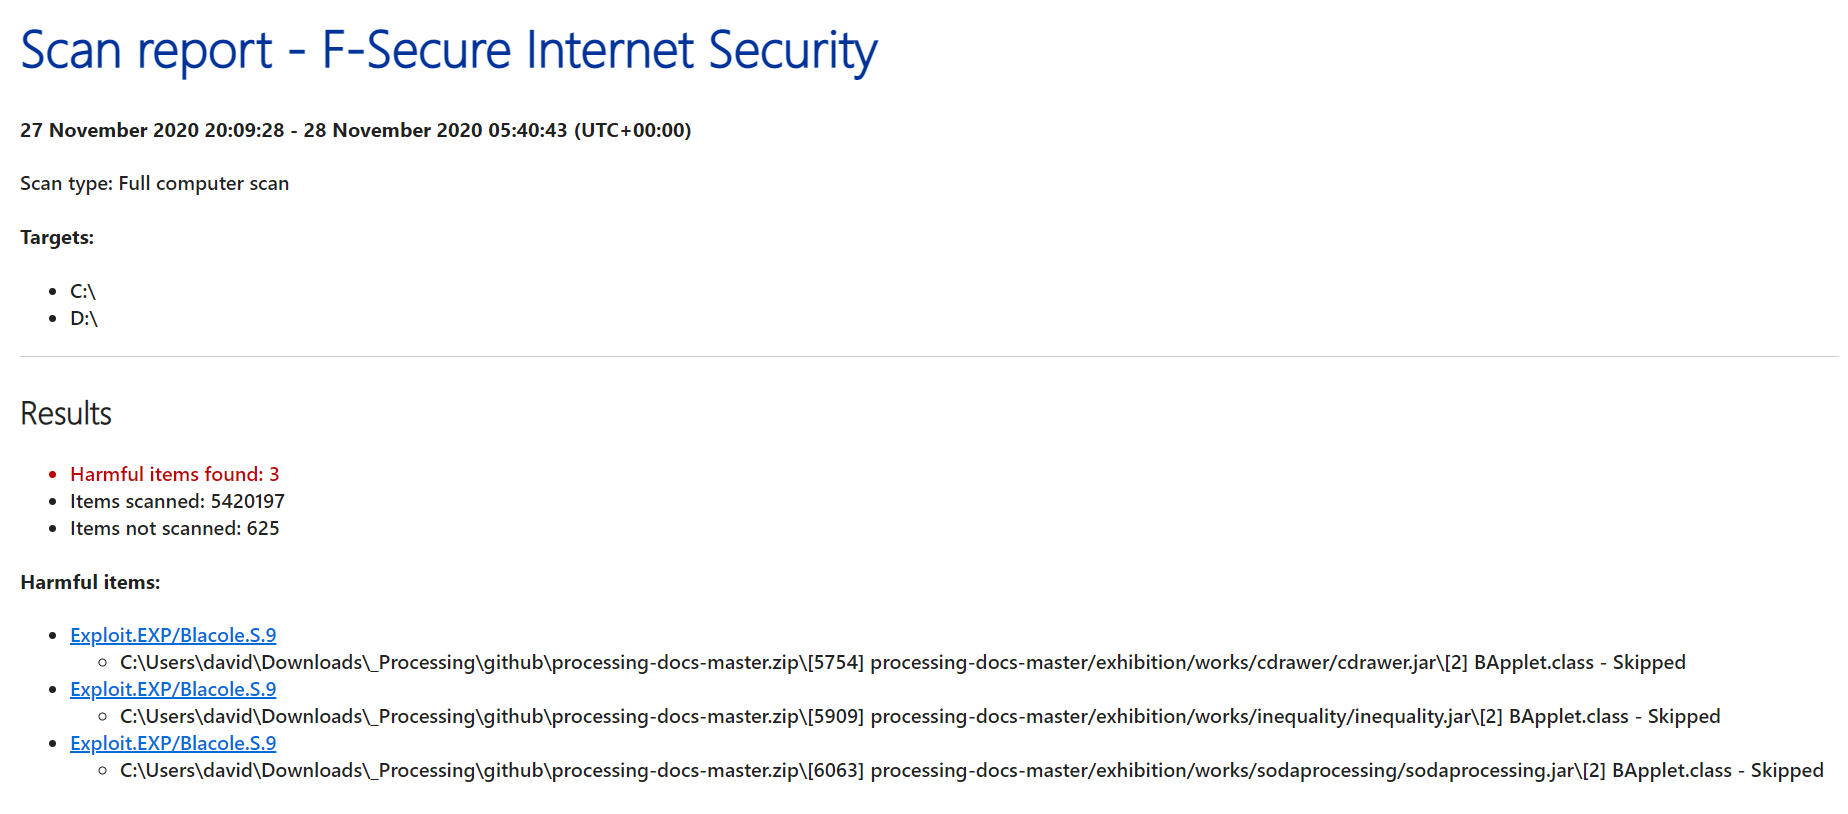
3 specific harmful items found (from the F-Secure report):
Exploit.EXP/Blacole.S.9
processing-docs-master.zip[5754] processing-docs-master/exhibition/works/cdrawer/cdrawer.jar[2] BApplet.class
processing-docs-master.zip[5909] processing-docs-master/exhibition/works/inequality/inequality.jar[2] BApplet.class
processing-docs-master.zip[6063] processing-docs-master/exhibition/works/sodaprocessing/sodaprocessing.jar[2]
Part of an exploit kit: see also:
https://www.f-secure.com/v-descs/exploit_java_blackhole.shtml
F-Secure reported that it was unable to clean the files. I reverted to deleting the zip file.
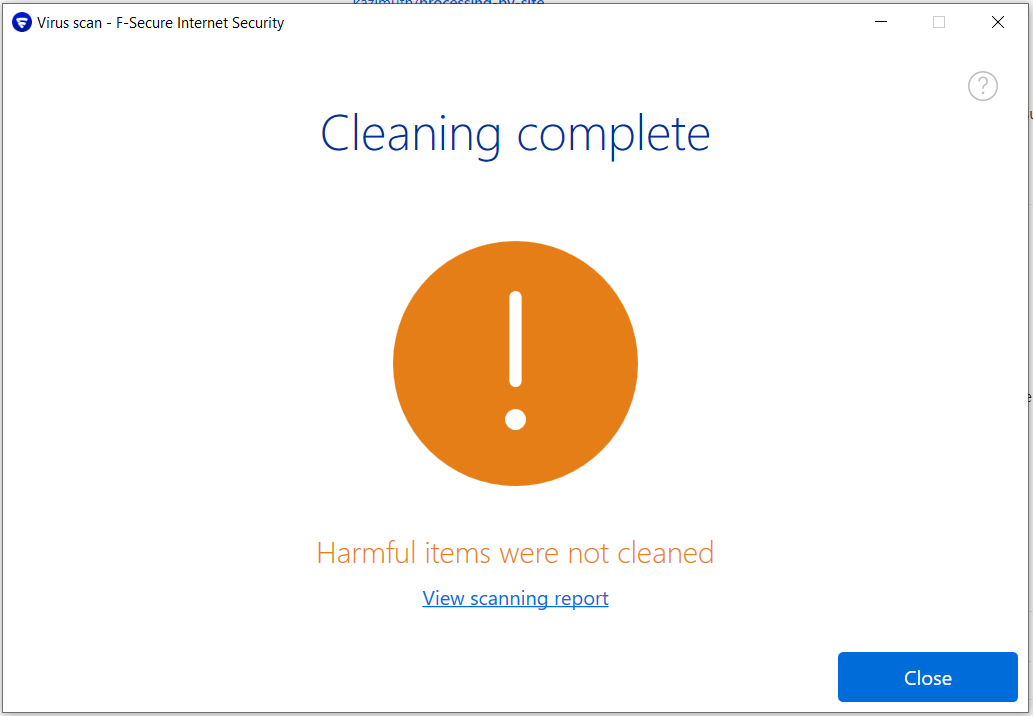
URL(s) of affected page(s)
See above note.
Proposed fix
Author to examine original code files, perhaps send individual files to F-Secure for analysis; remove exploit from affected files if the exploit is real, or modify the code to prevent false negative if that's the case, or post notice that such a false negative exists and can be safely ignored.
I would have sent the zip file to F-Secure for analysis myself, but their file-size limit is 30Mb. I'm not opening the zip file myself just in case this is a real issue.
コントリビューションガイド
このリポジトリのコントリビューションガイドは索引されていません
はじめの一歩
- issue を最後まで読み、次にプロジェクトのコントリビューションガイドを読みます。
- 着手することを issue にコメントします — 二人が同じ作業をするのを防げます。
- リポジトリをフォークし、ブランチを切って変更します。
- issue 番号を参照したプルリクエストを送ります。
調査の方向性
ドキュメントアーカイブにある報告済みの3つのパス、exhibition/works/cdrawer/cdrawer.jar、inequality/inequality.jar、sodaprocessing/sodaprocessing.jarから始め、それぞれのBApplet.classに焦点を当てます。これらのファイルを元のコードと比較し、可能であれば個々のファイルをF-Secureに提出して分析してもらいます。検出が実際のものか誤検知かを確認し、その後、exploitを削除するか、安全な誤検知への対応を文書化すれば完了です。
索引モデルが issue の本文から書いたものです。
評価
- 技術スタック
- java
- 領域
- documentation, security
- issue の種類
- バグ
- 難易度
- 4/5
- 見積もり時間
- 3〜5日
- 活発さ
- 停滞
- 明瞭さ
- おおむね明確
- 初心者へのやさしさ
- 35/100