enhance-dev / enhance-dev/form-elements
Include nonce attribute for Content Security Policy
Open
- Dominant language
- JavaScript
- Stars
- 4
- Forks
- 1
- PR merge metrics
- No merged PRs in 30d
Description
See https://github.com/enhance-dev/enhance-starter-project/issues/12
When a nonce is available, form-elements should include that nonce as an attribute to prevent errors like in this screenshot:
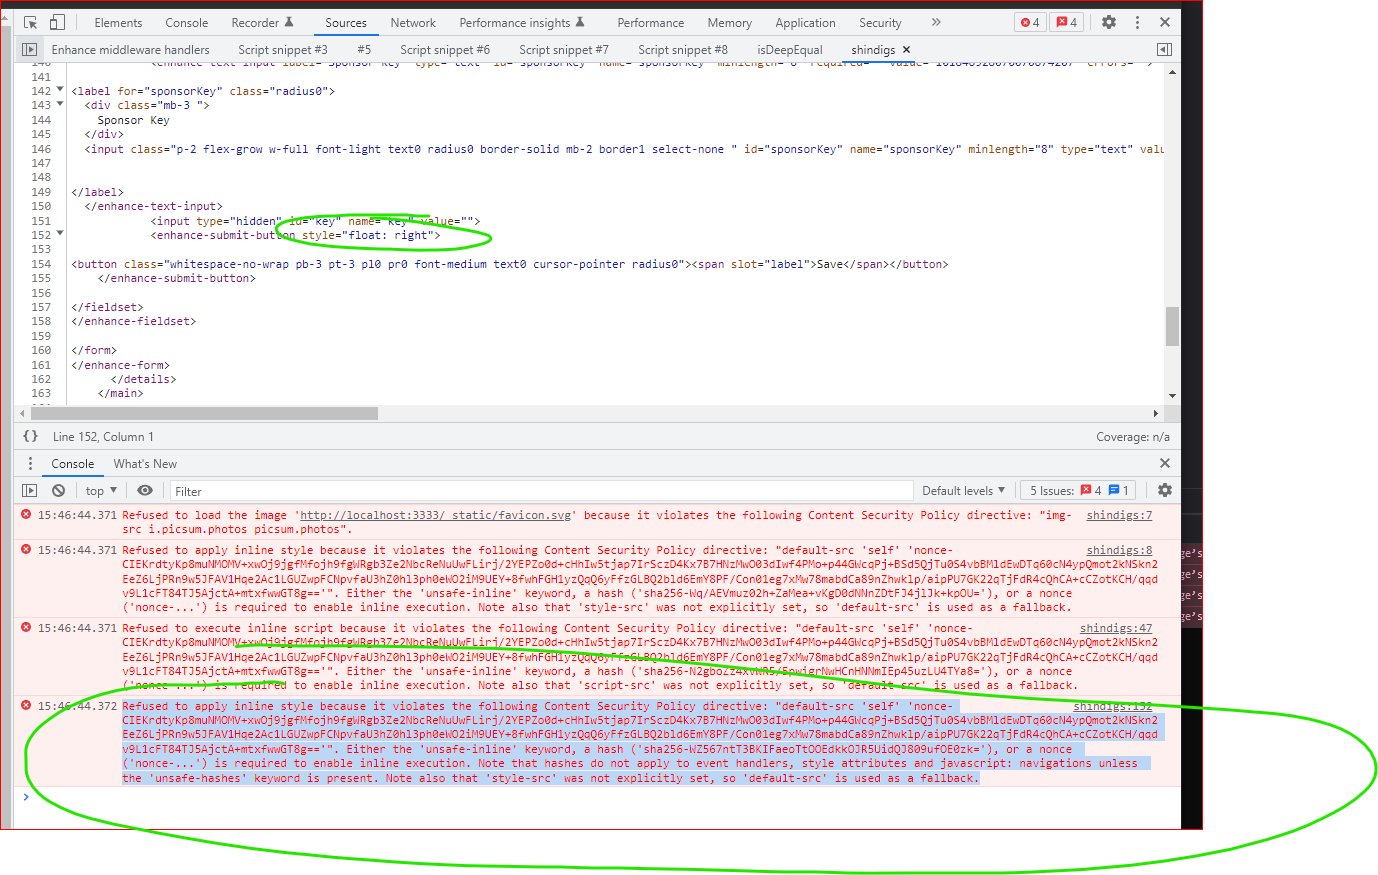
```Refused to apply inline style because it violates the following Content Security Policy directive: "[omitted for brevity]". Either the 'unsafe-inline' keyword, a hash ('sha256-WZ567ntT3BKIFaeoTtOOEdkkOJR5UidQJ809ufOE0zk='), or a nonce ('nonce-...') is required to enable inline execution.```
Contributor guide
Assessment
This issue has not been assessed yet.