alibaba / alibaba/lowcode-engine
引擎能力被 CSP 安全策略阻拦
- Dominant language
- TypeScript
- Stars
- 15.9k
- Forks
- 2.7k
- PR merge metrics
- No merged PRs in 30d
Description
## bug 说明
将下面代码插入到 lowcode-demo 项目 index.ejs 文件 head 标签中即可出现
```html
```
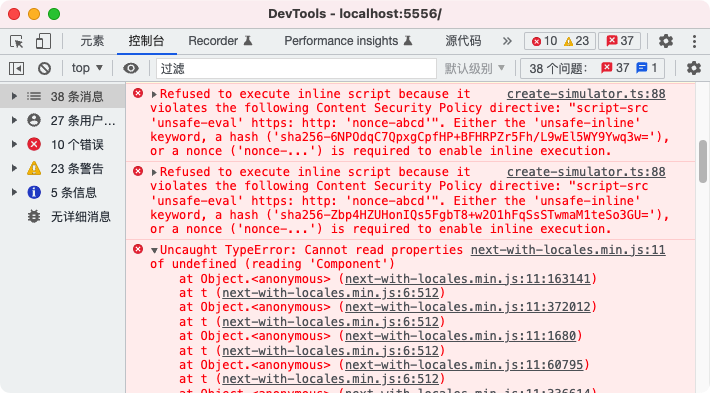
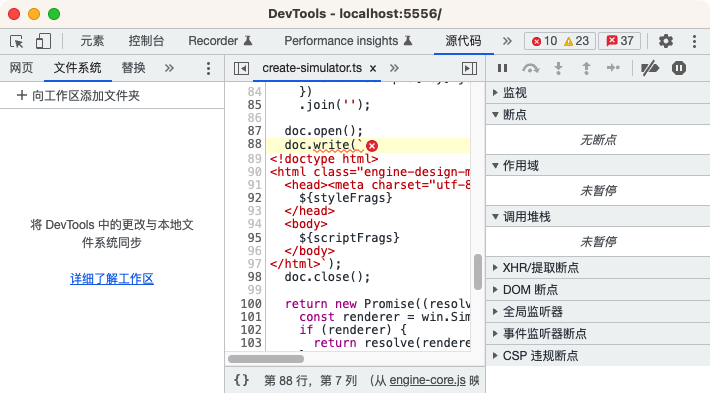
异常具体指向[这一行](https://github.com/alibaba/lowcode-engine/blob/v1.0.14/packages/designer/src/builtin-simulator/create-simulator.ts#L88)。
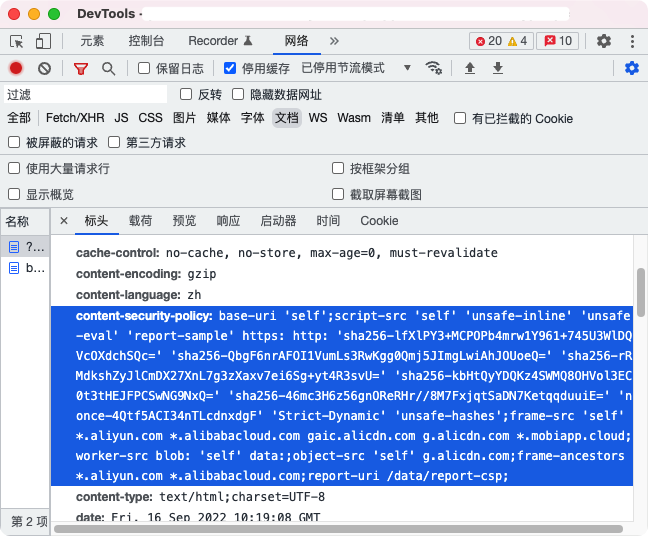
对于页面 HTTP 头有 content-security-policy 设置的,会同样出现上述问题。所以此问题常常是本地开发好了,生产环境挂了
## 期望
Google 对于 document.write 的说明:https://developer.chrome.com/blog/removing-document-write/
期望取消 document.write 的使用,PR 在下方。
Contributor guide
No contributing guide indexed for this repository
Research direction
Reproduce the failure by adding the shown Content-Security-Policy meta tag to lowcode-demo's index.ejs, then inspect packages/designer/src/builtin-simulator/create-simulator.ts at line 88. Replace the document.write usage as requested and verify that the lowcode demo no longer fails under the CSP policy.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- typescript
- Domain
- frontend, security
- Issue type
- Bug
- Difficulty
- 2/5
- Estimated time
- 1-3 hours
- Activity status
- Stale
- Clarity
- Clearly specified
- Newbie friendliness
- 35/100