Configuring Identity Server as IDP for SSO does not cover role mapping for the users other than admin
Nobody has claimed this yet.
- Dominant language
- CSS
- Stars
- 99
- Forks
- 708
- Avg merge
- 1d 7h
- Merged PRs (30d)
- 22
Description
Description:
The documenation does not cover the IDP configuration that works for users other than admin users and how we can map correct roles for the users are provisioned at the APIM [1] in contrast the APIM 260 I've noticed it has a more detailed explanation [2]. We must include points 10-13 as depicted below to the APIM 4.0.0 documentation. Please do needful
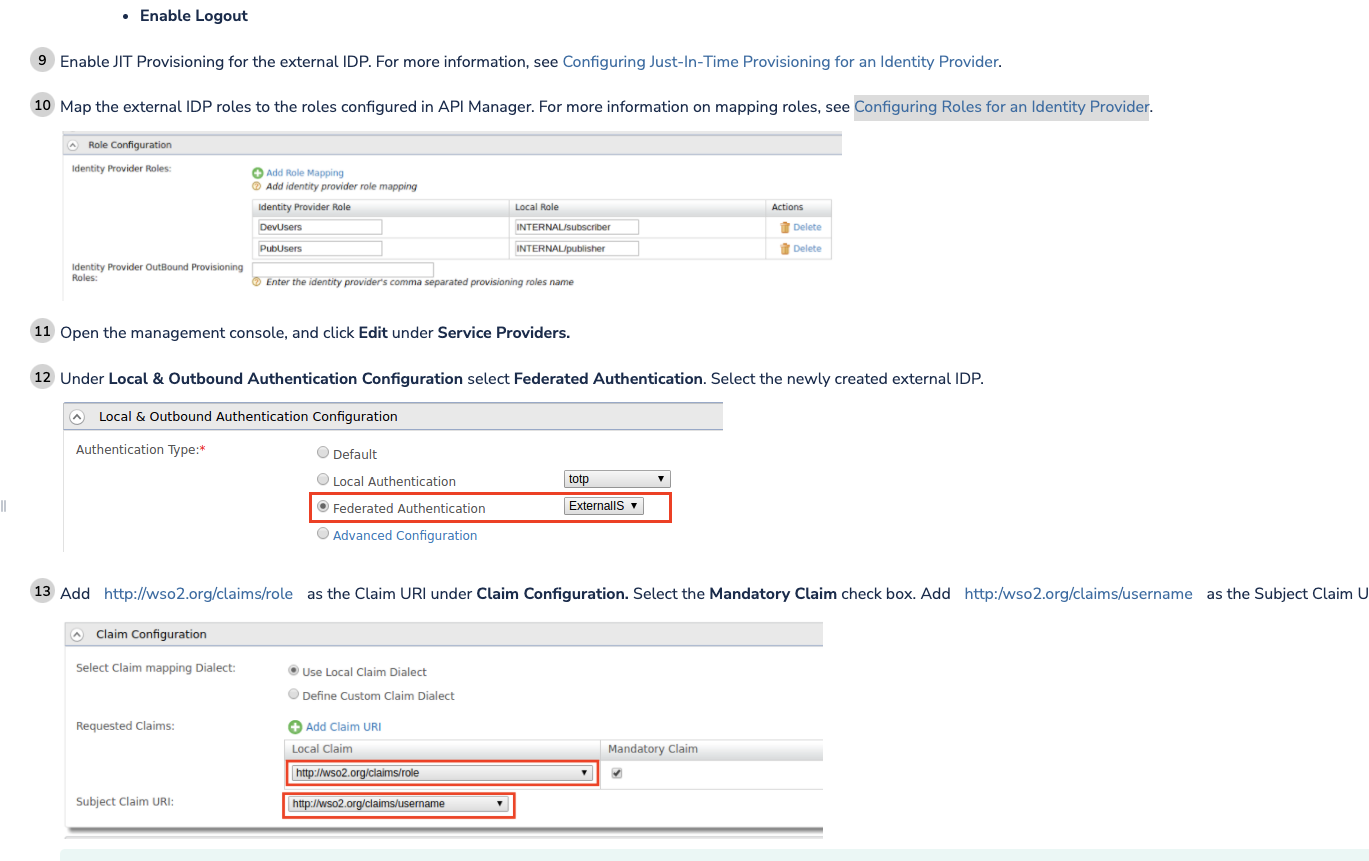
[1] https://apim.docs.wso2.com/en/latest/reference/customize-product/extending-api-manager/saml2-sso/configuring-identity-server-as-idp-for-sso/
[2] https://docs.wso2.com/display/AM260/Configuring+External+IDP+through+Identity+Server+for+SSO
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start with the APIM 4.0.0 documentation page linked as [1] and compare it with the APIM 2.6.0 reference linked as [2]. Add the missing points 10–13 shown in the issue so the guide explains non-admin user provisioning and role mapping; the documentation is done when those users' roles are covered clearly.
Written by the indexing model from the issue text.
Assessment
- Domain
- authentication, authorization, documentation
- Issue type
- Documentation
- Difficulty
- 2/5
- Estimated time
- 1-3 hours
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 48/100