Add a note for Hashicope Vault documentation on how to set policies
Open
@sajithaliyanage is already working on this.
Since Sep 9, 2021.
API-M-4.0.0
Severity/Minor
Type/Bug
- Dominant language
- CSS
- Stars
- 99
- Forks
- 708
- Avg merge
- 1d 7h
- Merged PRs (30d)
- 22
Description
Description:
When Hashicope vault is setup, it is required to create a policy file, provision it and assign it to a role when AppRole Pull authentication is used. In this policy file we need to define the necessary privileges to access the vault entries.
The permission file should be in following format if the secrets are stored as below.
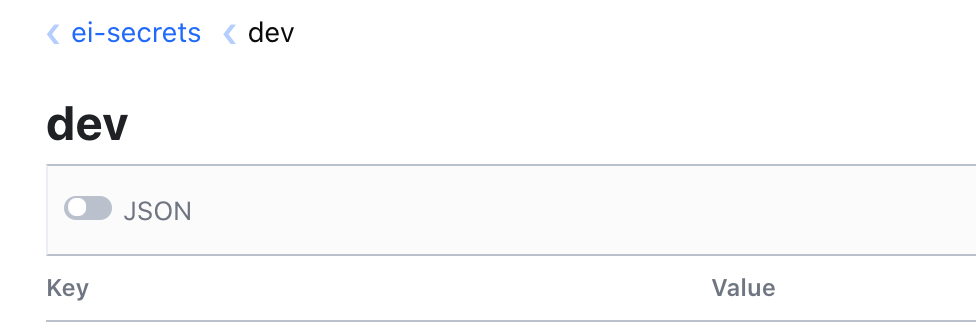
  path "ei-secrets/data/*" {
    capabilities = [ "read", "update" ]
  }
Hence the path takes the format
<Secret Engine Name>/data/<rest of the vault path>/*
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Assessment
This issue has not been assessed yet.