tailscale / tailscale/tailscale
Tagged device UI still shows the user who created the node
- Dominant language
- Go
- Stars
- 36.5k
- Forks
- 3.2k
- Avg merge
- 1d 23h
- Merged PRs (30d)
- 132
Description
### What is the issue?
Here is the configuration:
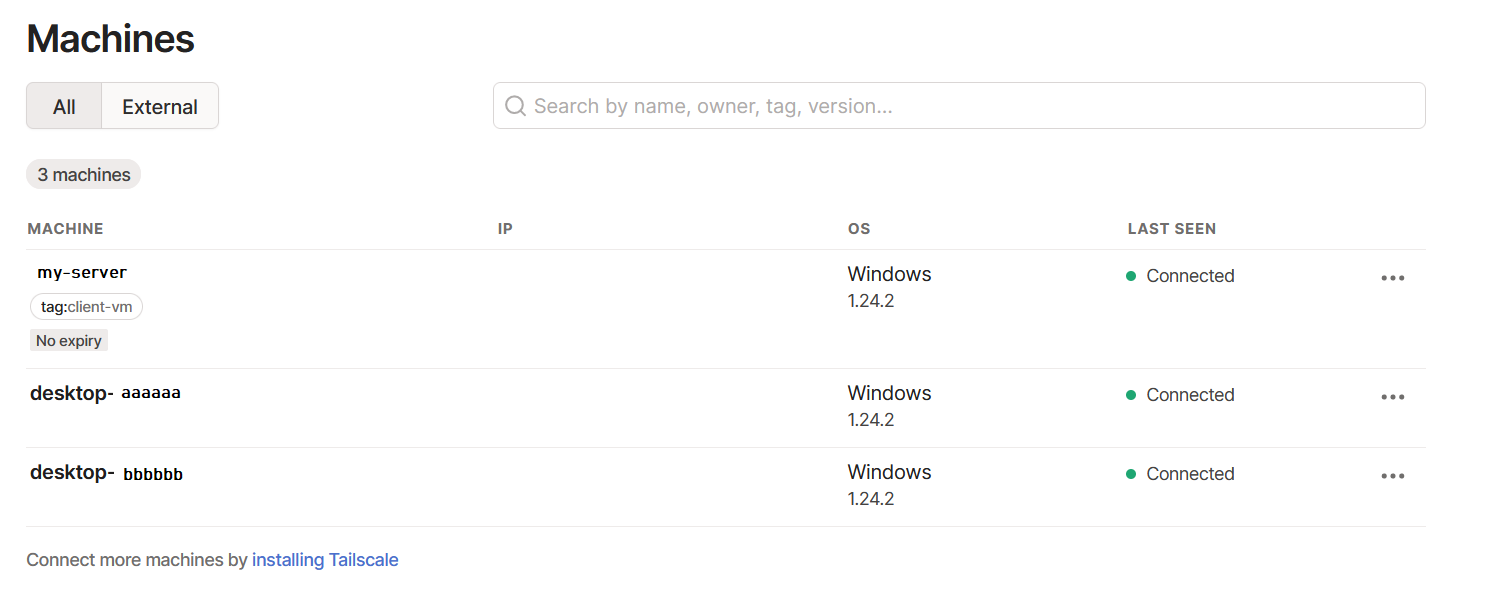
The two `desktop-` machines belong to the user `user@company.com`.
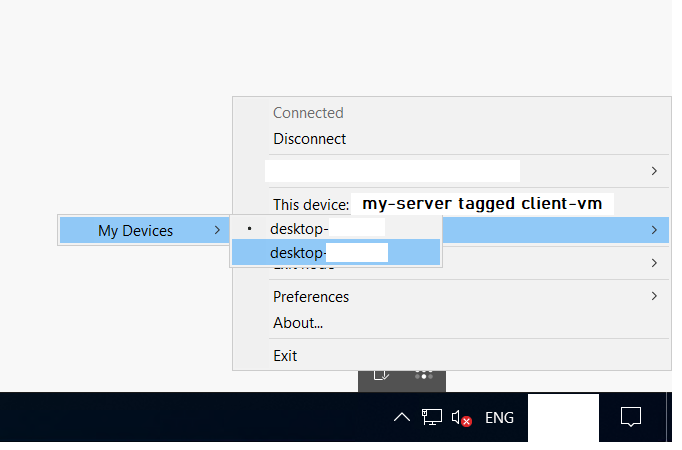
When RDP into `my-server`, in the Taskbar we see this:
This is the ACL I'm using:
```
// Example/default ACLs for unrestricted connections.
{
// Declare static groups of users beyond those in the identity service.
"groups": {
"group:dc-admins": [ "user@company.com" ],
},
// Tags
"tagOwners": {
"tag:client-vm": ["user@company.com"],
},
// Access control lists.
"acls": [
// All employees can access their own devices (i.e. mobile phones)
{ "action": "accept", "src": ["autogroup:members"], "dst": ["autogroup:self:*"] },
// DC-Admins can access the client VMs
{ "action": "accept", "src": ["group:dc-admins"], "dst": ["tag:client-vm:*"] },
]
}
```
My expectation is that the server is tagged, ACLs are deny-by-default, and therefore I should need an ACL line to give access from `client-vm` back to the users' machines. But the machine is inheriting the users' permissions from `user@company.com` and hence able to see their devices included in the group `autogroup:self`.
I consider this to be quite a serious security issue as the server could be used as a bastion to access i.e. the users' personal phones or other devices on a Tailscale network that they may not have realised were included in the ACL.
### Steps to reproduce
_No response_
### Are there any recent changes that introduced the issue?
_No response_
### OS
Windows, Other
### OS version
Pro, Server Standard 2022
### Tailscale version
1.24.2
### Bug report
BUG-9e73d5909f38f1088789709ad7287d617350da7421db67d847081940bad86f99-20220506024959Z-b90acd5cffd19254
Contributor guide
Assessment
This issue has not been assessed yet.