resolved: handle only a whitelist of interfaces
Nobody has claimed this yet.
- Dominant language
- C
- Stars
- 16.7k
- Forks
- 4.7k
- Avg merge
- 1d 6h
- Merged PRs (30d)
- 140
Description
systemd version the issue has been seen with
244
Used distribution
ubuntu
Expected behaviour you didn't see
In a system that extensively works with new ip links, such as extensive work with with containers, systemd-resolved takes 100% CPU
Unexpected behaviour you saw
100% CPU
Steps to reproduce the problem
Run in bash:
while true ; do ip link add veth$RANDOM$RANDOM type veth peer name veth$RANDOM$RANDOM ; done
And see:
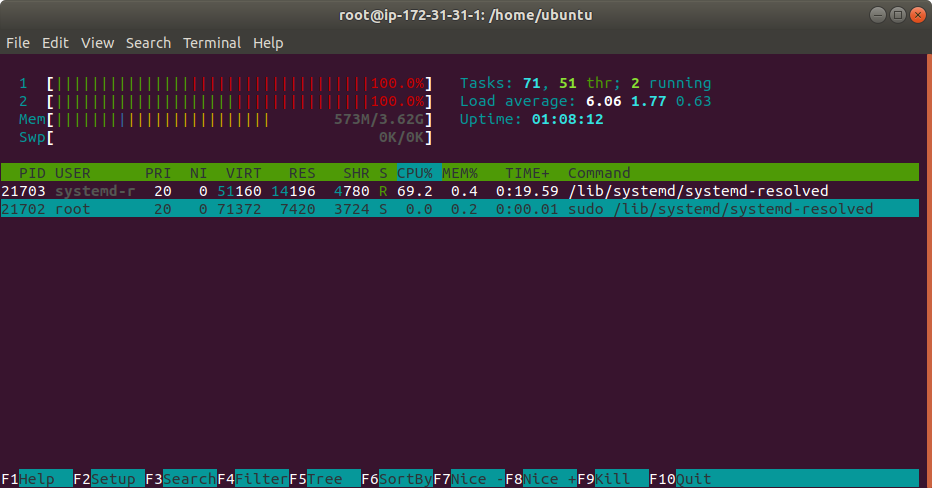
Notice there's no way to opt-out from resolved adding a DNS server to each new network interface in the system.
I'd expect to at least have a flag to have resolved handle only a whitelist of interfaces, or not handle non-physical interfaces.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Reproduce the behavior with the provided bash loop while observing systemd-resolved's CPU use and DNS handling for newly created links. Start by tracing how resolved processes network-interface changes; done should provide a documented way to restrict handling to a whitelist or exclude non-physical interfaces without the reported CPU spike.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- c, linux
- Domain
- networking, operating-systems
- Issue type
- Feature
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 38/100