sameersbn / sameersbn/docker-gitlab
GITLAB_HTTPS, SSL_CERTIFICATE_PATH and mixed content issue
@solidnerd is already working on this.
Since May 11, 2020.
- Dominant language
- Shell
- Stars
- 8.1k
- Forks
- 2.1k
- Avg merge
- 17h 47m
- Merged PRs (30d)
- 7
Description
Hi,
We have HaProxy which handles all http and https requests and have all SSL certs.
Gitlab container is exposing only port 22 and 80. It looks like this:
HaProxy [80] (redirects to https) -> Haproxy[443]
HaProxy[443] (drops ssl) -> Gitlab(Nginx)[80] -> (returns the content to the browser)
We had this problem with mixed content when loading avatarts and build logs.
Avatarts requests were redirected from http to https by haproxy and were resolved by the browser so it was fine (just warnings)
But the build logs json files requests over http were blocked by the browser as they are XMLHttpRequest requests and browsers does not let you make XMLHttpRequest to http if page is loaded over https.
Haproxy did not even received that http request as browser was cancelling it.

Command that I tried first to spawn gitlab (I removed stuff that is not related):
/usr/bin/docker run \
  -p 22:22 \
  --link redis:redisio \
  -e 'GITLAB_HOST=gitlab.mydomain.com' \
  -e 'GITLAB_HTTPS=true' \
  --volume-driver=convoy \
  -v gitlab_mgmt:/home/git/data/ \
  -v gitlab_log_mgmt:/var/log/gitlab \
  -v gitlab_certs:/certs \
  --name=gitlab \
  sameersbn/gitlab:9.2.2
Command that we use NOW to spawn gitlab (I removed stuff that is not related):
/usr/bin/docker run \
  -p 22:22 \
  --link redis:redisio \
  -e 'GITLAB_HOST=gitlab.mydomain.com' \
  -e 'GITLAB_HTTPS=true' \
  -e 'SSL_CERTIFICATE_PATH=/this_path_must_not_exits_for_https_to_work_properly' \
  -e 'SSL_KEY_PATH=/this_path_must_not_exits_for_https_to_work_properly' \
  -e 'SSL_DHPARAM_PATH=/this_path_must_not_exits_for_https_to_work_properly' \
  --volume-driver=convoy \
  -v gitlab_mgmt:/home/git/data/ \
  -v gitlab_log_mgmt:/var/log/gitlab \
  -v gitlab_certs:/certs \
  --name=gitlab \
  sameersbn/gitlab:9.2.2
PROBLEM IS:
If I just set GITLAB_HTTPS=true and omit UNSETING (or setting them to a path that does not exist) SSL_CERTIFICATE_PATH SSL_KEY_PATH SSL_DHPARAM_PATH then /etc/nginx/sites-enabled/gitlab nginx configuration file is wrong (in our use case) because of this nested if statement:
https://github.com/sameersbn/docker-gitlab/blob/master/assets/runtime/functions#L1307

SSL_CERTIFICATE_PATH SSL_KEY_PATH SSL_DHPARAM_PATH are being set to default values here:
https://github.com/sameersbn/docker-gitlab/blob/master/assets/runtime/env-defaults#L131
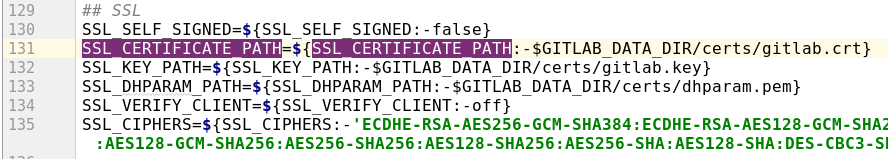
There are some (default) files in the location those three variables are pointing when you start the container so the wrong nginx configuration file was being copied (which redirects calls from port 80 to 443). This makes an infinite loop of 301 redirects when I tried our gitlab external url. It looked something like this:
HaProxy[443] (drops ssl) -> Gtilab(Nginx)[80] (Nginx now redirects to 443) -> Haproxy[443] -> (drops ssl) -> Gtilab(Nginx)[80] -> the cycle continue indefinitely...
I set those three variables to a folder that does not exist (as can be seen in the docker run command above) and the mixed content warnings/errors disappeared and everything seems to be working fine. Now the right (for our use case) nginx config file is being copied by the functions shell script (which now makes nginx to serve on port 80 only).
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Assessment
This issue has not been assessed yet.