[Bug]: New Codex runtime entries can disable existing shadow-home providers
Nobody has claimed this yet.
- Dominant language
- TypeScript
- Stars
- 23k
- Forks
- 5.9k
- Avg merge
- 11h 14m
- Merged PRs (30d)
- 357
Description
Summary
T3's Codex shadow-home setup only links entries that already exist in the shared home when materialization runs. If a later Codex update creates a new top-level runtime entry in both the shared and shadow homes, the next materialization rejects the shadow copy and disables the provider.
Codex 0.147 introduced queue_1.sqlite, which triggers this today. The same failure can recur when Codex adds another home entry.
Reproduction
- Configure the documented multi-account layout: one shared
homePathand another account using thathomePathplus a separateshadowHomePath. - Start with no
queue_1.sqlitein either home and let T3 materialize the shadow home. - Run Codex 0.147 against both effective homes. Codex creates a regular queue database in each.
- Refresh provider status or restart T3.
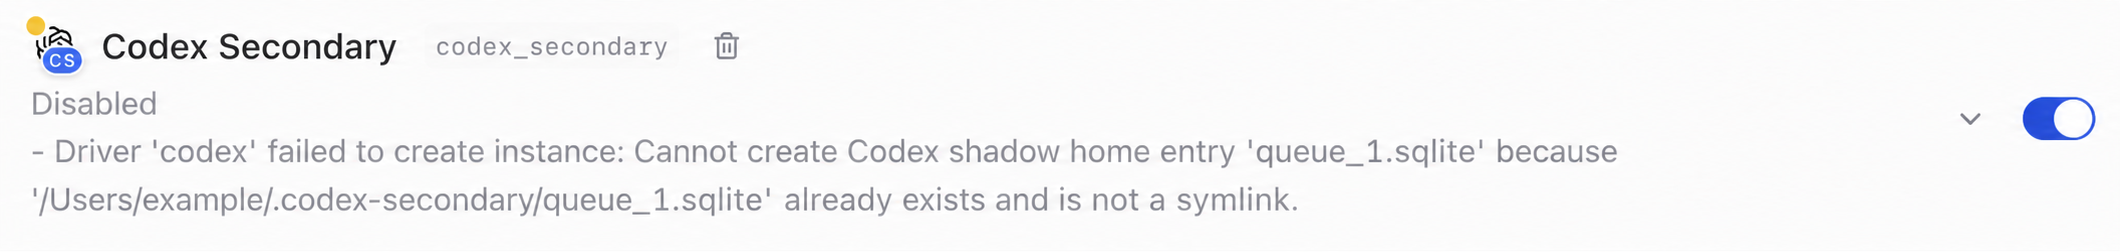
The shadow-home provider becomes disabled:
Driver 'codex' failed to create instance: Cannot create Codex shadow home entry 'queue_1.sqlite' because '<shadow-home>/queue_1.sqlite' already exists and is not a symlink.
A minimal unit repro is to create regular sharedHome/queue_1.sqlite and shadowHome/queue_1.sqlite files, then call materializeCodexShadowHome(layout).
Why it happens
T3 lists the current shared-home entries, then ensureSymlink rejects any existing regular shadow entry. There is no recovery path; the conflict becomes a provider creation error.
Codex added the queue DB in openai/codex@b87981a. In the affected installation, the shared DB and two shadow DBs were automatically created within six seconds, confirming this was runtime-created state rather than a copied home.
Expected behavior
Codex upgrades that add runtime entries should not disable existing shadow-home providers. T3 should reconcile ownership safely or offer a targeted recovery path without silently deleting user data.
Acceptance criteria
- New Codex home entries created after an earlier materialization do not leave providers disabled.
- The solution is resilient to future filenames rather than only adding
queue_1.sqliteto an allowlist. - Existing data is preserved; SQLite families such as the base DB, WAL, and SHM are handled together.
- Tests cover creation between materialization passes and an existing regular shadow entry.
Environment
- T3
mainat1a003e383ac6b10258b8100c2617d938c4f06c69 - Codex CLI 0.147.0
- macOS 26.5.2, Apple Silicon
Workaround
With related processes stopped, backing up and removing the shadow queue_1.sqlite, queue_1.sqlite-wal, and queue_1.sqlite-shm files allows T3 to create the shared link. This is manual, potentially data-destructive, and does not address future Codex entries.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start in apps/server/src/provider/Drivers/CodexHomeLayout.ts, reading materializeCodexShadowHome and ensureSymlink at the referenced lines. Reproduce the issue with regular queue_1.sqlite files in sharedHome and shadowHome, then add unit coverage for entries created between materialization passes and existing regular shadow entries. Done means future runtime-created entries are reconciled without disabling providers or losing SQLite-related data.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- sqlite, typescript
- Domain
- backend, databases
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Quiet
- Clarity
- Mostly clear
- Newbie friendliness
- 52/100