If the key(id_rsa) mutual trust file in the tiup home directory is wrong, the -i(id_rsa) specified key deployment will not overwrite it again
Open
Nobody has claimed this yet.
type/bug
- Dominant language
- Go
- Stars
- 466
- Forks
- 338
- Avg merge
- 3d 7h
- Merged PRs (30d)
- 8
Description
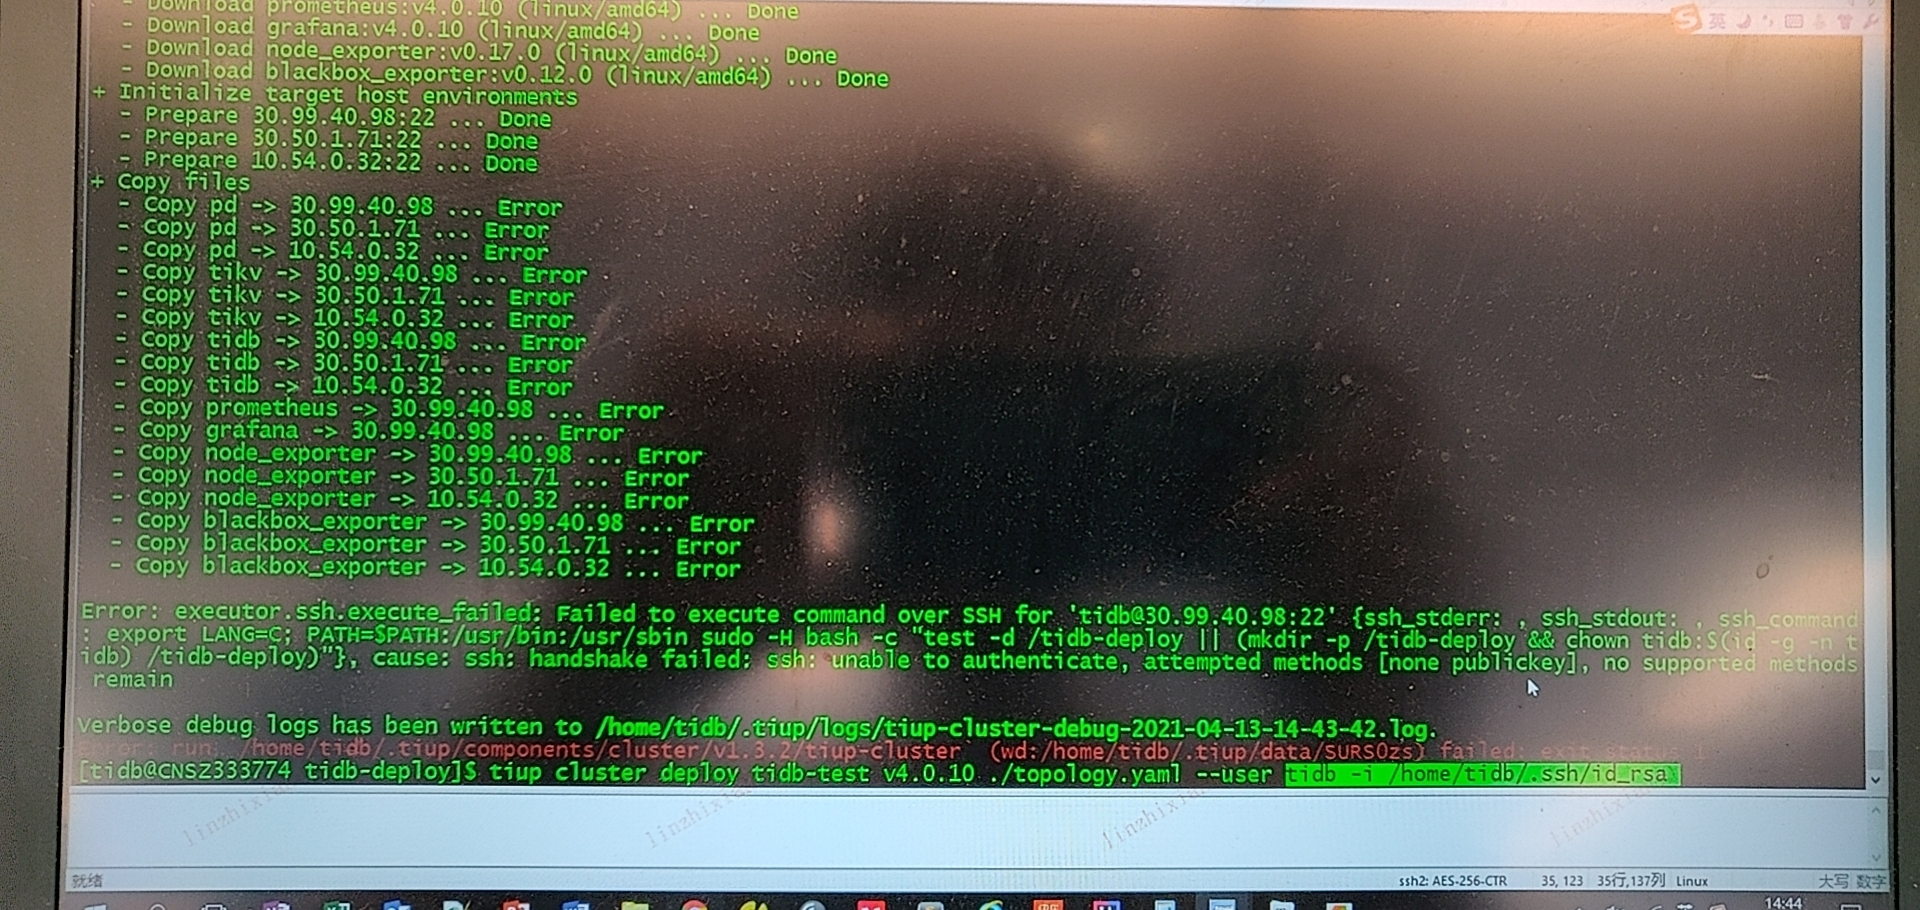
在初次指定错误的秘钥的情况下 -i 部署集群,部署会失败,同时会在 .tiup/storage/xxx/ssh/ 下生成对应的私钥。
而后如果 deploy 部署的时候指定上正确的秘钥,该目录不会被覆盖,
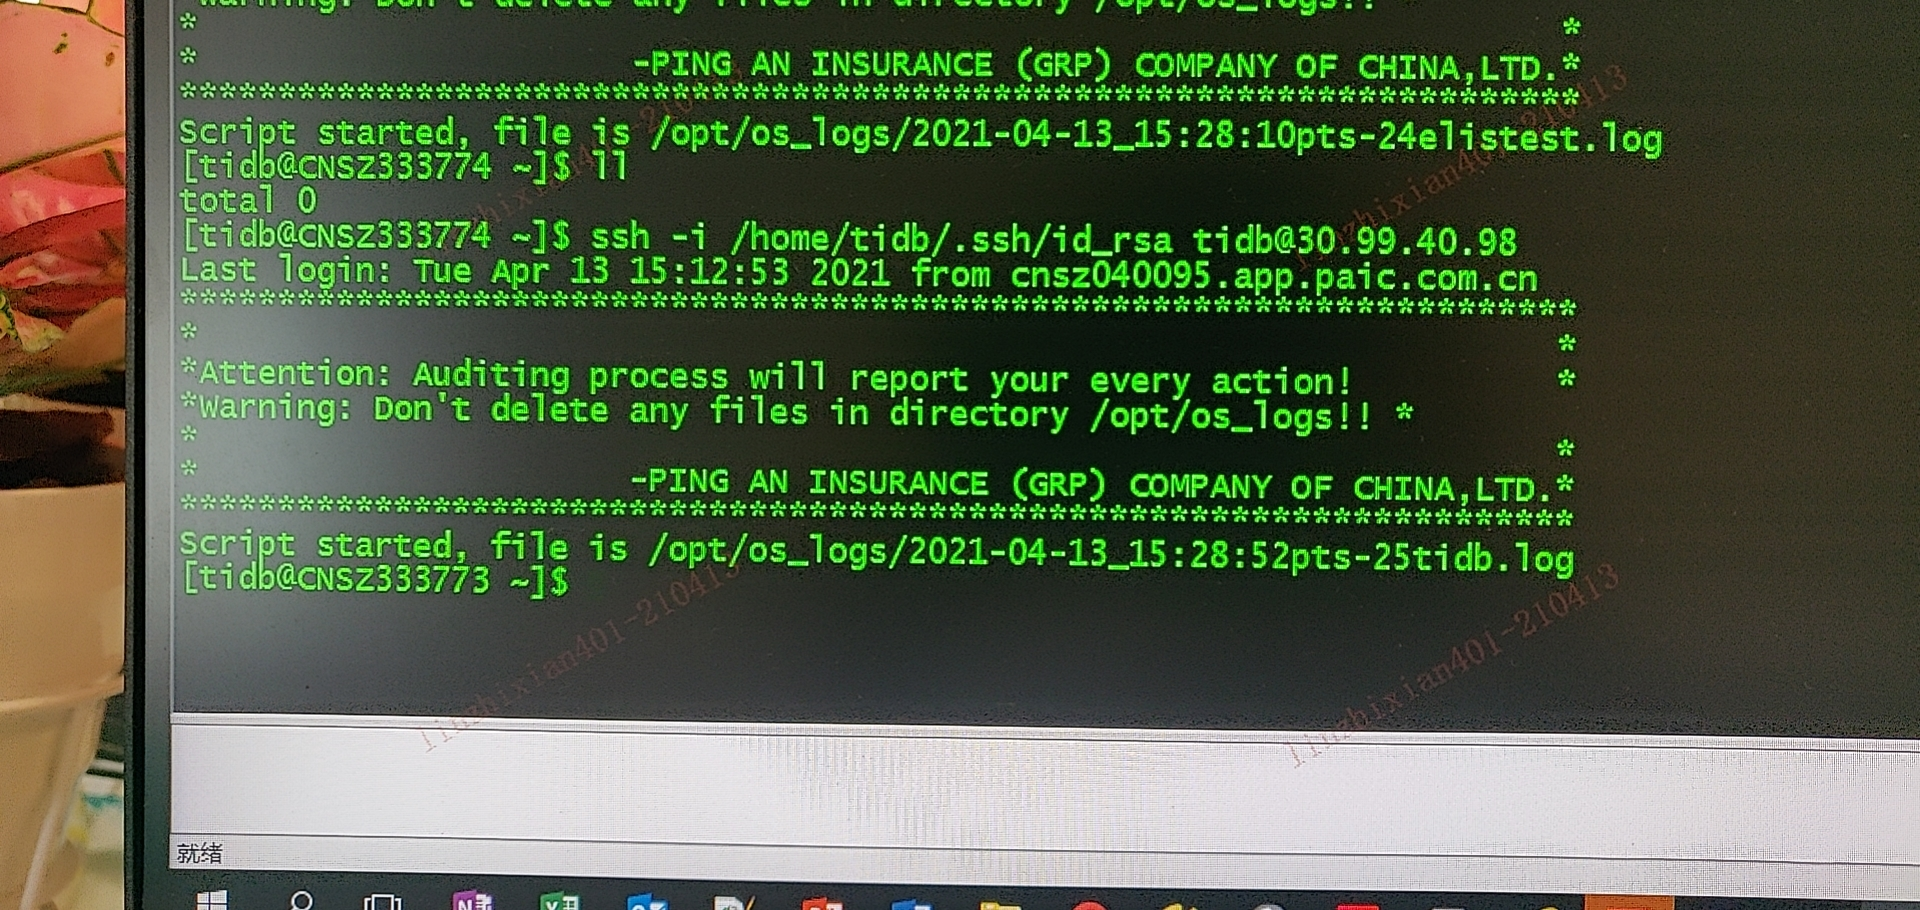
这样会产生一个问题,我的终端 ssh -i id_rsa tidb@xxx 到目标均正常,但是 deploy 却失败。

Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Reproduce the two-step deployment using an incorrect key and then a corrected -i key. Inspect the key handling around the deploy entry point and the generated .tiup/storage/xxx/ssh/ directory. Done means a second deploy uses the corrected key instead of retaining the earlier private key, and the deployment succeeds when direct SSH succeeds.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- go
- Domain
- cli, devops
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 38/100