[QA] username and password fields are not forwarded to kopano IDM
Open
Nobody has claimed this yet.
QA:team
UX
- Dominant language
- PHP
- Stars
- 8.8k
- Forks
- 2.1k
- Avg merge
- 20h 7m
- Merged PRs (30d)
- 41
Description
seen while testing 2.1.1 - but not a regression, same with earlier versions
- admin enters his username and password in the owncloud login page.
- admin hits the 'Login' button, login succeeds. OK
- ldap user enters his username and password in the owncloud login page.
- ldap user hits the 'Kopano' button, his credentials are wiped out. BAD.
- he has to enter them again. then the login succeeds via IDP.

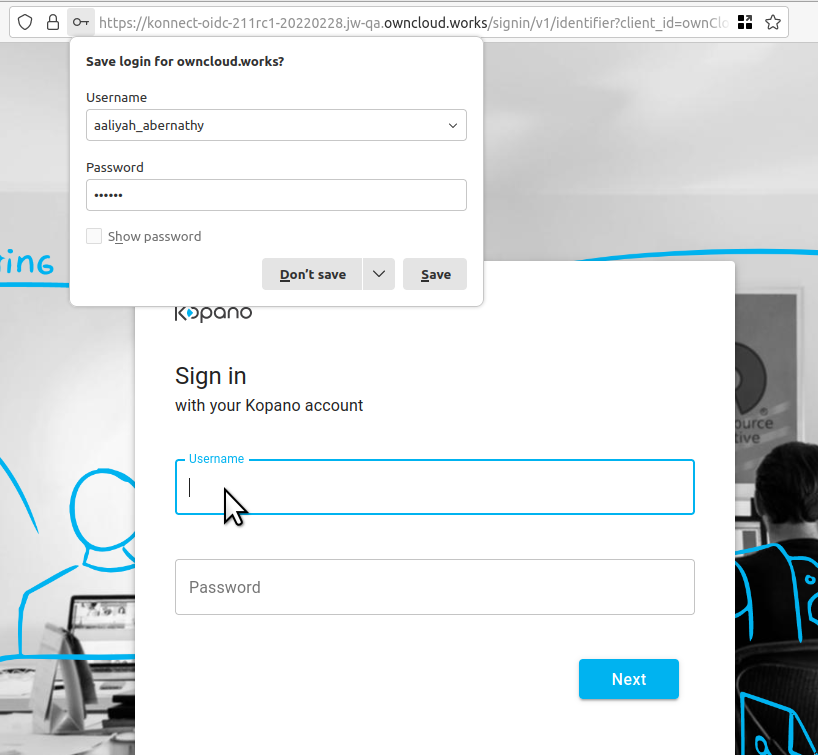
Expected behaviour:
- UX-background: As both buttons 'Login' and 'Kopano' are styled identical and one is advertised as an alternative to the other, it is reasonable that users assume the actions on this page are identical in both cases.
- The kopano login expects that the login data are only entered after hitting the 'Kopano' button, but not before. In case the user has entered them before, they should be pre-filled into the IDP-login page.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start with the ownCloud login page and trace the Login and Kopano button flows into the IDP-login page, reproducing the credential-clearing behavior described. Done means credentials entered before selecting Kopano are preserved and pre-filled in the IDP login flow, while the existing Login flow still succeeds.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- javascript, php
- Domain
- authentication, frontend
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Quiet
- Clarity
- Mostly clear
- Newbie friendliness
- 52/100