Vulnerability type Click Jacking
Nobody has claimed this yet.
- Dominant language
- TypeScript
- Stars
- 457
- Forks
- 272
- Avg merge
- 13h 33m
- Merged PRs (30d)
- 23
Description
Hi team,
This time i founded this vulnerability in your website:
https://nuxtjs.org/
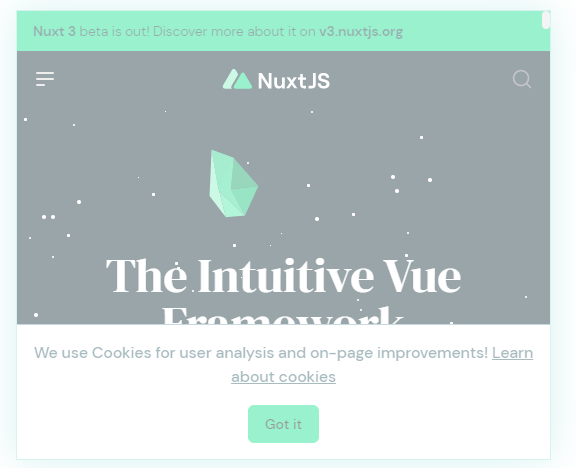
Click jacking (User Interface redress attack, UI redress attack, UI redressing) is a malicious technique of tricking a Web user into clicking on something different from what the user perceives they are clicking on, thus potentially revealing confidential information or taking control of their computer while clicking on seemingly innocuous web pages.
The server didn't return an X-Frame-Options header which means that this website could be at risk of a click jacking attack. The X-Frame-Options HTTP response header can be used to indicate whether or not a browser should be allowed to render a page in a or <iframe>. Sites can use this to avoid click jacking attacks, by ensuring that their content is not embedded into other sites.
This vulnerability affects Web Server.
Here are the steps to reproduce the vulnerability:
1.open notepad and paste the following code.
<title>i Frame</title>This is clickjacking vulnerable
<iframe src=" https://nuxtjs.org/ " frameborder="2 px" height="500px" width="500px"></iframe>2.save it as .html eg s.html
3.and just simply open that...
OR
Copy the link below and paste on your updated browser (Chrome,Firefox).
https://clickjacker.io/test?url=https://nuxtjs.org/
As far as i know this data is enough to prove that your site is vulnerable to Click jacking
according to OWASP its more than enough.
https://www.owasp.org/index.php/Testing_for_Clickjacking_(OWASP-CS-004)
SOLUTION:
https://www.owasp.org/index.php/Clickjacking_Defense_Cheat_Sheet
Check this out and here is the solution for that.
I Hope that you will fix this issue as soon as possible. Looking forward to hear from you. Thank you
Sincerely,
Hassan Raza
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by checking the response headers for https://nuxtjs.org/ and identify where the nuxt.com deployment controls them. Confirm the reported framing behavior in a browser, then verify that the deployed site prevents unintended framing; no file or test is named in the issue.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- nuxt
- Domain
- security, web-dev
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100