nextcloud / nextcloud/user_saml
debugging user_saml ipsilon uesr not provisioned error
Open
Nobody has claimed this yet.
- Dominant language
- PHP
- Stars
- 104
- Forks
- 85
- Avg merge
- 1d 15h
- Merged PRs (30d)
- 16
Description
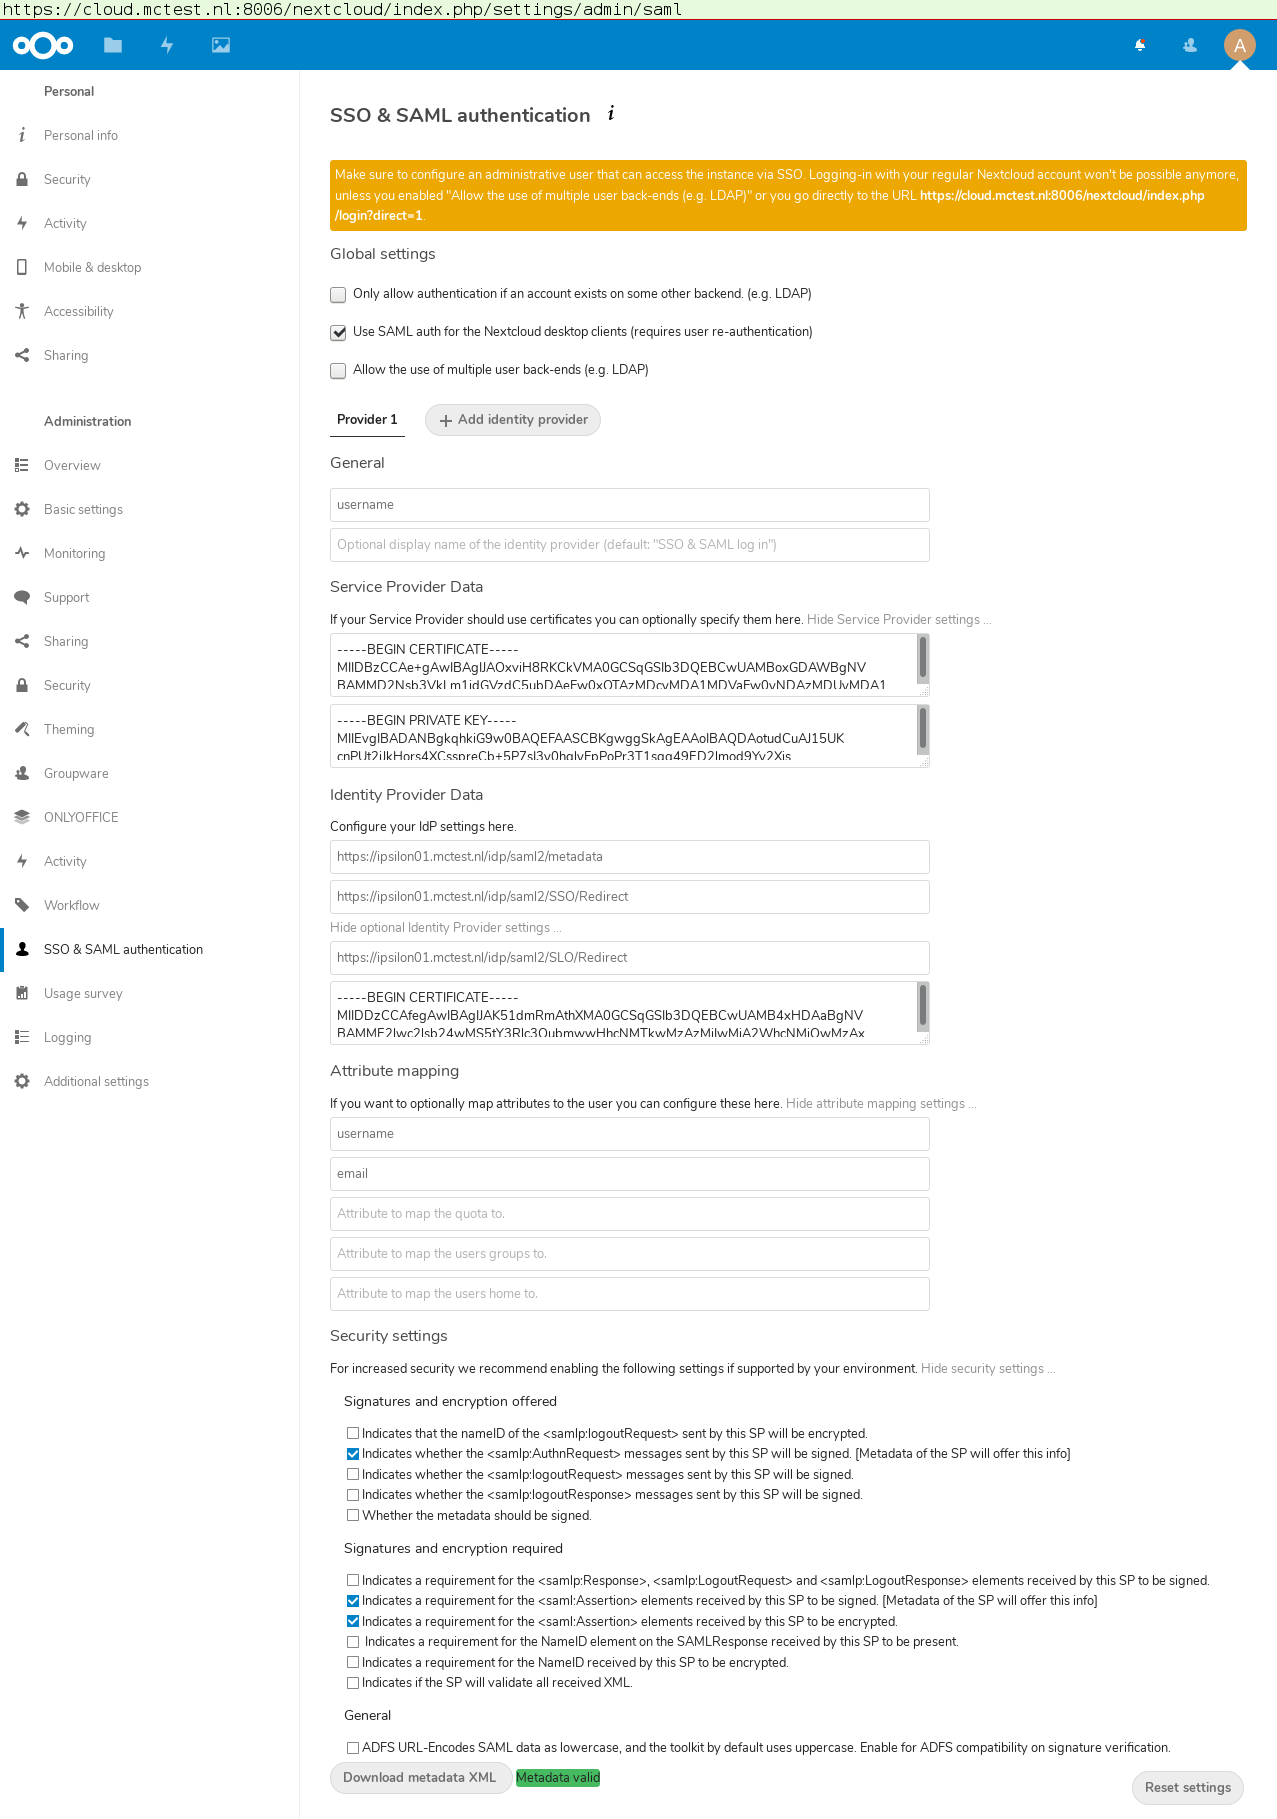
- I would like to know how to debug what user_saml headers are recieving from my IdP?
- should the return response from my IdP go to
https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/metadata
or
https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/sso
or
something else?
The user_saml matadata returned buy default to https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/metadata
but hat did not seems right i think?
When my IdP returns I get an "Account not proviioned" error
<?xml version="1.0"?>
<md:EntityDescriptor xmlns:md="urn:oasis:names:tc:SAML:2.0:metadata" validUntil="2019-03-09T21:48:42Z" cacheDuration="PT604800S" entityID="https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/sso">
  <md:SPSSODescriptor AuthnRequestsSigned="true" WantAssertionsSigned="true" protocolSupportEnumeration="urn:oasis:names:tc:SAML:2.0:protocol">
    <md:KeyDescriptor use="signing">
      <ds:KeyInfo xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
        <ds:X509Data>
          <ds:X509Certificate>snip</ds:X509Certificate>
        </ds:X509Data>
      </ds:KeyInfo>
    </md:KeyDescriptor>
    <md:KeyDescriptor use="encryption">
      <ds:KeyInfo xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
        <ds:X509Data>
          <ds:X509Certificate>snip</ds:X509Certificate>
        </ds:X509Data>
      </ds:KeyInfo>
    </md:KeyDescriptor>
    <md:SingleLogoutService Binding="urn:oasis:names:tc:SAML:2.0:bindings:HTTP-Redirect" Location="https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/sls"/>
    <md:NameIDFormat>urn:oasis:names:tc:SAML:1.1:nameid-format:unspecified</md:NameIDFormat>
    <md:AssertionConsumerService Binding="urn:oasis:names:tc:SAML:2.0:bindings:HTTP-POST" Location="https://cloud.mctest.nl:8006/nextcloud/index.php/apps/user_saml/saml/acs" index="1"/>
  </md:SPSSODescriptor>
</md:EntityDescriptor>
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start with the supplied SAML metadata XML, especially the entityID and AssertionConsumerService URL, and compare those endpoints with the IdP configuration. Then inspect the returned SAML headers and account-provisioning settings to determine why the user is rejected; done means identifying the correct response endpoint and the cause of the provisioning error.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- php
- Domain
- authentication, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 20/100