nextcloud / nextcloud/user_saml
Unable to get admin user once user_saml is enabled (making it hard to integrate File Access Control App alongside user_saml)
Nobody has claimed this yet.
- Dominant language
- PHP
- Stars
- 104
- Forks
- 85
- Avg merge
- 1d 15h
- Merged PRs (30d)
- 16
Description
I am using the SSO & SAML authentication app. But this does not provide a way to have an extra "admin" user.
Thus I turn off this app via "sudo -u www-data php console.php app:disable user_saml" on the nextcloud server each time I want to do admin work (which allows me to sign in using the initial admin account).
The problem now is, I have integrated the file access control app too. But to add configurations, it requires me to sign in as the admin user, which means this drop down menu only shows admin:
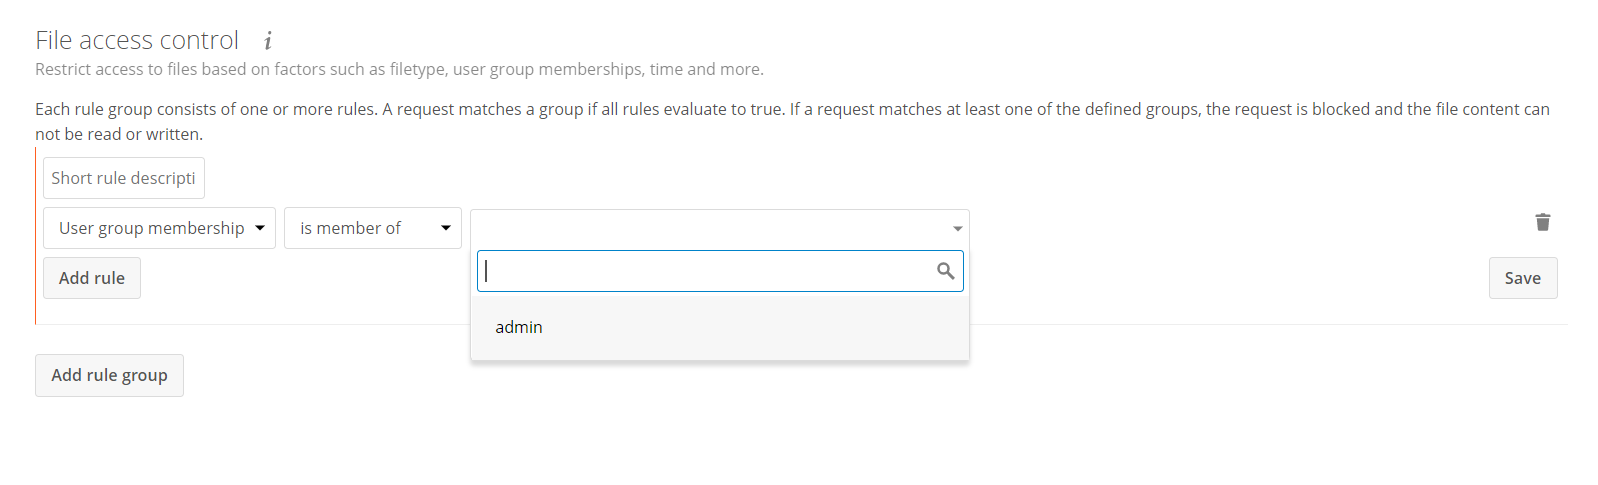
Is there a workaround for this?
Is there a way to get an admin user that is "extra" when SSO & SAML plugin is enabled?
Any ideas would be helpful.
I am using the Nextcloud AWS AMI here: https://aws.amazon.com/marketplace/pp/B06ZZXYKWY
Latest VersionNextCloud-V12.0.0-IVCISA
Operating SystemLinux/Unix, Ubuntu 16.04.2
Delivery Method64-bit Amazon Machine Image (AMI) (Read more)
SupportSee details below
AWS Services RequiredAmazon EC2, Amazon EBS
Highlights
NextCloud integrates Authentication Support (LDAP / Active Directory, SSO / SAML 2.0, Kerberos, Two-factor authentication).
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
The report involves the user_saml and File Access Control apps but names no source files, tests, or entry points. Start by reproducing the missing-admin behavior with SAML enabled and reviewing how administrative access is determined. Done means defining and validating a supported way to perform File Access Control administration without disabling SAML.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- php
- Domain
- authentication, authorization
- Issue type
- Feature
- Difficulty
- 5/5
- Estimated time
- Over a week
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 20/100