Force app password generation on places where there is a link to access non web Nextcloud resources
Nobody has claimed this yet.
- Dominant language
- PHP
- Stars
- 36.9k
- Forks
- 5.2k
- Avg merge
- 2d 3h
- Merged PRs (30d)
- 713
Description
How to use GitHub
- Please use the 👍 reaction to show that you are interested into the same feature.
- Please don't comment if you have no relevant information to add. It's just extra noise for everyone subscribed to this issue.
- Subscribe to receive notifications on status change and new comments.
Is your feature request related to a problem? Please describe.
Given a Nextcloud instance with only SAML login, when I want to use standard non web protocoles (webdav, cardav, caldav) I can't use my regular password, and I need to generate an app password.
Describe the solution you'd like
It would be nice, on places where the webdav link is present (or carddav, caldav), that the UX forces the user to generate an app password directly.
For instance this is how the webdav link looks like:
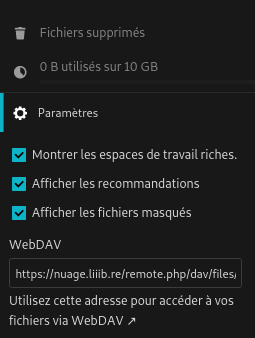
If only SSO is activated, it would be nice to force the user to generate an app password at this place, and then the user would get:
- username
- password
- url
Describe alternatives you've considered
We have docuemntation at this point for this issue, but I think this is the most opened issue on our side.
Additional context
This of course applies only in the case of sso, although, using app password could be considered a good practice in any case.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by tracing the places where WebDAV, CardDAV, or CalDAV links are shown and the existing app-password generation flow. The change is complete when SSO-only users can generate an app password there and receive the username, password, and resource URL.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- php
- Domain
- authentication
- Issue type
- Feature
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 38/100