Simplify OAuth2 login flow
Nobody has claimed this yet.
- Dominant language
- PHP
- Stars
- 36.9k
- Forks
- 5.2k
- Avg merge
- 2d 3h
- Merged PRs (30d)
- 713
Description
Is your feature request related to a problem? Please describe.
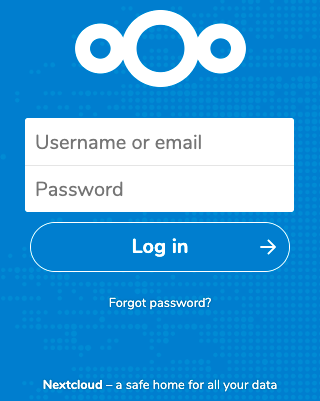
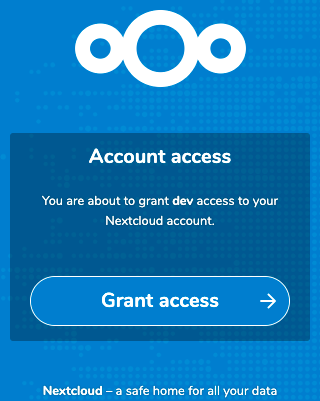
When user trying to login using OAuth2 client, he sees three screens:
- authpicker page
- login page
- grant page
First is completely useless (#17136), third must be showed only one time.
Describe the solution you'd like
I suggest to create table to store scopes that user has granted to client and skip grant page if no new scopes were requested. Also user must be able to revoke access to some or all scopes through web ui.
Describe alternatives you've considered
Alternatively we can check scopes from previous sessions (column scope in authtoken table).
I would like to create PR, but firstly I want to discuss need I create new table or use authtoken. Personally I prefer first variant because (1) authtoken doesn't have client id (only name) (2) even if user revokes all sessions it doesn't mean that user want to revoke access for client, so sessions and scopes must be stored separately (3) oauth sessions have small expiration period (1 hour, column expires in authtoken) and it is strange to check expired sessions.
Additional context

Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by tracing the OAuth2 authpicker, login, and grant pages described in the issue. Compare storing granted scopes in a new table with using the authtoken table, including client identity, expiration, and revocation behavior. Done means redundant grant screens are skipped when no new scopes are requested and users can revoke client scopes through the web UI.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- php
- Domain
- authentication, authorization
- Issue type
- Feature
- Difficulty
- 5/5
- Estimated time
- Over a week
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 30/100