Don't leak server address to openstreetmap.org
Nobody has claimed this yet.
- Dominant language
- JavaScript
- Stars
- 598
- Forks
- 113
- PR merge metrics
- No merged PRs in 30d
Description
When you click on a location it sends the lat/long to openstreetmap.org along with the server origin. I think the server origin should be kept private. If users are clicking on the map, there's a high chance the location is somewhere they've been or somewhere they live/work. Sending the Nextcloud server origin along with the location creates a link between the location and the owner of the domain.
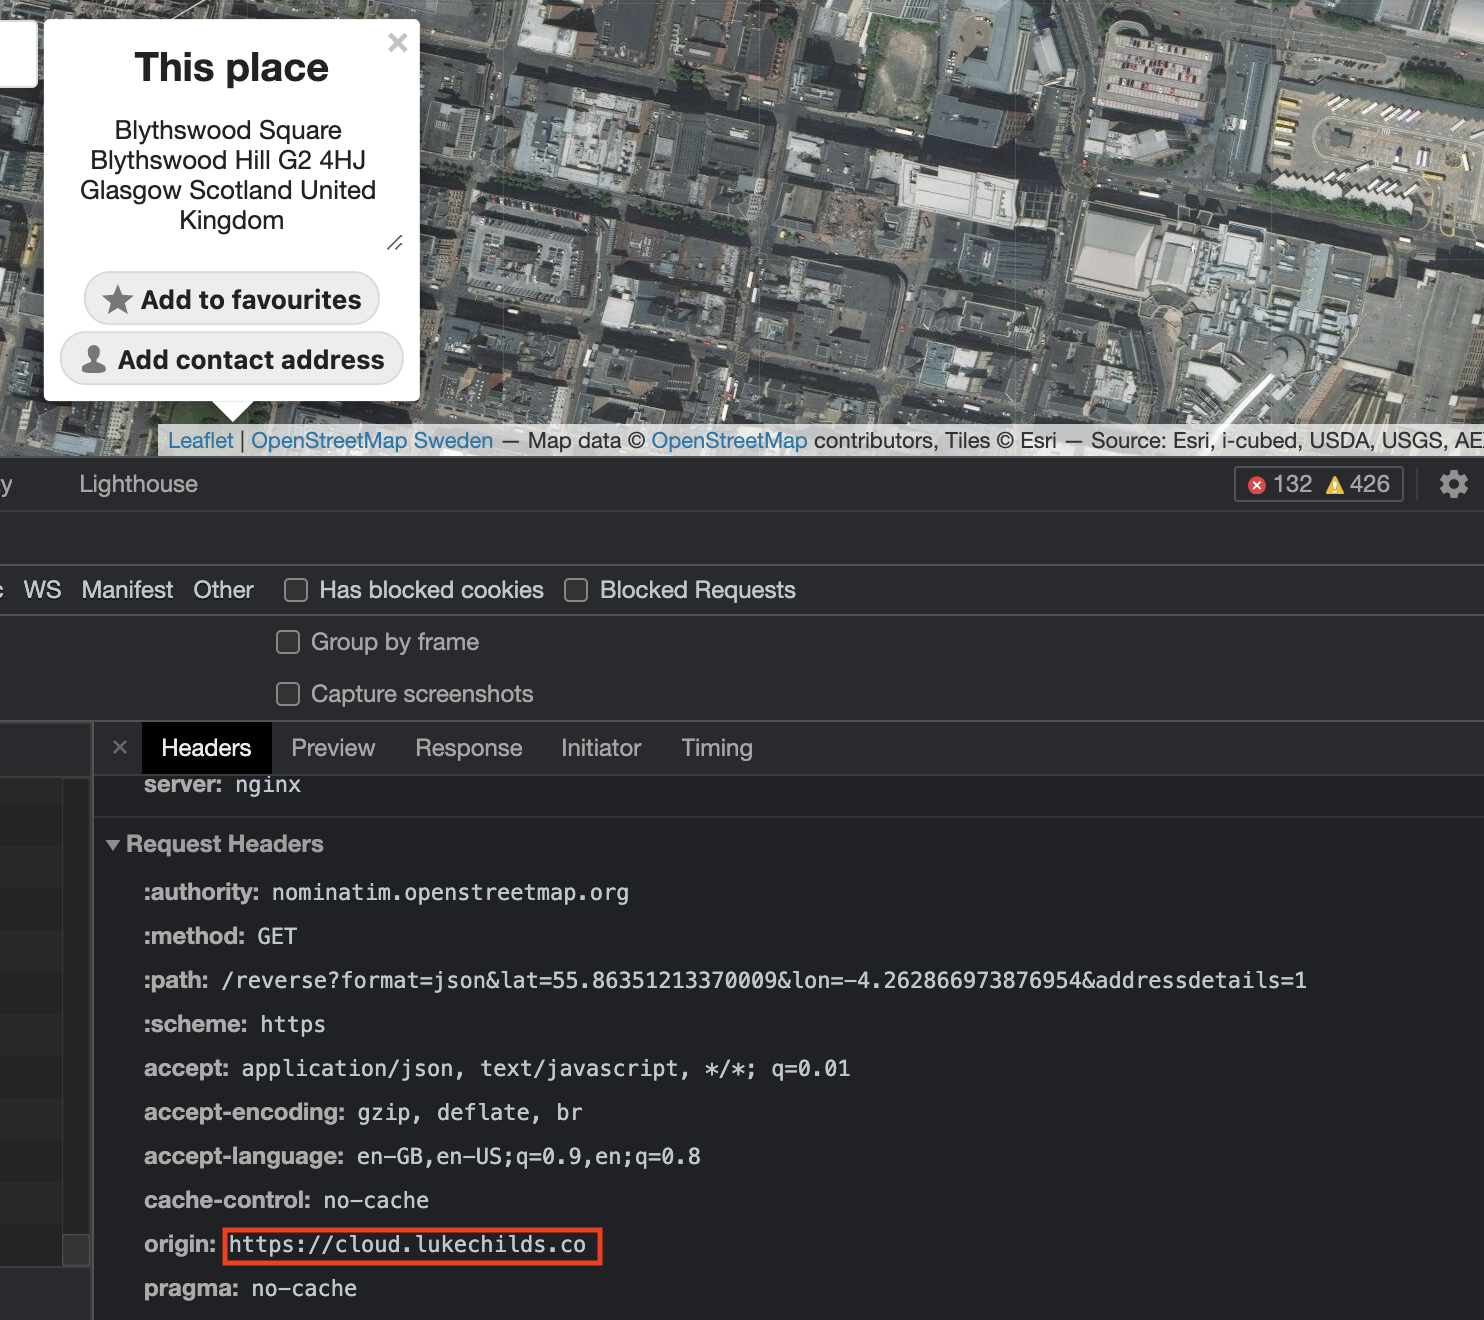
I'm not sure this can be disabled in the browser without breaking CORS, but it could be resolved by proxying the requests through Nextcloud. If you proxied image tile requests through it would also prevent leaking the users roaming IP to the openstreetmap.org server too.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Trace the map click handling and the outbound OpenStreetMap requests, including image tile requests. The issue is complete when direct requests no longer expose the Nextcloud server origin or the user's roaming IP to openstreetmap.org, while map functionality remains available.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- javascript
- Domain
- security, web-dev
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 38/100