LDAP Password Not Being Used for Mail Provisioning
Nobody has claimed this yet.
- Dominant language
- JavaScript
- Stars
- 1k
- Forks
- 348
- Avg merge
- 12h 28m
- Merged PRs (30d)
- 91
Description
Steps to reproduce
I have an interesting use case, that I have not found documented yet - although if I've missed it, please feel free to point me in the right direction.
Currently, I have Nextcloud set up with an LDAP backend, synchronizing the users successfully. In addition, I am using OpenID Connect Login (v. 2.3.1) to pass users in to Nextcloud automatically via SSO, so they do not have to log in. OpenID Connect Login provides a mechanism to link users to their LDAP account, so they stay in sync, instead of creating new accounts within Nextcloud, only allowing the user to log in to the system if they come in through SSO AND have an LDAP account.
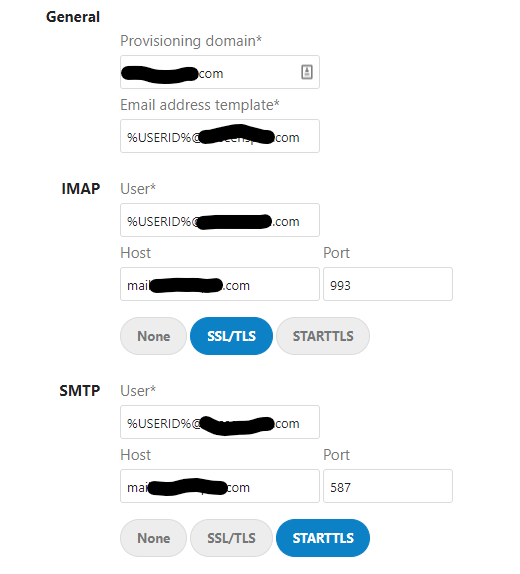
After setting both of these up, I attempted to set up the Mail app Provisioning Configuration to automatically provision the mail account, however, the account is being set up with an incorrect password, therefore the mail app cannot open the mailbox.
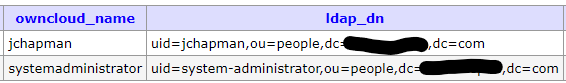
Some additional information showing the users mapped together (with some values redacted for privacy/security):
sso.config.php
$CONFIG = array (
        'allow_user_to_change_display_name' => false,
        'lost_password_link' => 'disabled',
        'oidc_login_provider_url' => 'https://mydomain/application/o/cloudoidc/',
        'oidc_login_client_id' => 'secretID',
        'oidc_login_client_secret' => 'secret',
        'oidc_login_auto_redirect' => false,
        'oidc_login_logout_url' => 'https://mydomain/if/session-end/cloudoidc/',
        'oidc_login_end_session_redirect' => false,
        'oidc_login_button_text' => 'Log in with My Domain SSO',
        'oidc_login_hide_password_form' => true,
        'oidc_login_use_id_token' => false,
        'oidc_login_attributes' => array (
            'id' => 'preferred_username',
            'name' => 'given_name',
            'mail' => 'email',
            'ldap_uid' => 'preferred_username',
            'groups' => 'groups',
        ),
        'oidc_login_default_group' => 'everyone',
        'oidc_login_scope' => 'openid profile roles email',
        'oidc_login_proxy_ldap' => true,
        'oidc_login_disable_registration' => false,
        'oidc_login_redir_fallback' => false,
        'oidc_login_tls_verify' => true,
        'oidc_create_groups' => true,
        'oidc_login_webdav_enabled' => true,
        'oidc_login_password_authentication' => true,
        'oidc_login_public_key_caching_time' => 86400,
        'oidc_login_min_time_between_jwks_requests' => 10,
        'oidc_login_well_known_caching_time' => 86400,
        'oidc_login_update_avatar' => false,
    );
Mail app Configuration
LDAP User Mapping
Mail Accounts

Is there something specific that needs to be done to tell the Mail app to read the LDAP user information to be able to send the correct password (or any password at all)?
Expected behavior
Since the user is being synced from LDAP and OpenID is linking the user to the LDAP user, I would love to be able to read the user information from LDAP, pass through the correct password, and log in to email through auto-provisioning without the user having to change/enter their information manually.
Actual behavior
The user gets a completely blank email box with the following in the server error logs:

Mail app version
1.11.7
Mailserver or service
Postfix/Dovecot
Operating system
Ubuntu 20.04.4 LTS
PHP engine version
PHP 8.0
Web server
Nginx
Database
MariaDB
Additional info
Nextcloud Hub II (23.0.2)
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by reproducing the issue with the Mail app Provisioning Configuration, the LDAP user mapping, and the OpenID Connect settings shown in the report. Trace how the provisioning configuration obtains credentials and compare that with the linked LDAP account and the Postfix/Dovecot authentication requirements. Done means a provisioned mailbox can authenticate without manual password entry, with appropriate coverage for the reported setup.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- mariadb, nginx, php, ubuntu
- Domain
- authentication, backend
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100