microsoft / microsoft/AttackSurfaceAnalyzer
Windows Metadata Changes to Certificates (which do not modify the certificate itself) are not captured
Nobody has claimed this yet.
- Dominant language
- C#
- Stars
- 3k
- Forks
- 294
- PR merge metrics
- No merged PRs in 30d
Description
Describe the bug
Open the user certificate managed and change some properties after first creating a base scan. Run another and note the changes are not detected. It appears some properties are not captured for comparison which could be by design? But some key ones like OCSP checking being disabled are important from a security standpoint.
To Reproduce
Steps to reproduce the behavior:
- Go to a certificate and edit the properties
- Change the friendly name i.e. DO_NOT_TRUST to DO_TRUST, change the cert purposes or disable the OCSP checks if enabled or change the extended validation for example. Save and run a scan to compare to a baseline scan.
- Note the changes are not detected
Expected behavior
Modification of key properties should be detected. Might be a good idea to document if not in scope for the current release and convert this to an enhancement.
Screenshots
If applicable, add screenshots to help explain your problem.
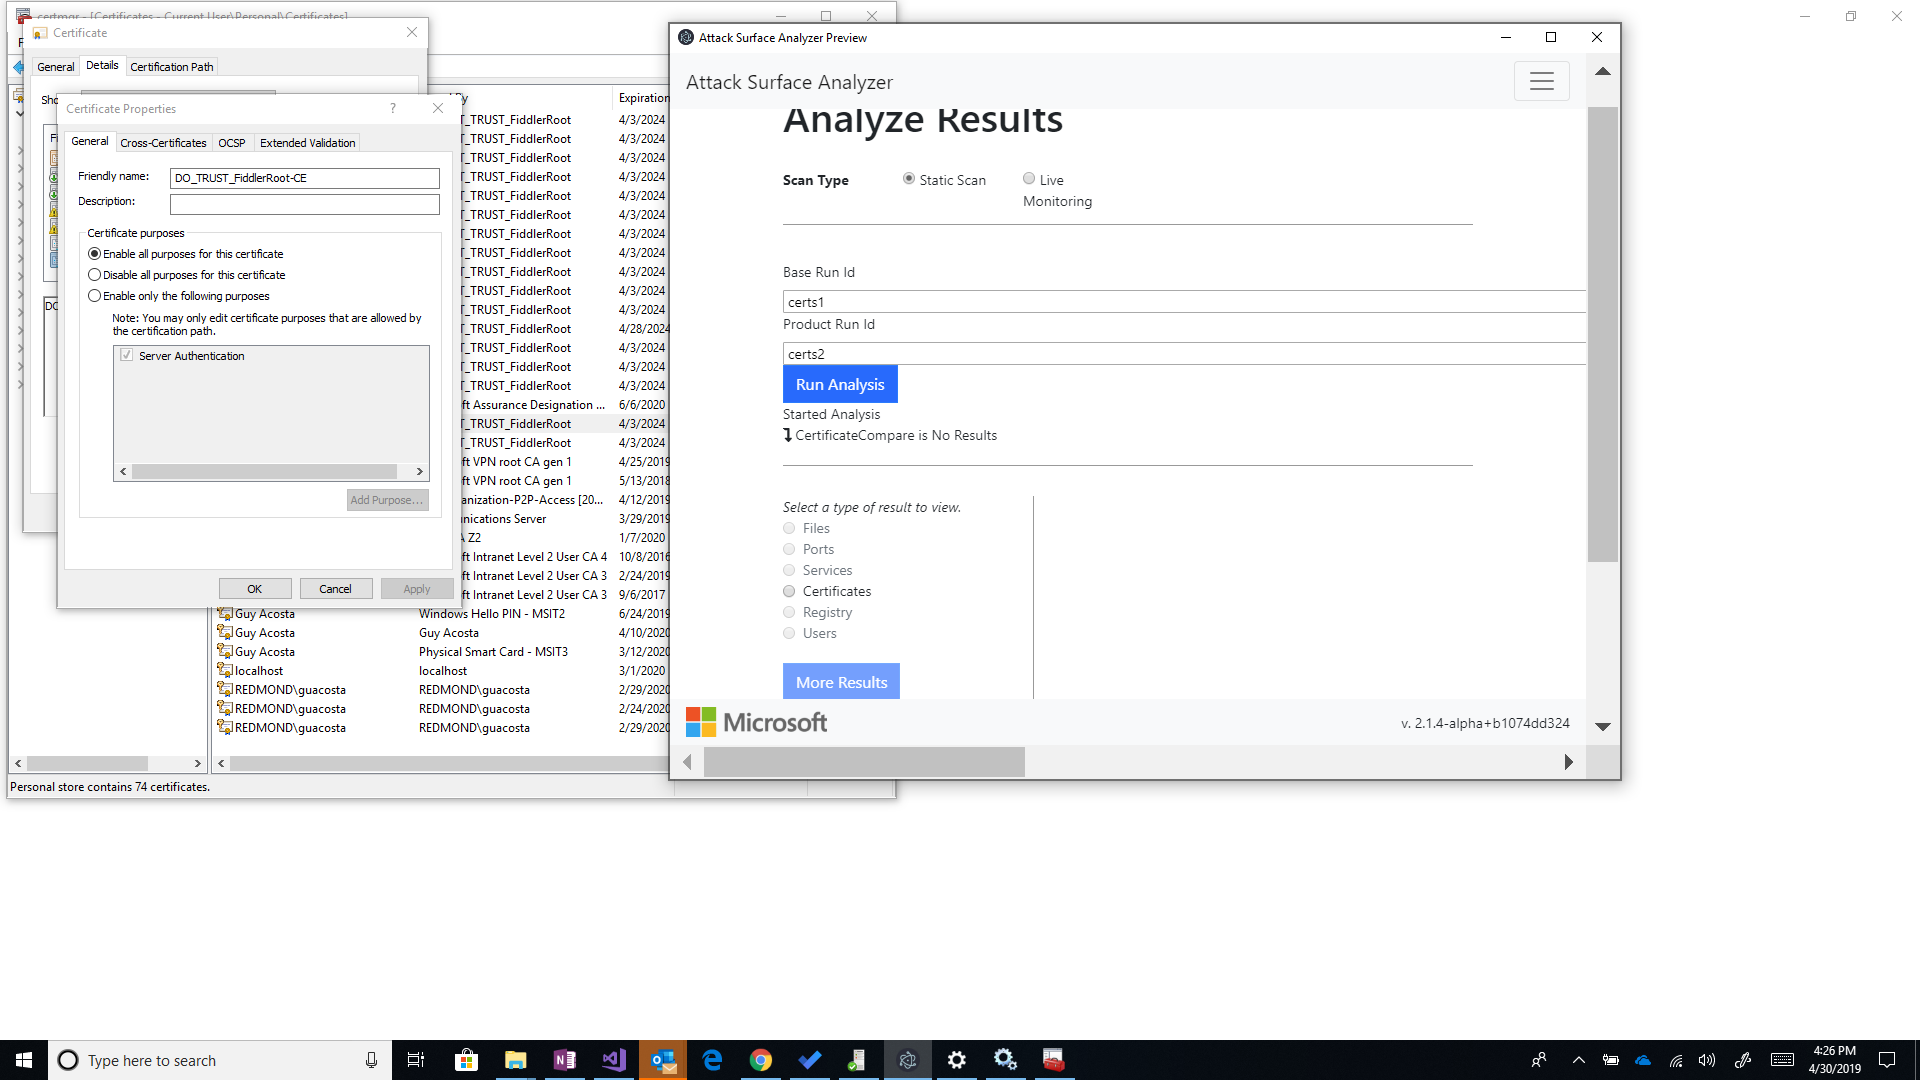

System Configuration (please complete the following information):
- OS: Windows
- OS Version: Windows 10
- Application Version: 2.1...see image
- CLI or GUI: GUI
Additional Context
Add any other context about the problem here.
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
No files, tests, or code entry points are named. Reproduce the Windows GUI workflow with a baseline scan, then change the certificate friendly name, purposes, OCSP setting, or extended validation and run a comparison scan. Done means the agreed key metadata changes are detected, or the unsupported properties are documented as out of scope.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- csharp
- Domain
- operating-systems, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 25/100