matthewmueller / matthewmueller/next-flash
npm audit - component-cookie -> debug
Open
Nobody has claimed this yet.
- Dominant language
- JavaScript
- Stars
- 12
- Forks
- 1
- PR merge metrics
- No merged PRs in 30d
Description
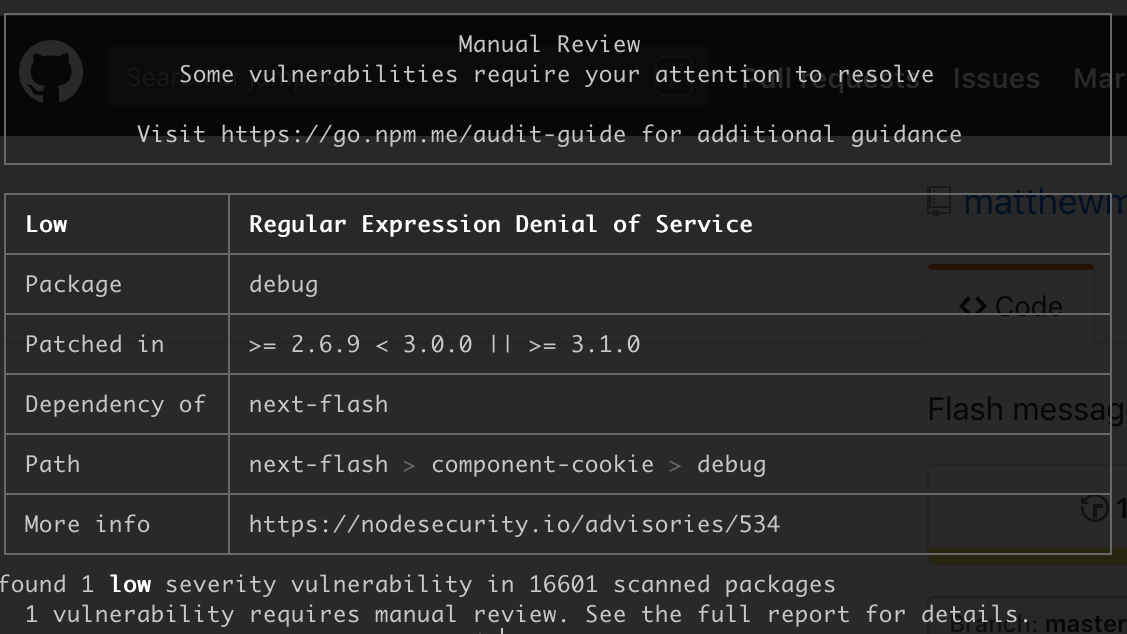
I'm getting a low severity vulnerability from component-cookie -> debug. Is this something that can be resolved? I noticed there was some discussion with @nfriedly on the next-cookies package before.
Thanks
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by running npm audit and reviewing the reported component-cookie -> debug dependency path. Determine whether the low-severity vulnerability can be resolved for next-flash, and consider the issue complete when the audit finding is resolved or its unresolved status is clearly documented.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- javascript, next.js
- Domain
- security
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100