Facebook: how reauthorization will work in goth?
Nobody has claimed this yet.
- Dominant language
- Go
- Stars
- 6.6k
- Forks
- 631
- PR merge metrics
- No merged PRs in 30d
Description
I'm using Goth in my Buffalo project and I wonder how Goth handles reauthorization. [According to Facebook](https://developers.facebook.com/docs/facebook-login/auth-vs-data#authentication-expiration), the authentication expiration is 60 days.
> When your app uses Facebook Login to authenticate someone, it receives a User access token. If your app uses one of the Facebook SDKs, this token lasts for about 60 days. However, the SDKs automatically refresh the token whenever the person uses your app, so the tokens expire 60 days after last use. If your app doesn't use the Facebook SDKs, you need to include code that refreshes the User token manually. If the User access token expires, your app must put the user through the login flow again.
I tried to change my laptop's date to next 3 months to test it but I didn't managed to perform the FB auth due to this HSTS configuration on FB side (note: there is no _Proceed_ button behind the _Advanced_ button):
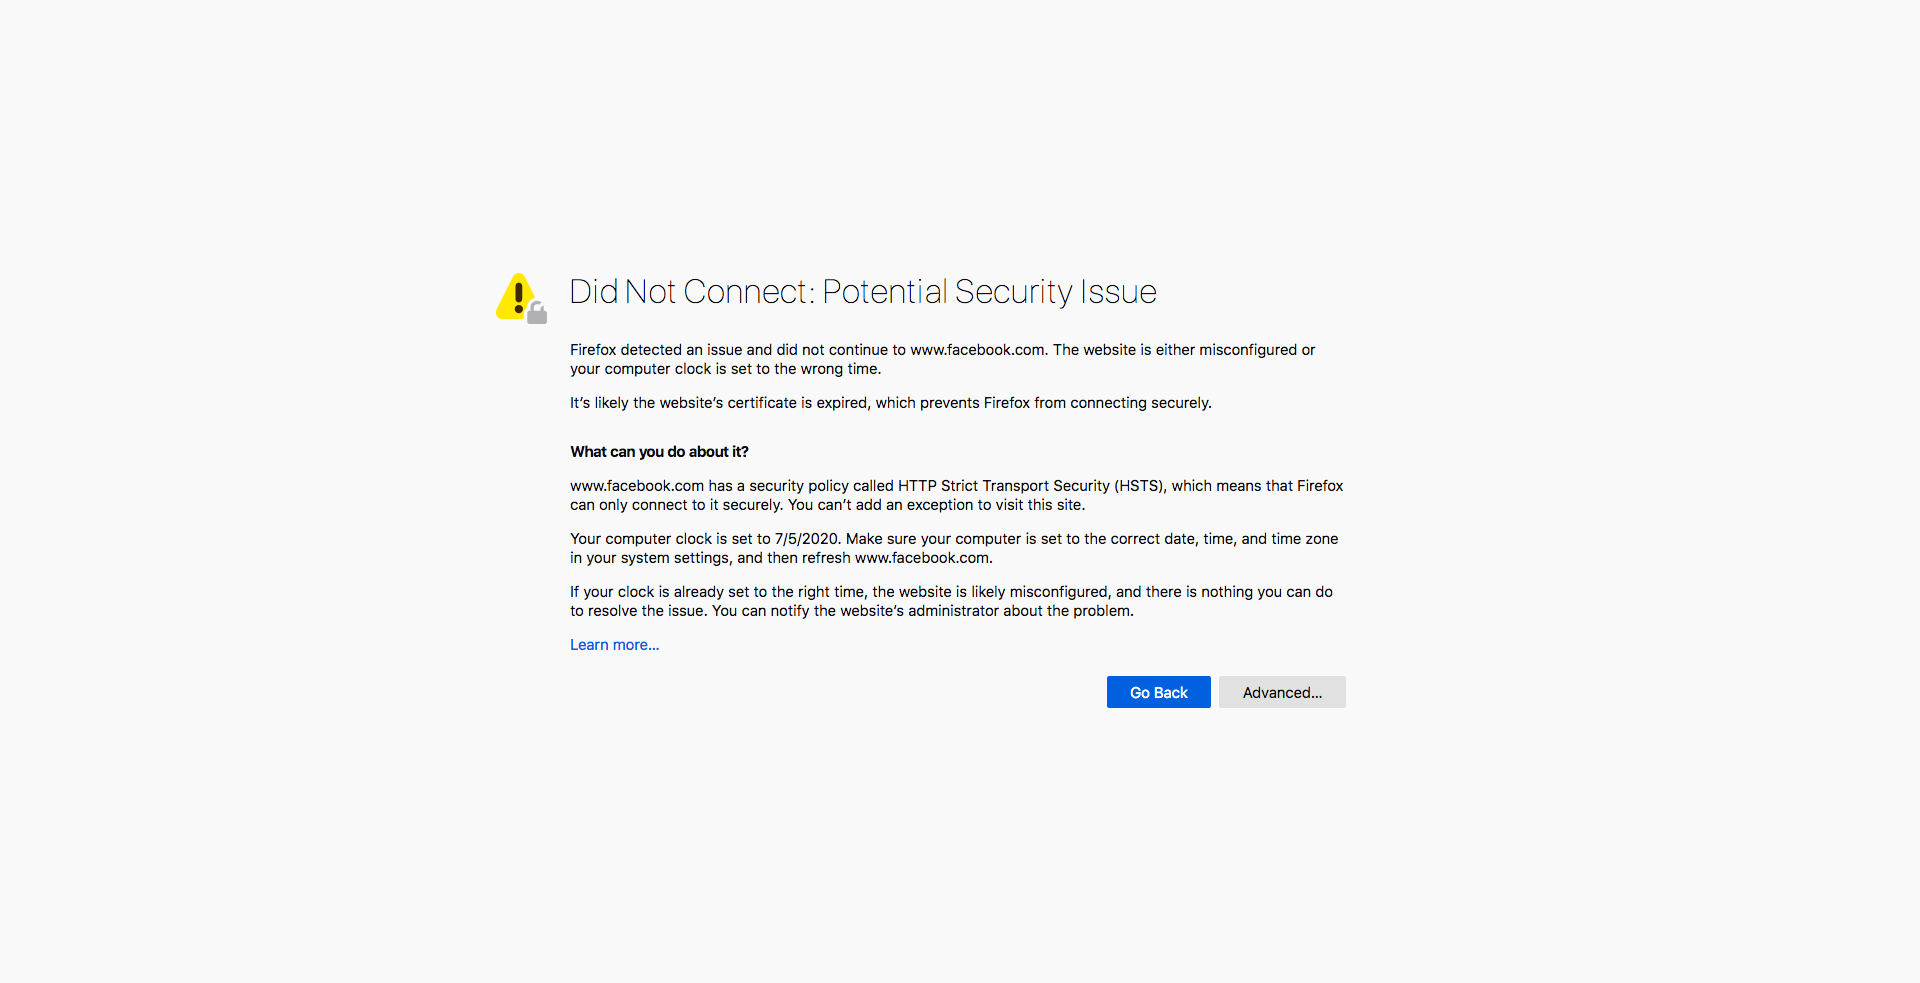
So, my questions here are:
1. What to expect after 60 days after the user authenticate himself to my app? Does he needs to authenticate himself again OR will my app (with help from Goth) will automatically handles the reauthorization for him in the background without needing him to see the [FB dialog box](https://i.imgur.com/0GFfaSv.png) and manually press the blue button again?
2. How long does Goth "remembers" an authenticated user for my app? Will my user needs to authenticate himself again using FB before that 60th day if he did not clear his browser cache & cookies?
3. After looking at the database created, looks like there are only two important fields that we need to keep; `provider` and `provider_id`. I'm curious — why don't Goth keep the access token and refresh token (if there is one) inside database as well?
---
**UPDATE**
I'm sure the answers from my questions above will also help https://github.com/markbates/goth/issues/189.
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Review issue 189 alongside the Facebook authentication-expiration documentation. Then inspect Goth's authentication and database behavior to document what happens after token expiration, how long authentication is remembered, and why provider and provider_id are stored without access or refresh tokens.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- go
- Domain
- authentication
- Issue type
- Documentation
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100