mandiant / mandiant/capa-rules
[Rule Idea] - Lazarus Decode Method
Nobody has claimed this yet.
- Dominant language
- No language data
- Stars
- 736
- Forks
- 245
- Avg merge
- 4d 53m
- Merged PRs (30d)
- 2
Description
## Prerequisites
* [x] Put an X between the brackets on this line if you have done all of the following:
* Checked that your rule idea isn't already filed: [search](https://github.com/fireeye/capa-rules/issues?q=is%3Aissue+is%3Aopen+)
## Summary
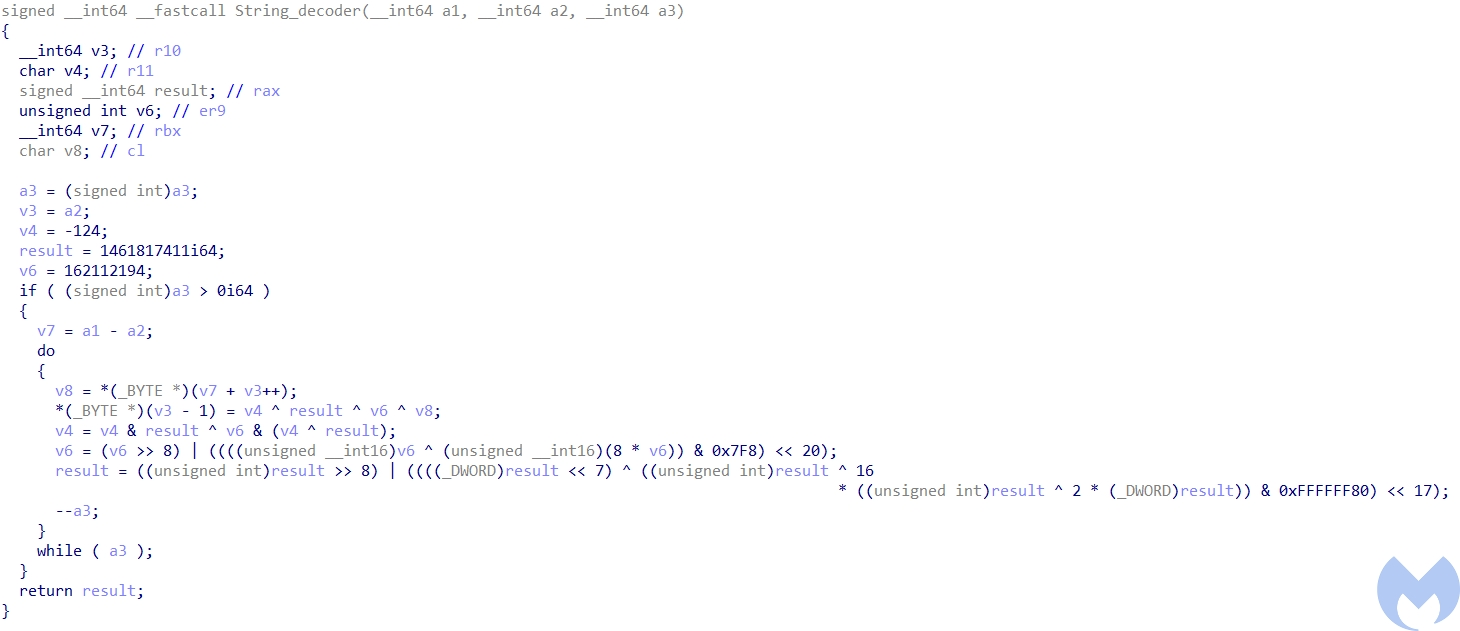
Lazarus uses a custom string decoding algo. The algorithm uses base64 and then a custom routine with arithmetic operations. Highlighted in the blog post here -> https://blog.malwarebytes.com/malwarebytes-news/2021/04/lazarus-apt-conceals-malicious-code-within-bmp-file-to-drop-its-rat/
## Examples
## Features
* `& 0x7f8`
* `<< 0x14`
* `0xFFFFFF80`
* `<< 0x11`
* `nxzor with counts`
* `characteristic loop`
## Additional context
## Rule details
### Namespace
Could fit in either
* `data-manipulation/encoding`
* `anti-analysis/obfuscation/string`
### References
* https://blog.malwarebytes.com/malwarebytes-news/2021/04/lazarus-apt-conceals-malicious-code-within-bmp-file-to-drop-its-rat/
* https://github.com/hackOtack/Malware/blob/main/lazerous_string_decoder.cpp
### Other rule meta information
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start with the Malwarebytes blog post and the linked lazerous_string_decoder.cpp reference, then compare the listed operations and loop characteristics with existing rules under data-manipulation/encoding and anti-analysis/obfuscation/string. Done means adding a capa rule that reliably identifies this Lazarus decoding method, with validation against suitable samples; the issue provides no local rule file or test path.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- cpp
- Domain
- reverse-engineering, security
- Issue type
- Feature
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100