learningequality / learningequality/studio
CORS problem when pre-viewing html5 content in studio
Nobody has claimed this yet.
- Dominant language
- Python
- Stars
- 191
- Forks
- 307
- Avg merge
- 5d 6h
- Merged PRs (30d)
- 10
Description
Summary
Previewing of html5 content is incorrect as the browser is blocking some of the files due to a CORS problem: When browsing from https://studio.learningequality.org/ some of the files in the html5 content have the https://master.studio.learningequality.org/ server in their urls.
Category
BUG
Usage Details
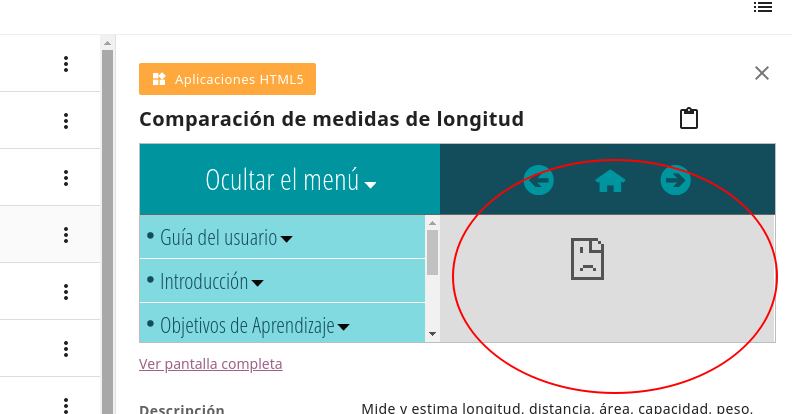
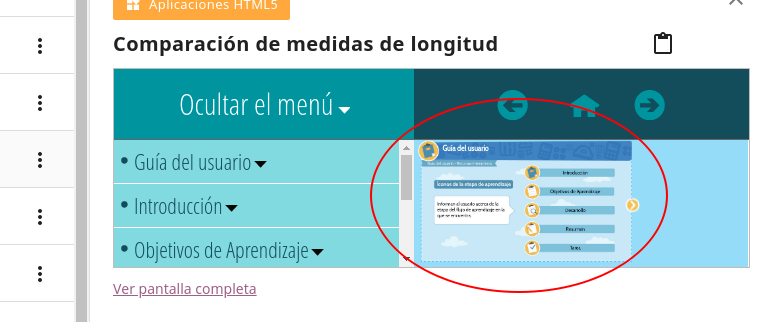
The same page viewed from https://master.studio.learningequality.org/es-es/channels/d948de3866444cfe843f7b10c00c5470/#/59d93a29e1de4c68a4f02cdc77b33ea4/145bbfde7b8c4c0985ab5c8e859b3a4a
Traceback or relevant snippet from browser console
In the browser (Chrome) console :
Refused to frame '<URL>' because it violates the following Content Security Policy directive: "default-src 'self' data: <URL>". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.

studio.learningequality.org/:1 Refused to frame 'https://studio.learningequality.org/' because it violates the following Content Security Policy directive: "default-src 'self' data: http://master.studio.learningequality.org". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.

studio.learningequality.org/:1 Refused to frame 'https://studio.learningequality.org/' because it violates the following Content Security Policy directive: "default-src 'self' data: http://master.studio.learningequality.org". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.

studio.learningequality.org/:1 Refused to frame 'https://studio.learningequality.org/' because it violates the following Content Security Policy directive: "default-src 'self' data: http://master.studio.learningequality.org". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.

studio.learningequality.org/:1 Refused to frame 'https://studio.learningequality.org/' because it violates the following Content Security Policy directive: "default-src 'self' data: http://master.studio.learningequality.org". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.

studio.learningequality.org/:1 Refused to frame 'https://studio.learningequality.org/' because it violates the following Content Security Policy directive: "default-src 'self' data: http://master.studio.learningequality.org". Note that 'frame-src' was not explicitly set, so 'default-src' is used as a fallback.
How to reproduce
In Studio (being an administrator) go to the url https://studio.learningequality.org/es-es/channels/d948de3866444cfe843f7b10c00c5470/#/59d93a29e1de4c68a4f02cdc77b33ea4 and click on any of the html5 resources to see its details and preview
Real-life consequences (anything community should be aware of, for instance how it affects end users)
Users are already having problems and complaining https://community.learningequality.org/t/problemas-con-contenidos-scorm/1885/6
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Reproduce the issue using the provided Studio URL and inspect Chrome's console for the CSP and CORS blocks while previewing an HTML5 resource. Trace the preview response and its referenced URLs to the configuration that supplies the policy. Done means the preview loads its files without cross-origin or framing violations.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- python
- Domain
- security, web-dev
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100