keybase / keybase/keybase-issues
DNSSEC proof isn't reliable over Tor
- Dominant language
- No language data
- Stars
- 899
- Forks
- 40
- PR merge metrics
- No merged PRs in 30d
Description
```
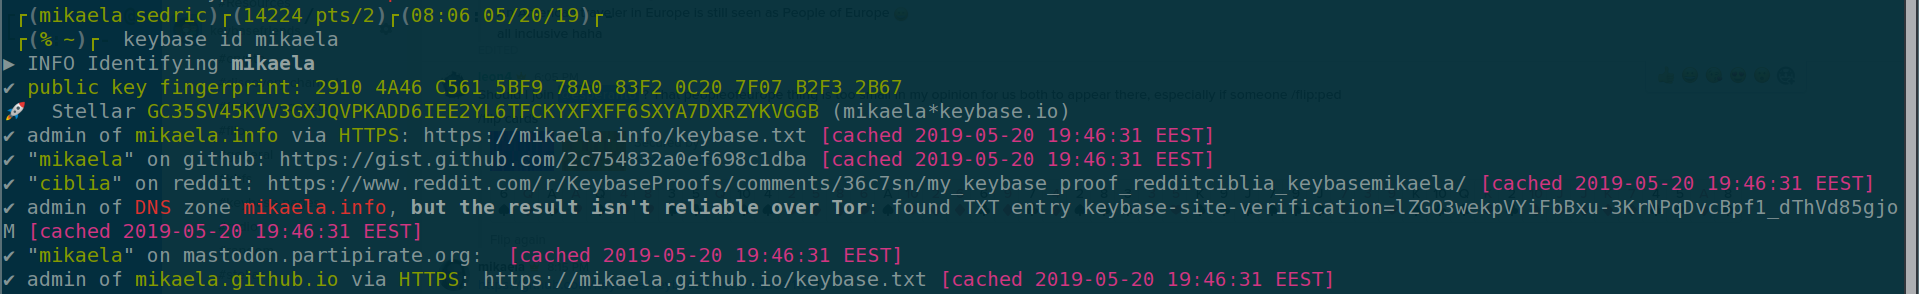
└┌(%:~)┌- keybase id mikaela
▶ INFO Identifying mikaela
...
✔ admin of mikaela.info via HTTPS: https://mikaela.info/keybase.txt [cached 2019-05-20 19:46:31 EEST]
✔ admin of DNS zone mikaela.info, but the result isn't reliable over Tor: found TXT entry keybase-site-verification=lZGO3wekpVYiFbBxu-3KrNPqDvcBpf1_dThVd85gjoM [cached 2019-05-20 19:46:31 EEST]
...
```
[Mikaela.info has DNSSEC](https://dnssec-debugger.verisignlabs.com/mikaela.info), so I think Keybase should validate the DNSSEC signatures and if they are valid, not show warning about the result not being reliable over Tor. I think there should possibly be warning about all DNS proofs that cannot be validated using DNSSEC or at least a note on successful DNSSEC validation.
I am not sure if this is a duplicate of #2073, but I opted to open a different issue, because there it's said that DNS proofs are in yellow, while in my output above `DNS` and `mikaela.info` are red.
Contributor guide
No contributing guide indexed for this repository
Research direction
Start by reproducing `keybase id mikaela` over Tor and inspect the DNS proof validation path; the issue names no files or tests. Done means valid DNSSEC-backed results no longer show the unreliable warning, while results without validated DNSSEC receive an appropriate warning or note.
Written by the indexing model from the issue text.
Assessment
- Domain
- networking, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100