karma-runner / karma-runner/karma
Adding a CSP policy fails due to inline code usage by karma
- Dominant language
- JavaScript
- Stars
- 12k
- Forks
- 1.7k
- PR merge metrics
- No merged PRs in 30d
Description
### Expected behaviour
I want karma to run with a CSP policy to prevent CSP violations from being introduced in a JS codebase.
Using the customHeaders feature I want to be able to add the following:
```javascript
customHeaders: [
{
match: '\\.html',
name: 'Content-Security-Policy',
value: `script-src 'self'; object-src 'self';`
}
],
```
Which represents the default security policy of an extension in Chrome: https://developer.chrome.com/extensions/contentSecurityPolicy#restrictions
And have karma itself execute my tests without karma triggering csp violations.
### Actual behaviour
Due to karma relying on injecting inline scripts I am not able to use the above security policy. Instead I have to relax the restriction to the following:
```javascript
customHeaders: [
{
match: '\\.html',
name: 'Content-Security-Policy',
value: `script-src 'self' 'unsafe-inline'; object-src 'self';`
}
],
```
This does allow the karma framework to execute but using a weaker CSP configuration than desired.
### Environment Details
- Karma version (output of `karma --version`): 1.7.1
- Relevant part of your `karma.config.js` file: see above
### Steps to reproduce the behaviour
1. Add the customHeaders from the expected behaviors section above
2. Run karma for a simple test
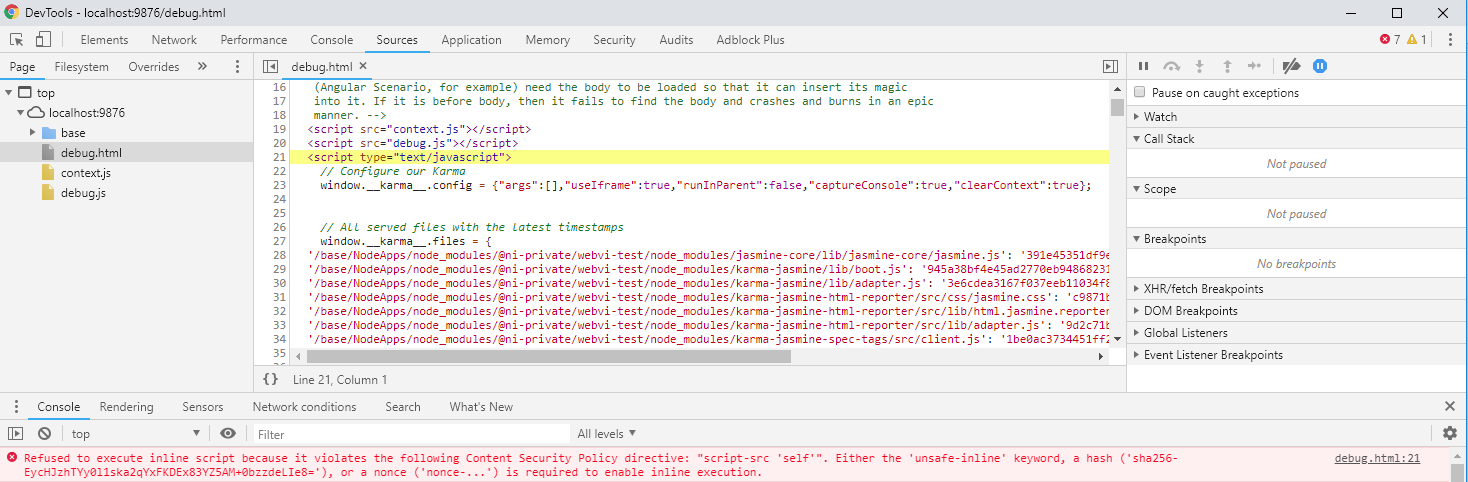
3. Notice the following errors in Chrome dev tools:
```
Refused to execute inline script because it violates the following Content Security Policy directive: "script-src 'self'". Either the 'unsafe-inline' keyword, a hash ('sha256-EycHJzhTYy0l1ska2qYxFKDEx83YZ5AM+0bzzdeLIe8='), or a nonce ('nonce-...') is required to enable inline execution.
```
Contributor guide
Assessment
This issue has not been assessed yet.