jpush / jpush/jpush-react-native
android组件暴露漏洞
Nobody has claimed this yet.
- Dominant language
- Java
- Stars
- 1.4k
- Forks
- 348
- PR merge metrics
- No merged PRs in 30d
Description
你的运行环境
React Native Environment Info:
System:
OS: macOS 10.15.1
CPU: (8) x64 Intel(R) Core(TM) i5-8279U CPU @ 2.40GHz
Memory: 149.02 MB / 8.00 GB
Shell: 5.7.1 - /bin/zsh
Binaries:
Node: 12.16.1 - /usr/local/bin/node
Yarn: 1.9.4 - /usr/local/bin/yarn
npm: 6.13.4 - /usr/local/bin/npm
Watchman: 4.9.0 - /usr/local/bin/watchman
SDKs:
iOS SDK:
Platforms: iOS 13.2, DriverKit 19.0, macOS 10.15, tvOS 13.2, watchOS 6.1
Android SDK:
API Levels: 23, 26, 27, 28
Build Tools: 23.0.1, 23.0.3, 26.0.3, 27.0.3, 28.0.1, 28.0.3, 29.0.3
System Images: android-23 | Android TV ARM EABI v7a, android-23 | Android TV Intel x86 Atom, android-23 | Android Wear ARM EABI v7a, android-23 | Android Wear Intel x86 Atom, android-26 | Intel x86 Atom_64
IDEs:
Android Studio: 3.6 AI-192.7142.36.36.6392135
Xcode: 11.3.1/11C504 - /usr/bin/xcodebuild
npmPackages:
react: 16.8.3 => 16.8.3
react-native: 0.59.5 => 0.59.5
npmGlobalPackages:
react-native-cli: 2.0.1
react-native-git-upgrade: 0.2.7
- 插件版本: "jcore-react-native": "^1.3.2",
- react-native 版本: react-native: 0.59.5 => 0.59.5
期望效果
没有漏洞,顺利通过应用市场的审核
实际效果
上架腾讯应用市场被拒,利用腾讯云移动应用安全检测有漏洞
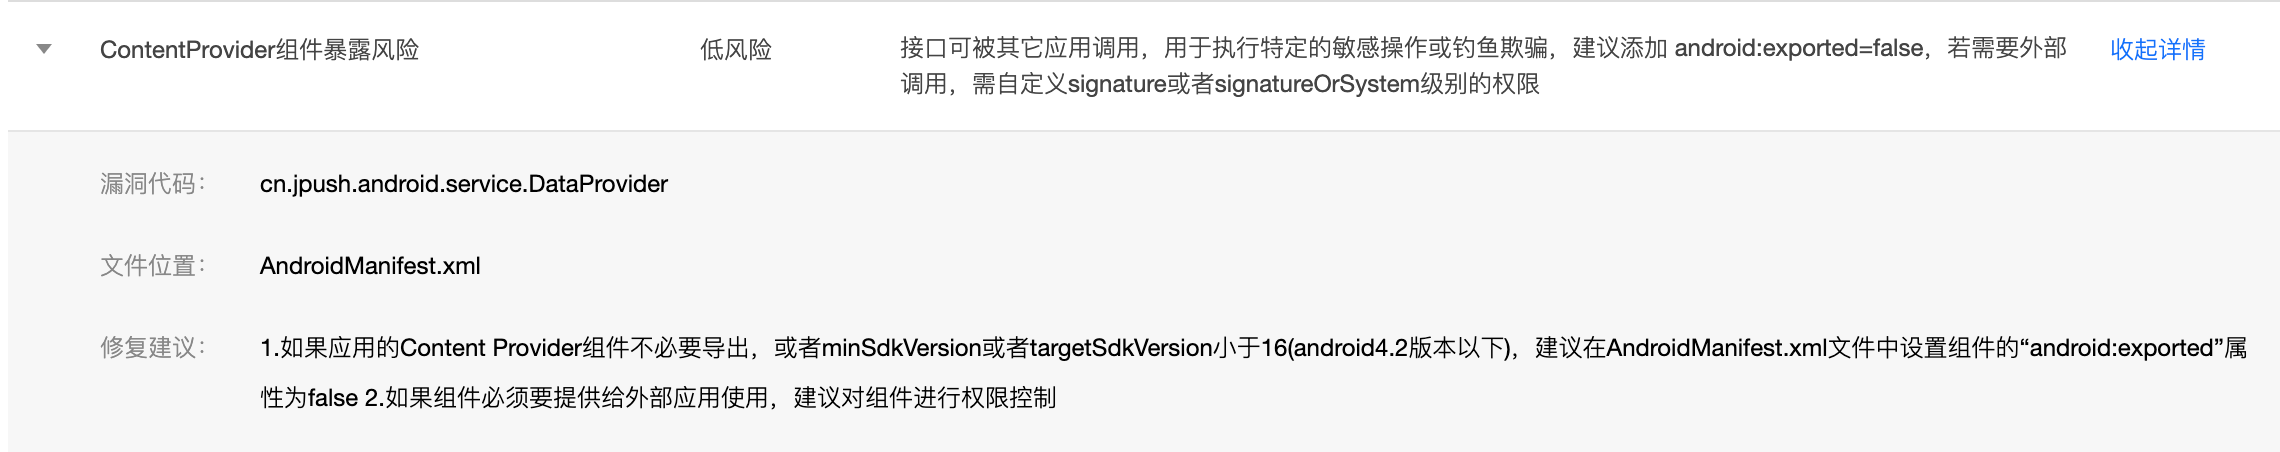
重现步骤
- 初始化react-native工程
- 添加jpush-react-native插件
- 编译android平台的release包
- 利用腾讯云移动应用安全加固apk
- 利用腾讯云移动应用安全测评
Debug logs
无
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
The report does not name an affected file, Android component, dependency, or failing test. Start by reproducing the release build with jpush-react-native and running the Tencent Cloud security assessment described in the issue. Done means identifying the reported vulnerability and confirming that the resulting Android release passes the relevant application-market security check.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- android, java, react-native
- Domain
- mobile, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 20/100