Fedora (CoreOS) Linux rejects SSH private key after update
Nobody has claimed this yet.
- Dominant language
- Python
- Stars
- 485
- Forks
- 8
- PR merge metrics
- No merged PRs in 30d
Description
I'm using the latest Postico. I have also tested this on Postico 2.
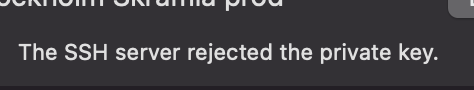
What happens is that the private SSH key is rejected when tunneling through SSH. However, using ssh in the terminal still works, and by looking at logs I have observed that the connection is rejected because the "ssh-rsa" key type isn't accepted. userauth_pubkey: key type ssh-rsa not in PubkeyAcceptedKeyTypes [preauth] is the exact log entry. My key is a rsa-sha2-256 key. Maybe the Postico usage of libssh2 is configured to send a different key type, or something along those lines? I'm not that familiar with libssh2.
Contributor guide
No contributing guide indexed for this repository
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start by examining the Postico SSH-tunneling path and its libssh2 authentication configuration, then compare its key exchange and authentication behavior with terminal ssh. Use the reported ssh-rsa rejection in the Fedora CoreOS logs as the reproduction signal; done means the RSA key is accepted for SSH tunneling after the update.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- fedora, linux, python
- Domain
- networking
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 30/100