Misconfigured browser extension silently fails auth when redirect url is wrong
- Dominant language
- Python
- Stars
- 3.2k
- Forks
- 459
- Avg merge
- 27d 1h
- Merged PRs (30d)
- 1
Description
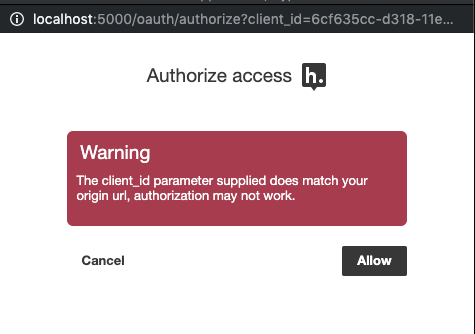
When configuring the browser extension: If I mistakenly used the embedded client OAuth client ID in the `chrome-dev.json` settings (e.g. `oauthClientId`) instead of the the correct browser extension id then authentication doesn't work but also does not error because the callback URL goes to `http://localhost:5000/app.html` which is valid, but not for the browser extension.
It would be nice if h/ was a little more supportive about this and could check to see if the URL of the page which opened the popup matches the matches the origin of the redirect URL. This could possible be done with the `HTTP_REFERER` header. If the two values don't match we could supply a warning to the user or just an error.
Contributor guide
No contributing guide indexed for this repository
Assessment
This issue has not been assessed yet.