hasura / hasura/graphql-engine
Remote schema - can't give permissions for mutations only
- Dominant language
- TypeScript
- Stars
- 32.1k
- Forks
- 3k
- PR merge metrics
- PR metrics pending
Description
### Version Information
using `hasura/graphql-engine:v2.8.3.cli-migrations-v3`, but also happened to me on `hasura/graphql-engine:latest.cli-migrations-v3`
### Environment
### What is the current behaviour?
I'm using a remote schema
```yaml
- name: My-Remote-Schema
definition:
url_from_env: REMOTE_SCHEMA_ADDRESS
timeout_seconds: 60
```
and trying to add permissions for mutations only
```yaml
permissions:
- role: admin-role
definition:
schema: |
schema {
query: Query
mutation: Mutation
}
type MyMutationResponse {
id: Int
}
type Mutation {
MyMutation(input: MyMutationRequest_Input): MyMutationResponse
}
type Query {
}
input MyMutationRequest_Input {
name: String
}
```
when running Hasura, I'm getting the following error:
```
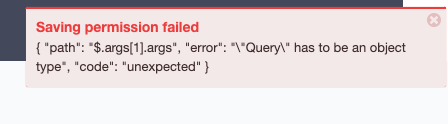
Saving permission failed
{ "path": "$.args[1].args", "error": "\"Query\" has to be an object type", "code": "unexpected" }
```
### What is the expected behaviour?
I want to have the option to not give permissions to any query, while having permissions to mutations
### How to reproduce the issue?
see the current behavior
### Screenshots or Screencast
### Any possible solutions/workarounds you're aware of?
I have to give permissions to some query. I use remote schema modification to rename it to something that will look like internal call (start with "_" for example)
### Keywords
remote schema permissions query mutation
Contributor guide
Research direction
Start with the remote schema permission definition shown in the issue and reproduce the validation error using the provided mutation-only schema. Trace the permission validation entry point that rejects the empty Query object, then verify that permissions with mutations but no query fields are accepted without requiring a workaround query.
Written by the indexing model from the issue text.
Assessment
- Domain
- api, authorization
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100