hasura / hasura/graphql-engine
document permissions on views based on insertability
- Dominant language
- TypeScript
- Stars
- 32.1k
- Forks
- 3k
- PR merge metrics
- PR metrics pending
Description
When I track a table or a view I get different permission levels for the default role "admin". On some views I only get "select" permission where on others I get "insert, select, update, delete".
Does anybody know how the default permissions are set for the "admin" role?
### Version Information
Server Version:
v2.2.0 / v2.5.0
### Environment
Hasura CE
### What is the expected behaviour?
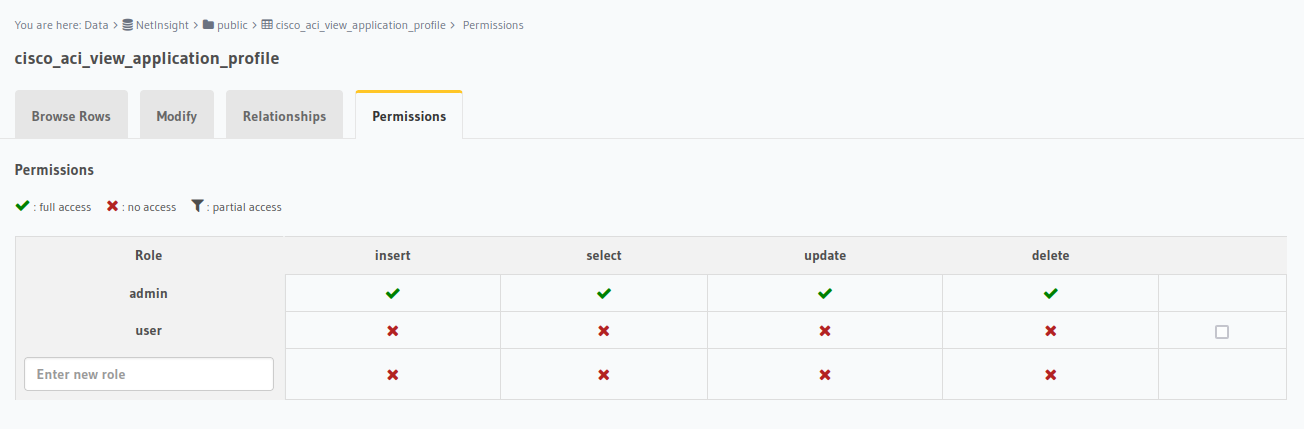
### Keywords
role, admin, permission
### What is the current behaviour?
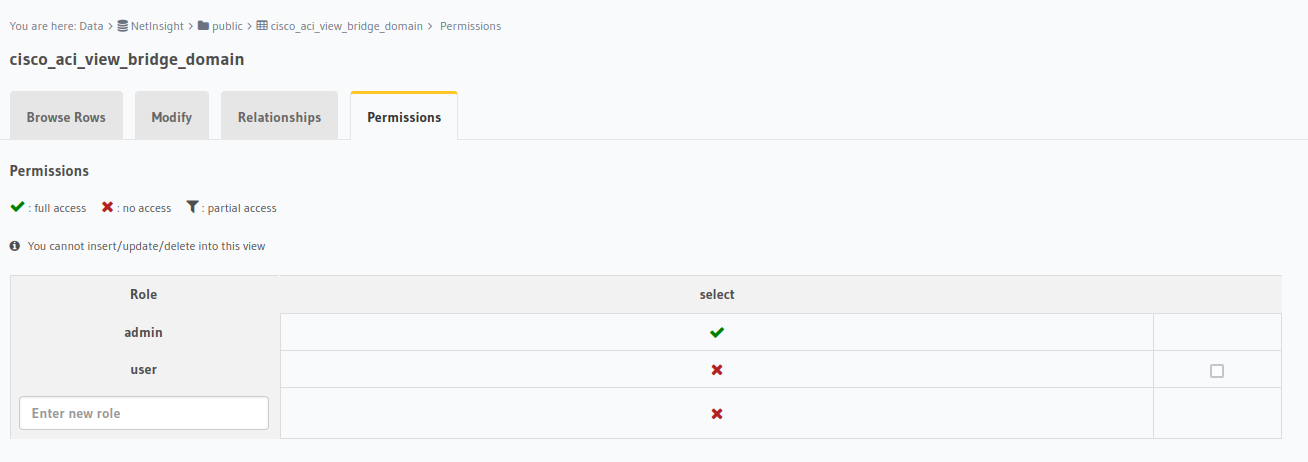
### How to reproduce the issue?
1. Track Table or View
2. Select Table or View
3. Select Permission tab
Contributor guide
Research direction
Reproduce the behavior by tracking a table or view, selecting it, and opening the Permission tab for the default "admin" role. Compare views with only select permission against views with insert, select, update, and delete, then document how permissions are determined and what behavior is expected for insertable views.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- postgres
- Domain
- authorization, database
- Issue type
- Documentation
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100