hasura / hasura/graphql-engine
_in operator missing when applying row level check against SQL Server tables
- Dominant language
- TypeScript
- Stars
- 32.1k
- Forks
- 3k
- PR merge metrics
- PR metrics pending
Description
v2.0.9 Version Information
Server Version:
CLI Version (for CLI related issue):
### Environment
Docker Windows
### What is the expected behaviour?
My requirement says that records have to be filtered by some id column present in the table.
However, a logged user can have multiple ids associated to their account (managed by the auth server)
The row level permission should allow the operator _in to filter based on the list passed into the JWT token.
Hasura docs mention that this feature is supposed to be available since v1
[permission rules ](https://hasura.io/docs/latest/graphql/core/auth/authorization/permission-rules.html)
### Keywords
SQL server, Row Level, in operator, _in
### What is the current behaviour?
When setting row level permissions on sql server tables. The _in option is not available
### How to reproduce the issue?
1. docker-compose the hasura v.2.0.9
2. connect any sql server and track any table
3. go in the permission tab and try to apply row check/filter by any field
4. the operator _in won't be available
### Screenshots or Screencast
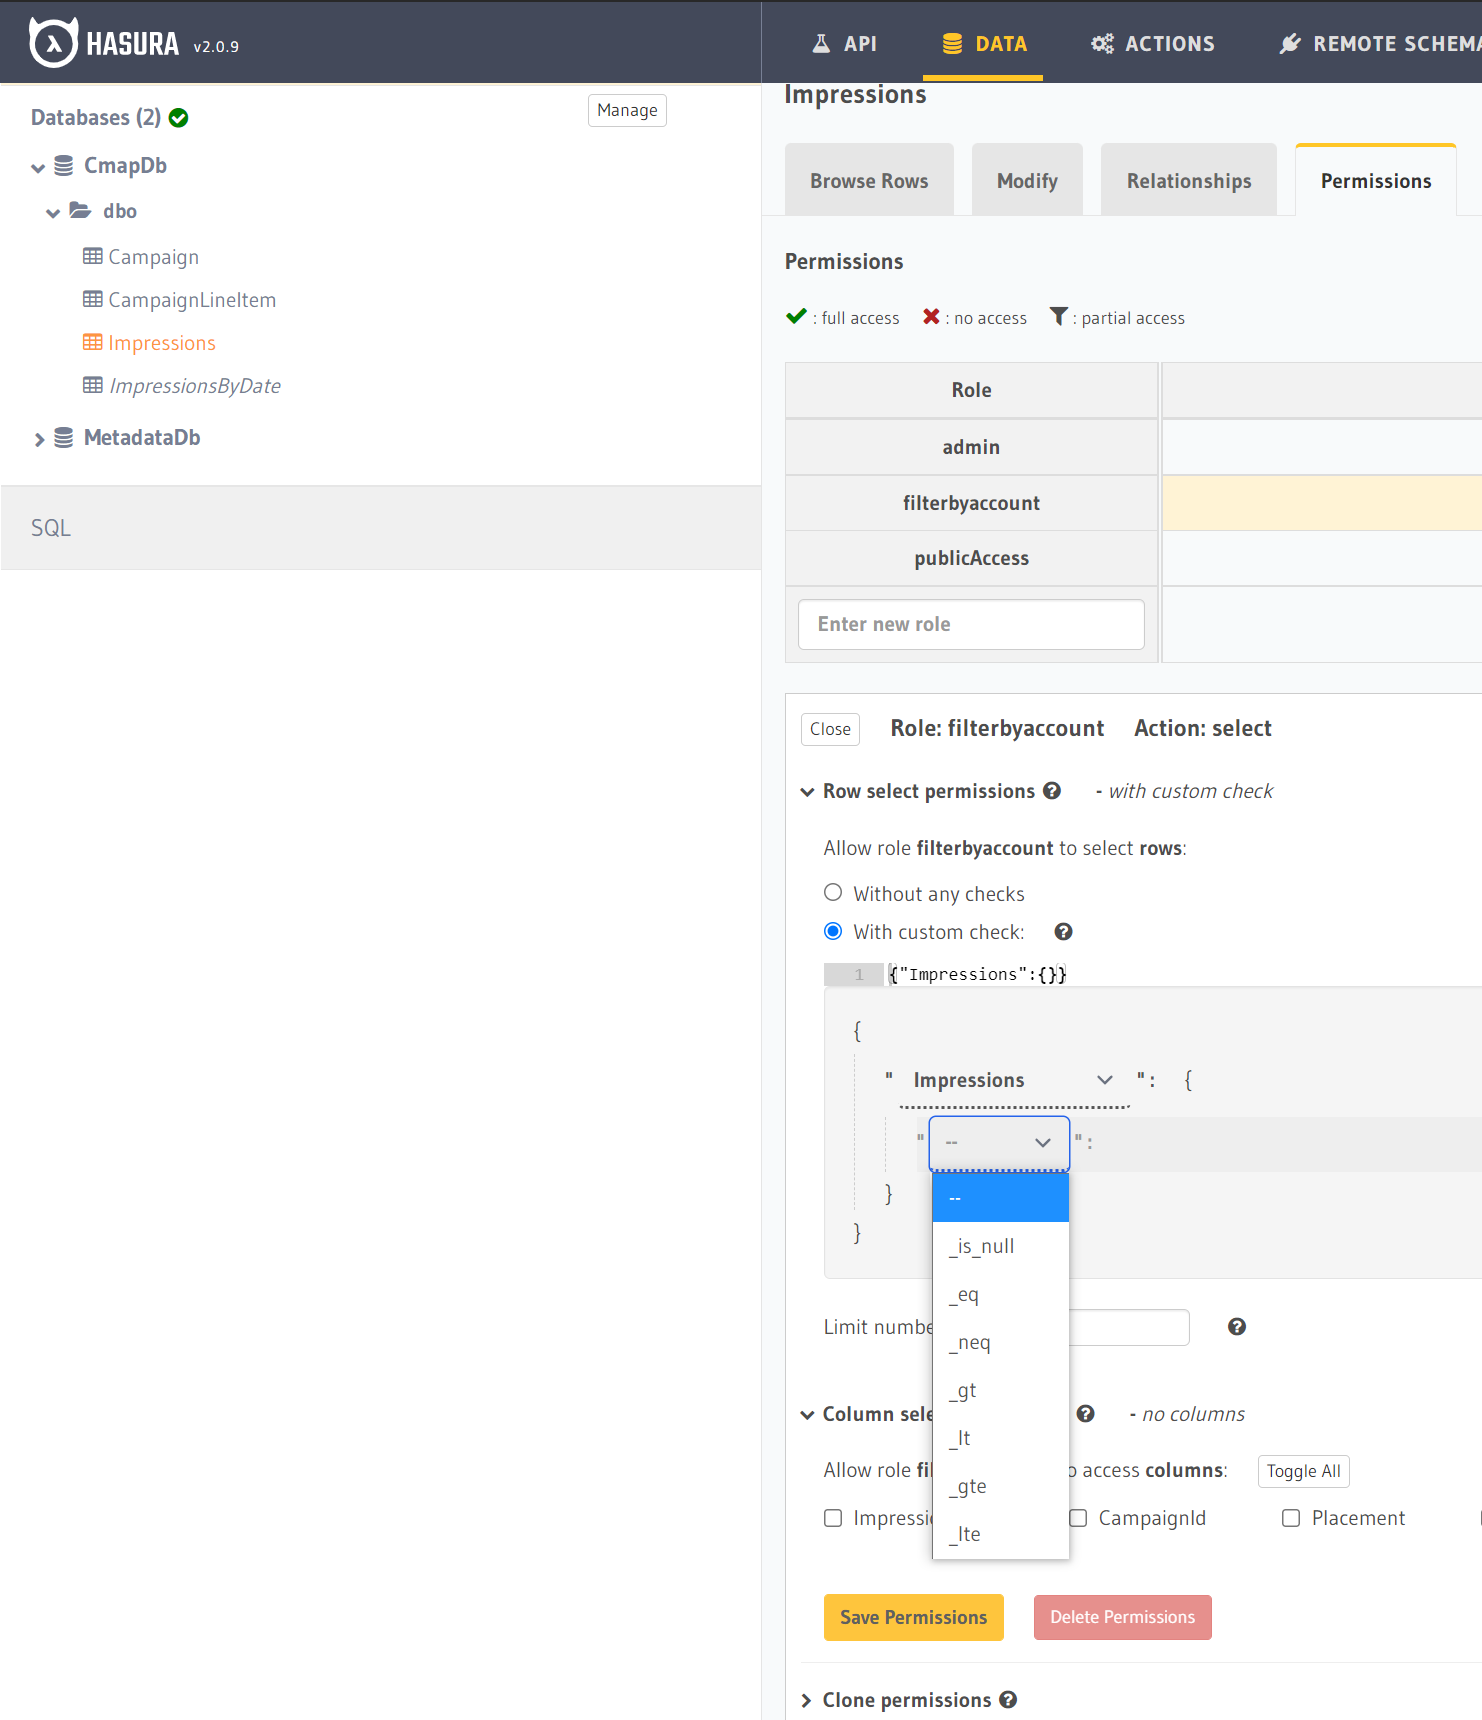
### Please provide any traces or logs that could help here.
### Any possible solutions?
### Can you identify the location in the source code where the problem exists?
### If the bug is confirmed, would you be willing to submit a PR?
Contributor guide
Assessment
This issue has not been assessed yet.