clickjacking vulnerability
- Dominant language
- TypeScript
- Stars
- 16.9k
- Forks
- 1.9k
- Avg merge
- 22h 45m
- Merged PRs (30d)
- 70
Description
Hi there,
I found that a clickjacking attack can be performed in graphiql.
Whiling visiting graphiql, the value of parameter "*query*" would be placed in editor, so when user click the "*execute button*", a GraphQL query will be sent to server and executed.
If attackers trick a logined user into clicking this button, malicious query (such as a mutation) will be executed.
For example, I set up 2 pages:
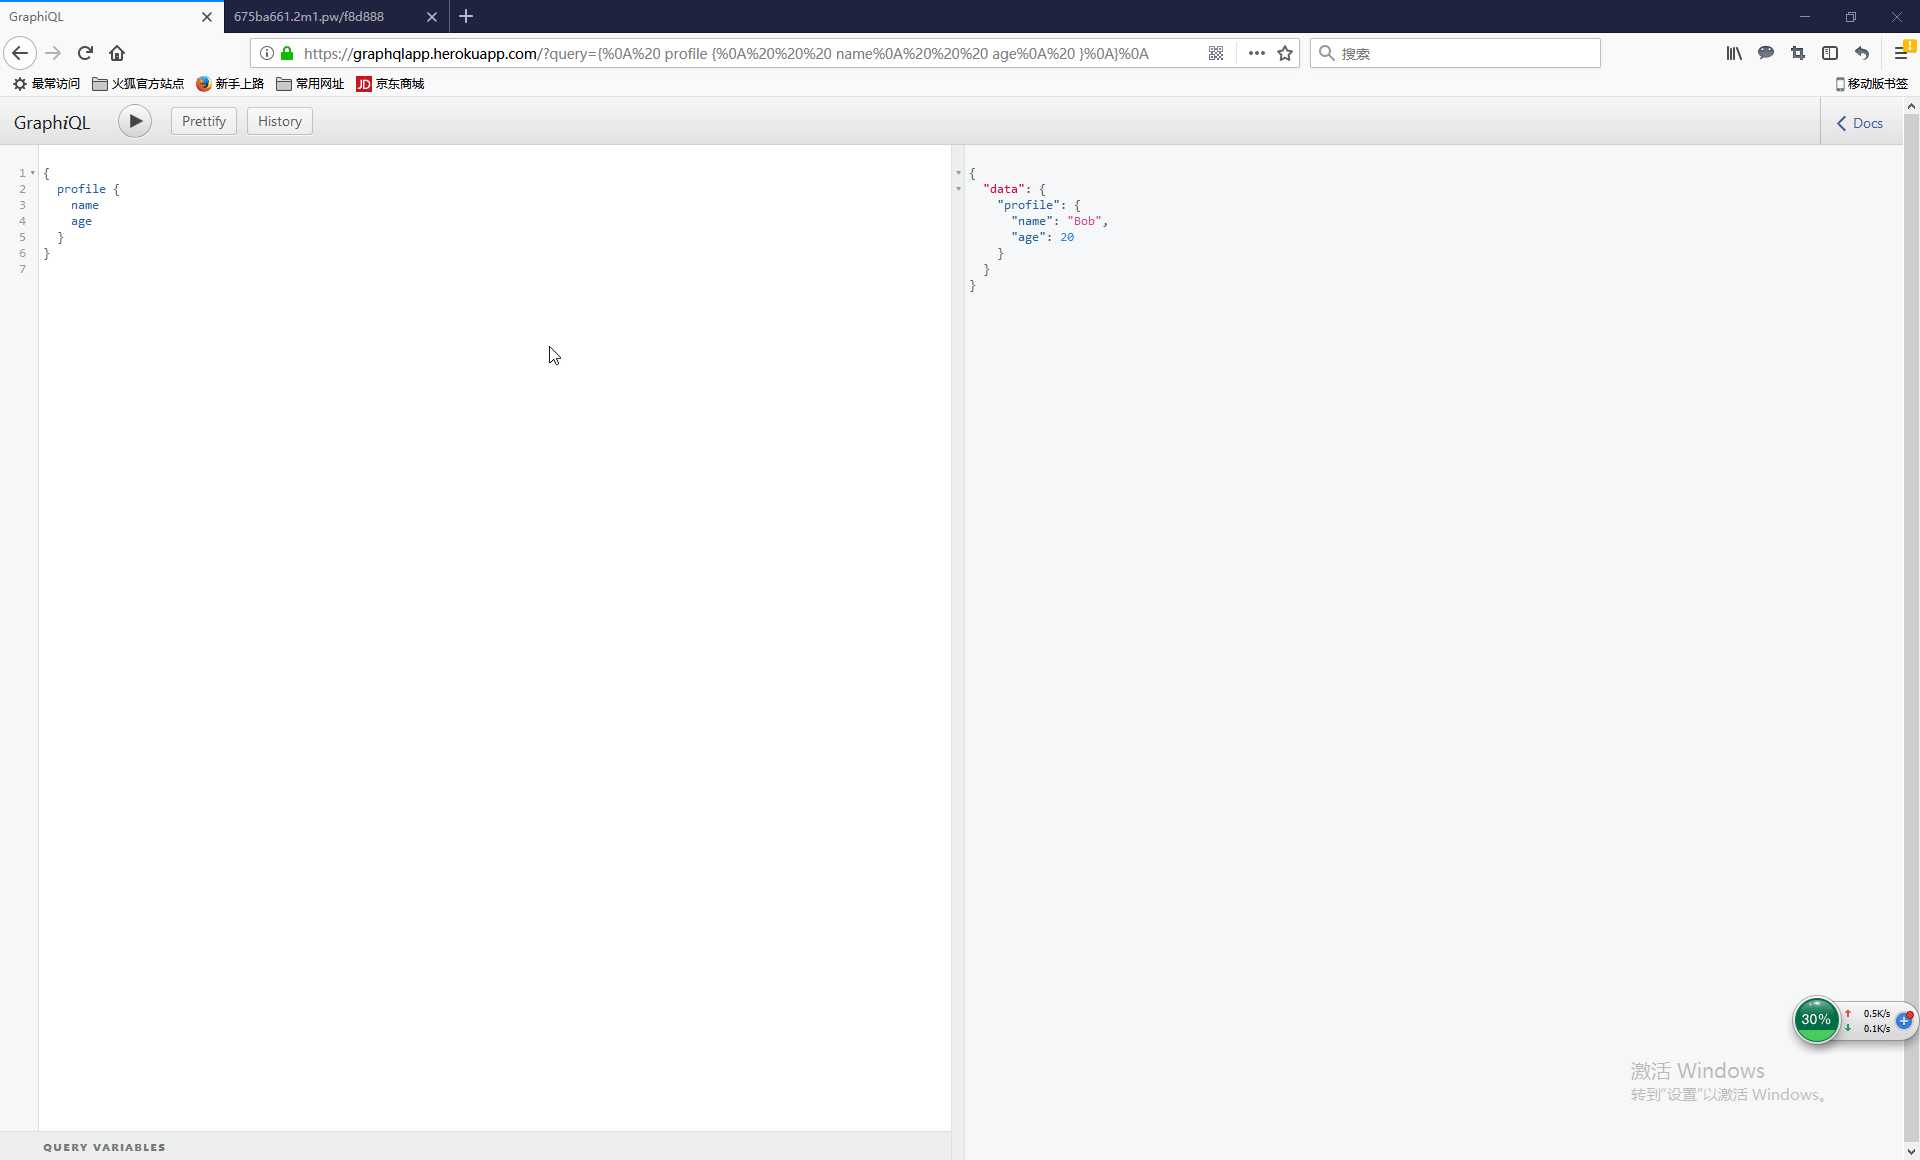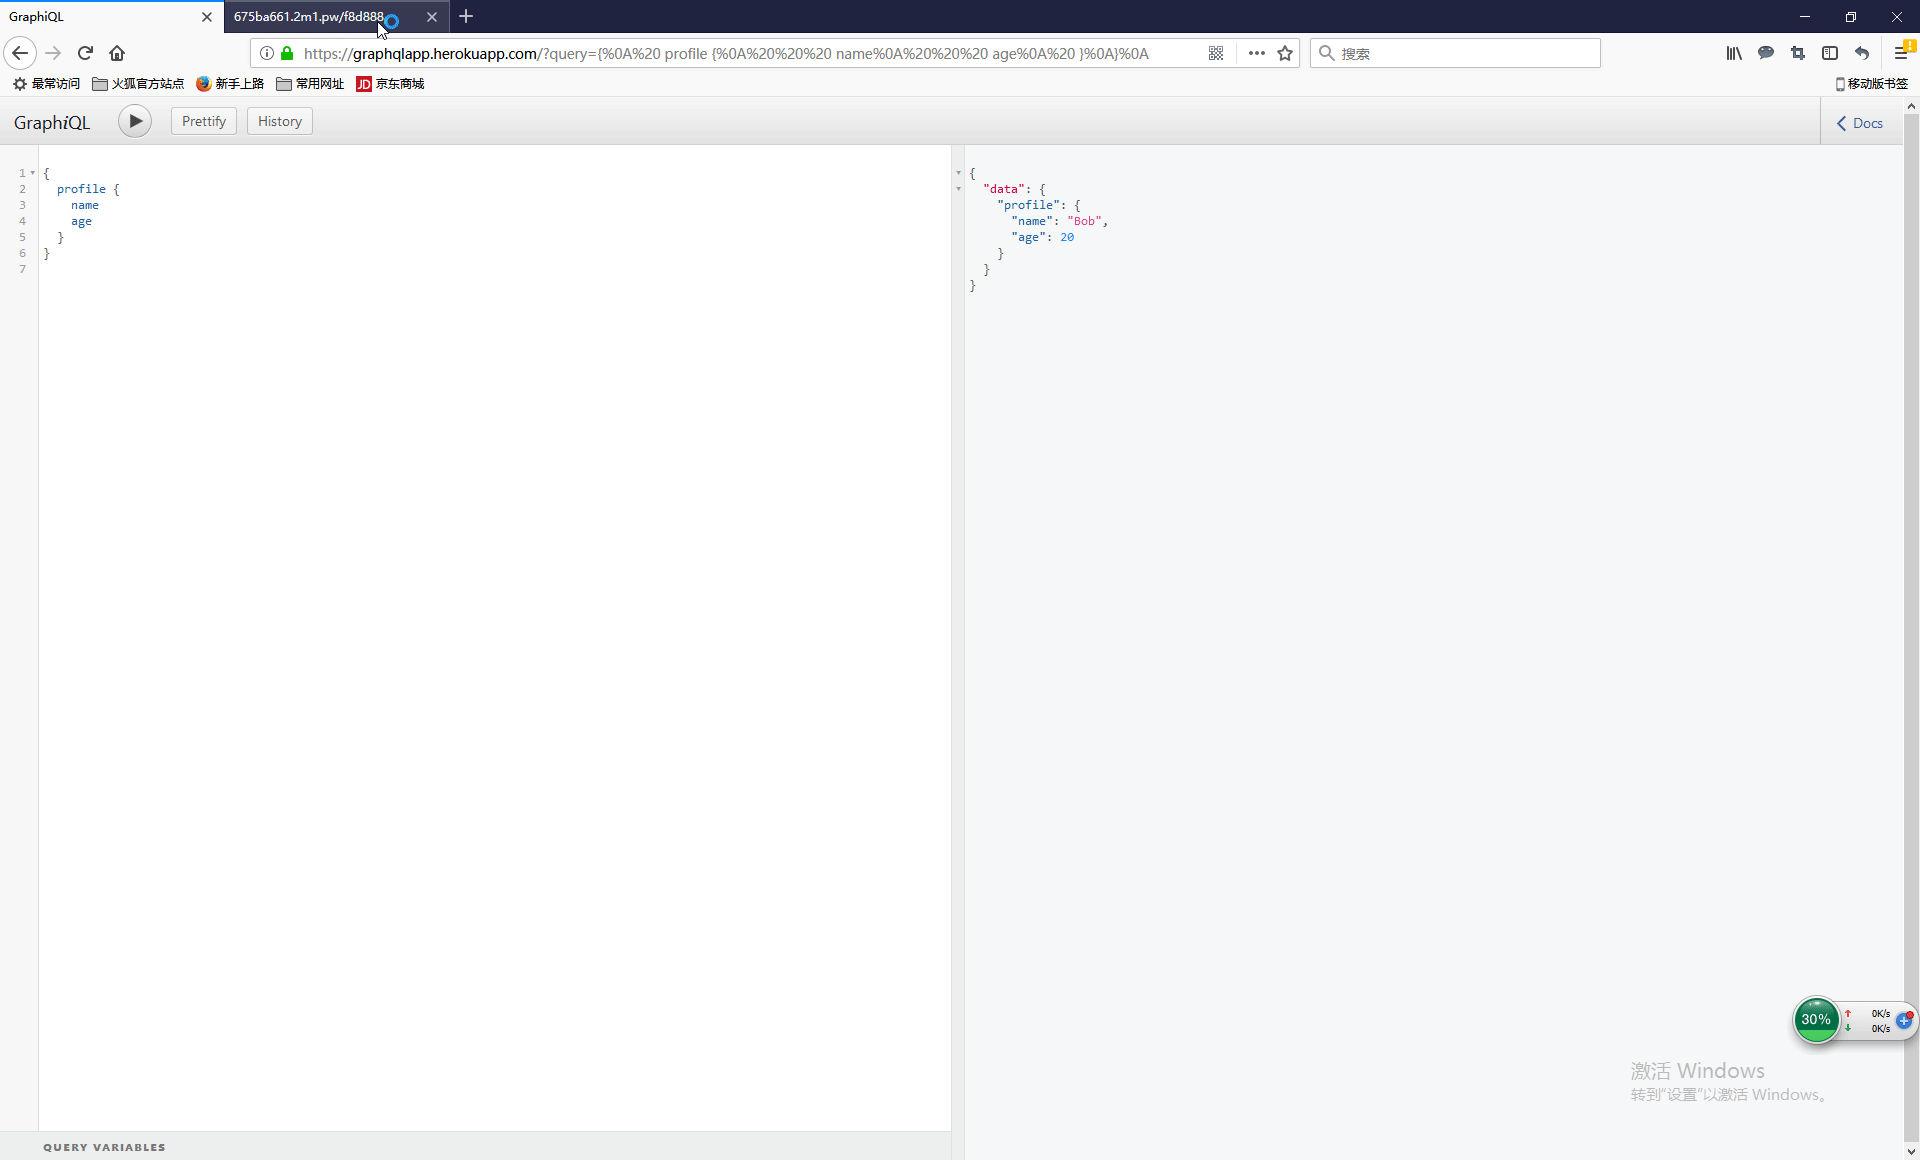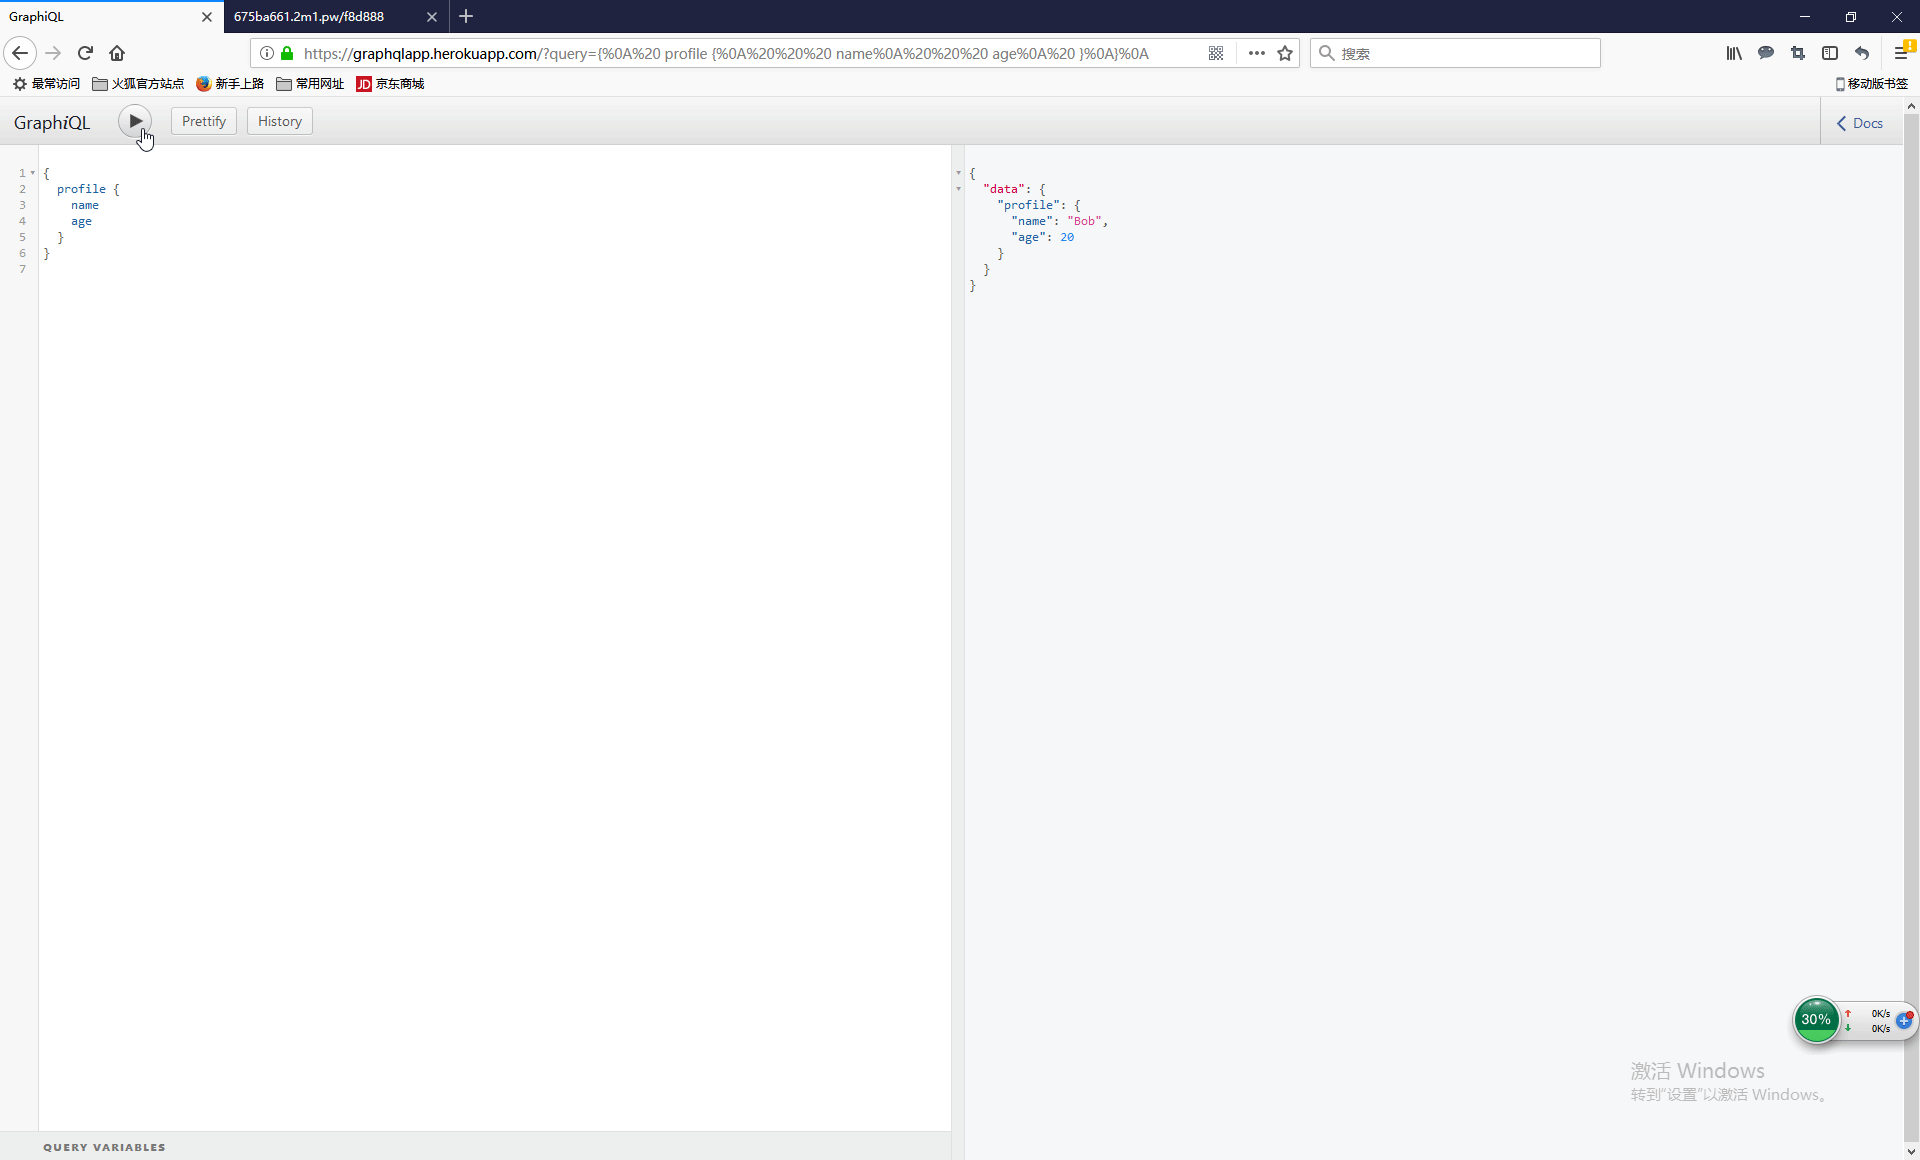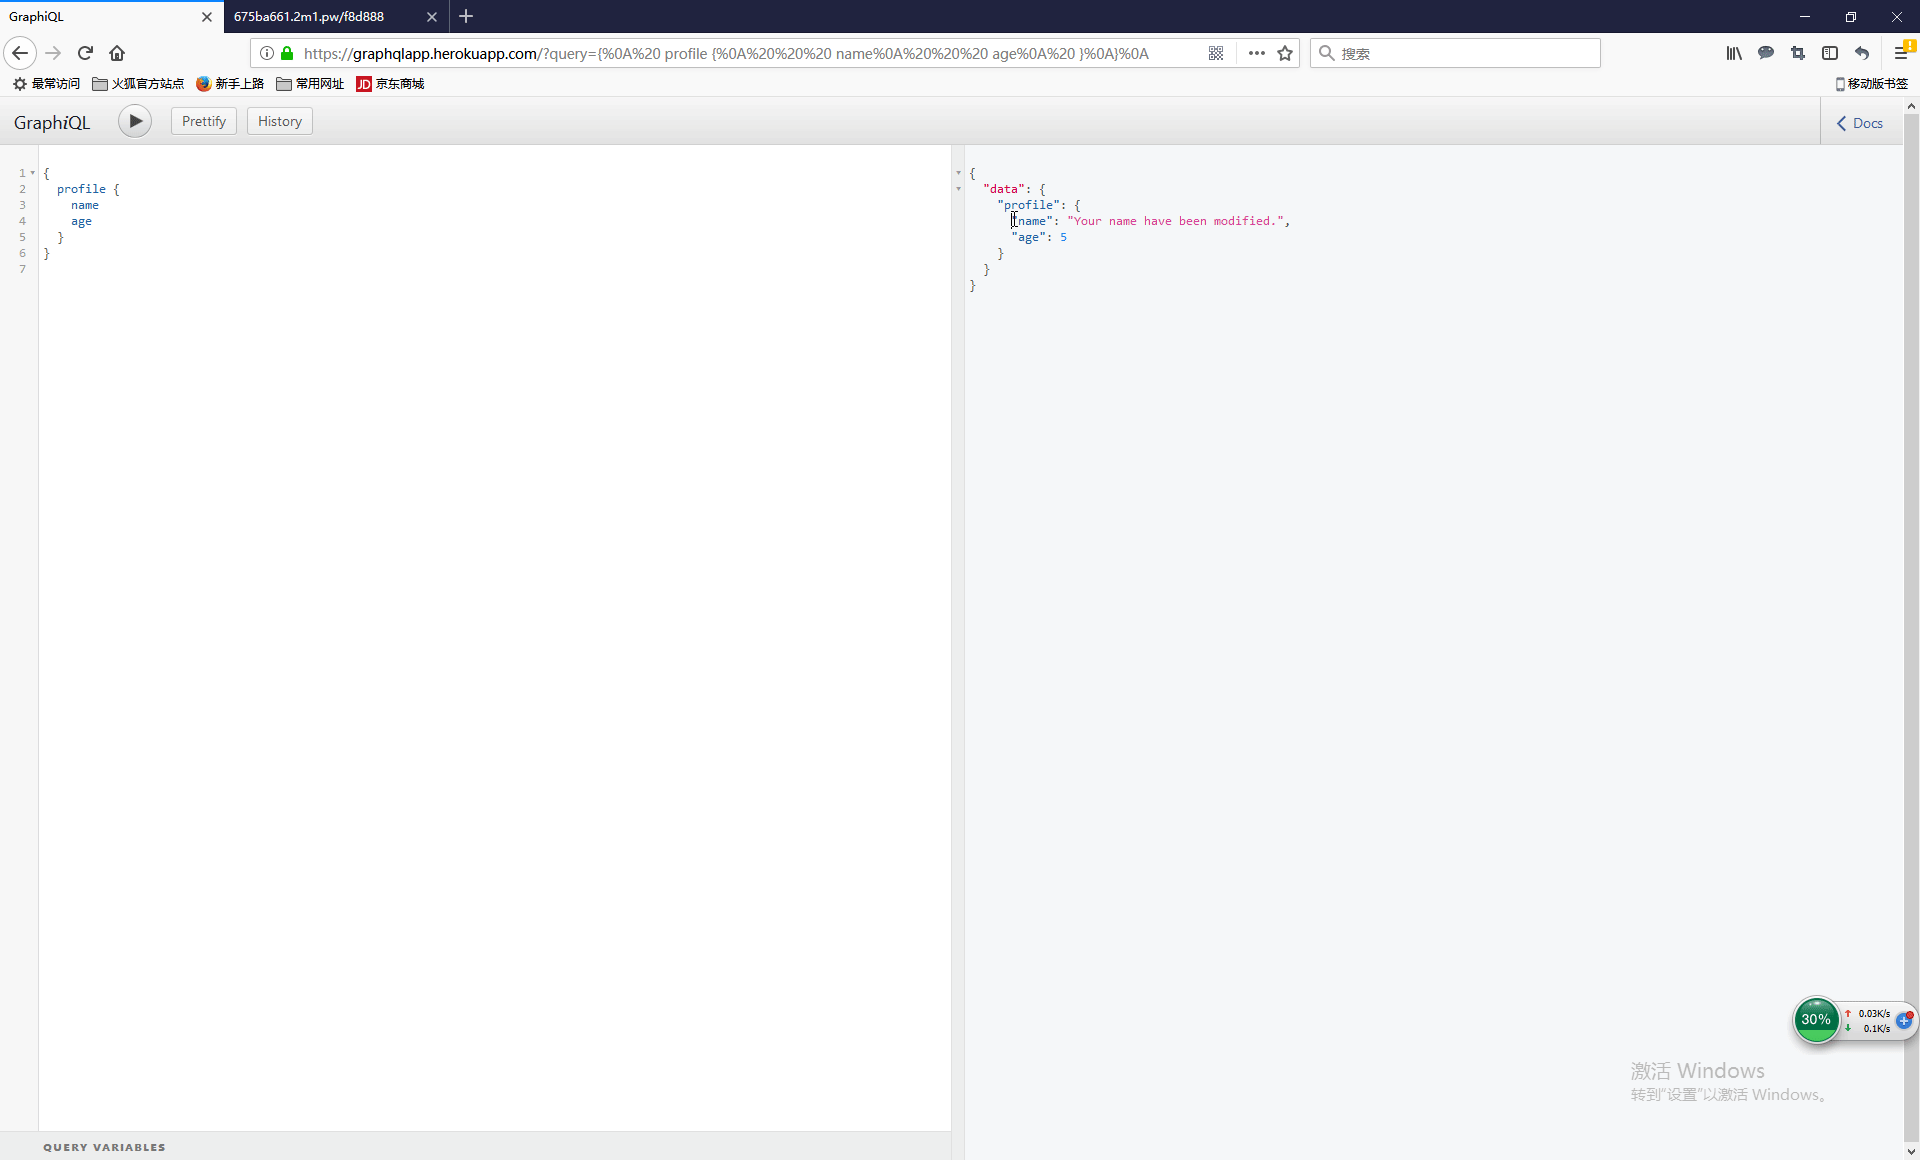
1. https://graphqlapp.herokuapp.com/?query=%7B%0A%20%20profile%20%7B%0A%20%20%20%20name%0A%20%20%20%20age%0A%20%20%7D%0A%7D%0A
2. http://675ba661.w1n.pw/f8d888
page 1 is the GraphiQL(using express-graphql), page 2 was created by attackers.
Open the page 1, you can see that your name is Bob at this time. After click the "*click*" button on page 2, your name will be changed to "*your name has been modified*" whithout your permission.
I recorded a screenshot for it:
Contributor guide
Assessment
This issue has not been assessed yet.