Ensure that CORS is set for the buckets holding static resources
- Dominant language
- JavaScript
- Stars
- 1.8k
- Forks
- 776
- PR merge metrics
- No merged PRs in 30d
Description
It seems that after a second update is deployed to a review env, there are a lot of CSRF errors in the browser, due to the fact that the CORS settings are not properly set in the browser:
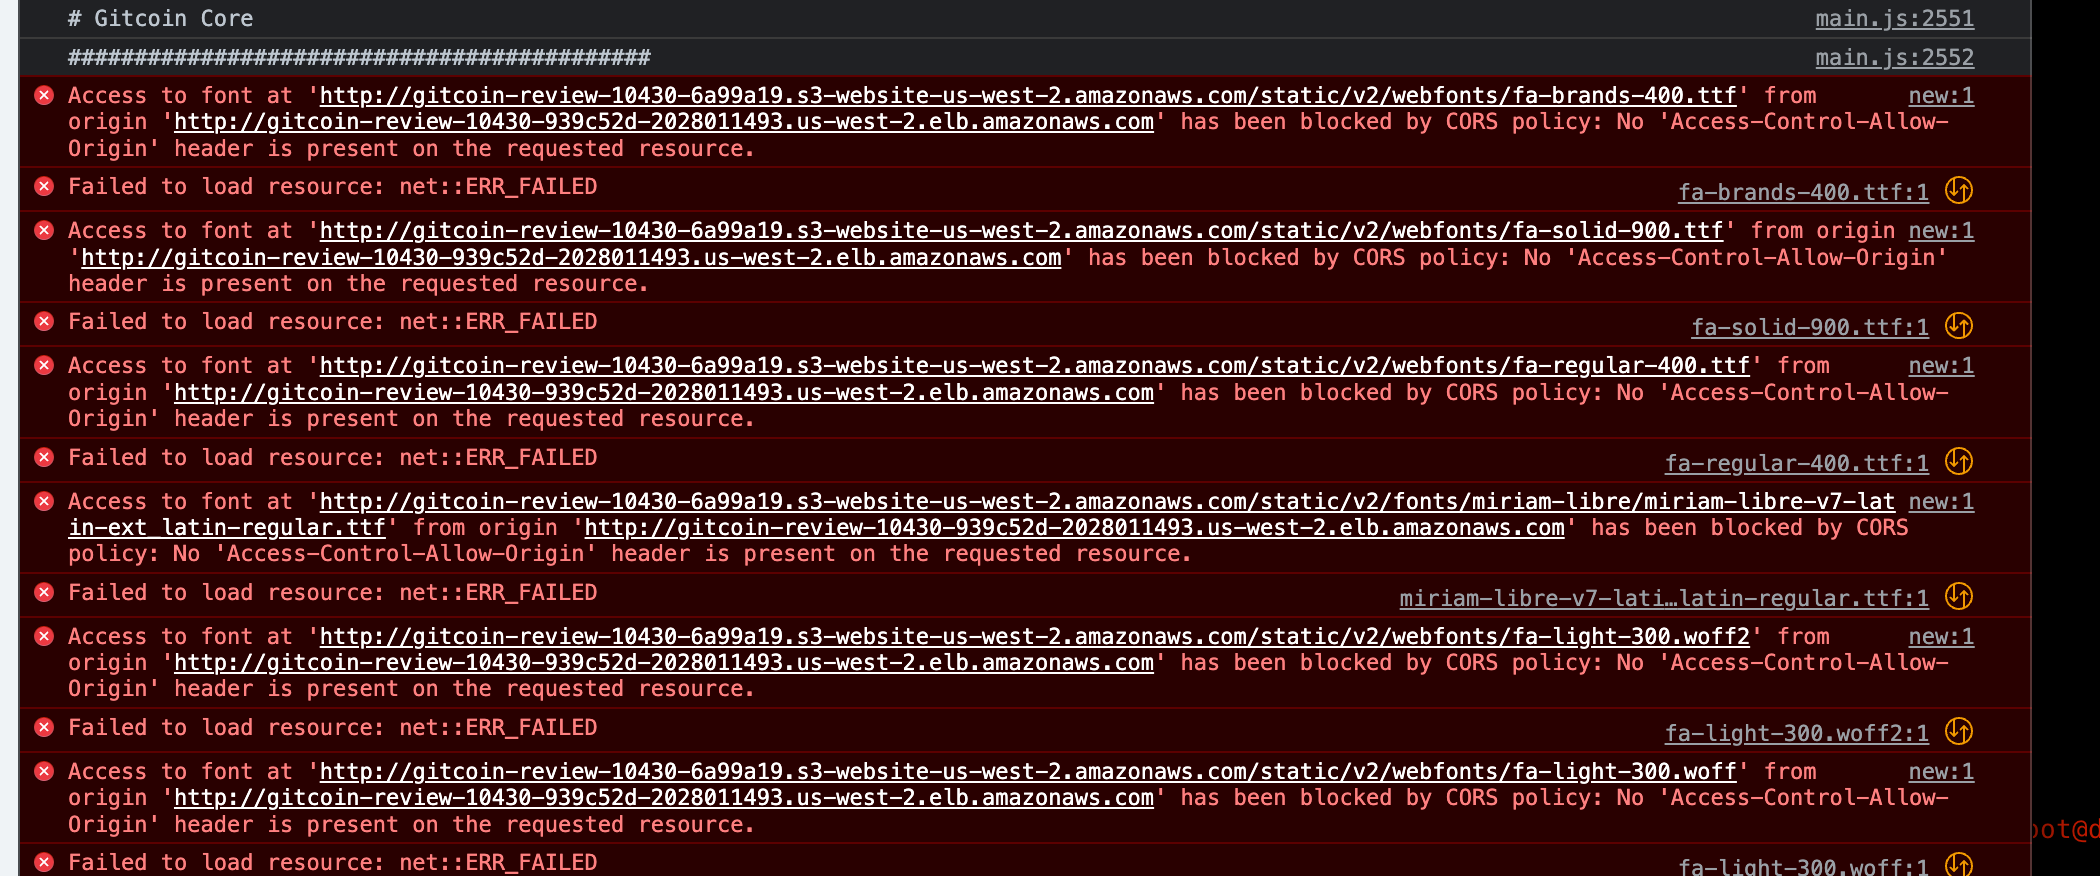
We would need the following settings:
```json
[
{
"AllowedHeaders": [
"Authorization"
],
"AllowedMethods": [
"GET",
"HEAD"
],
"AllowedOrigins": [
"*"
],
"ExposeHeaders": [
"Access-Control-Allow-Origin"
]
}
]
```
Contributor guide
Research direction
Start by locating the deployment or infrastructure configuration that creates the buckets holding static resources for review environments; the issue does not name a file or entry point. Apply the requested CORS settings there and verify that a second review-environment deployment no longer produces browser CORS errors when loading static resources.
Written by the indexing model from the issue text.
Assessment
- Domain
- cloud
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100