geonetwork / geonetwork/core-geonetwork
Keycloak issues when using Geonetwork 3.12.9 and Jetty
- Dominant language
- Java
- Stars
- 521
- Forks
- 514
- Avg merge
- 6d 13h
- Merged PRs (30d)
- 19
Description
I am trying to configure Keycloak 21.0.2 and Geonetwork 3.12.9 (Jetty). Keycloak connects to Azure AD using openid connect protocol.
Keycloak is running under docker and https (8443) and Geonetwork as standalone application using Jetty.
After entering my credentials into the login page, I got this:

And in the Jetty logs, the error is:
```
ERROR org.keycloak.adapters.OAuthRequestAuthenticator - failed to turn code into token
javax.net.ssl.SSLHandshakeException: PKIX path building failed: sun.security.provider.certpath.SunCertPathBuilderException: unable to find valid certification path to requested target
```
At keycloak level, I am using as redirects URLs:
https://localhost:8443/realms/my-realm/broker/azuread/endpoint*
http://localhost:8081/geonetwork/*
The keycloak.json is:
```
{
"realm": "my-realm",
"auth-server-url": "https://localhost:8443/",
"ssl-required": "external",
"resource": "client",
"credentials": {
"secret": "my-secret"
},
"confidential-port": 0,
"use-resource-role-mappings" : true
}
```
I succesfully reach this screen:
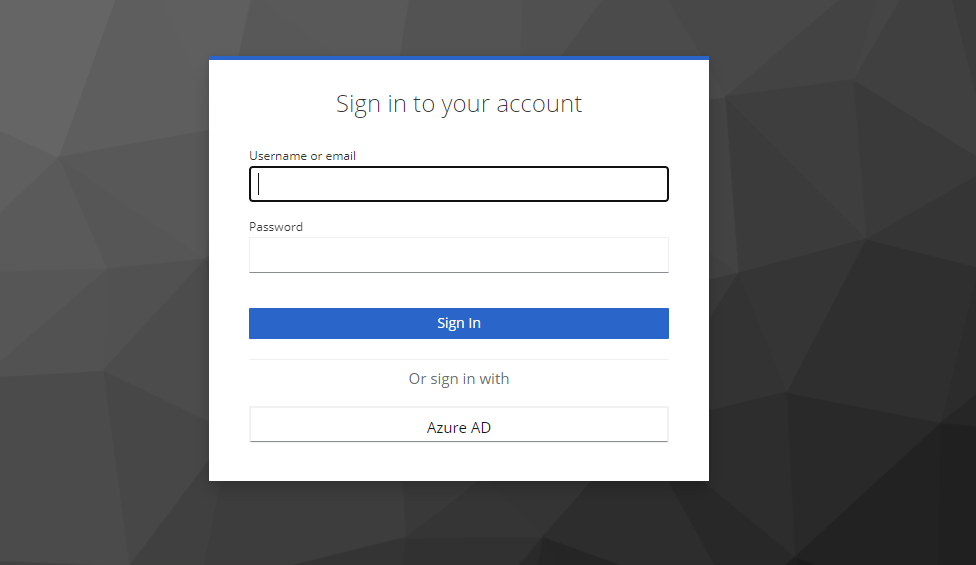
But after entering my credentials using the Azure AD button, I am presented with the above 403 error.
Contributor guide
Research direction
Start with keycloak.json and the Jetty log entry showing the SSLHandshakeException, then trace the callback flow for the Azure AD login using the listed redirect URLs. Confirm the Keycloak-to-GeoNetwork exchange completes successfully without the certificate-path error or the resulting 403 response.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- docker, java
- Domain
- authentication, backend, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100