elastic / elastic/integrations
Elasticsearch integration mapping/field inconsitencies
- Dominant language
- Handlebars
- Stars
- 333
- Forks
- 647
- Avg merge
- 2d 18h
- Merged PRs (30d)
- 182
Description
There are some field type inconsistencies between the `System` integration and the `Elasticsearch` integration. This leads Kibana to show the message:
````
Mapping conflict
A field is defined as several types (string, integer, etc) across the indices that match this pattern. You may still be able to use these conflict fields in parts of Kibana, but they will be unavailable for functions that require Kibana to know their type. Correcting this issue will require reindexing your data.
````
It is looking similar to https://github.com/elastic/integrations/issues/1573 and I think it makes the `Elasticsearch` integration non-ECS complaint, which I suppose should be considered a bug.
Checking those conflicts manually, we get the following details.
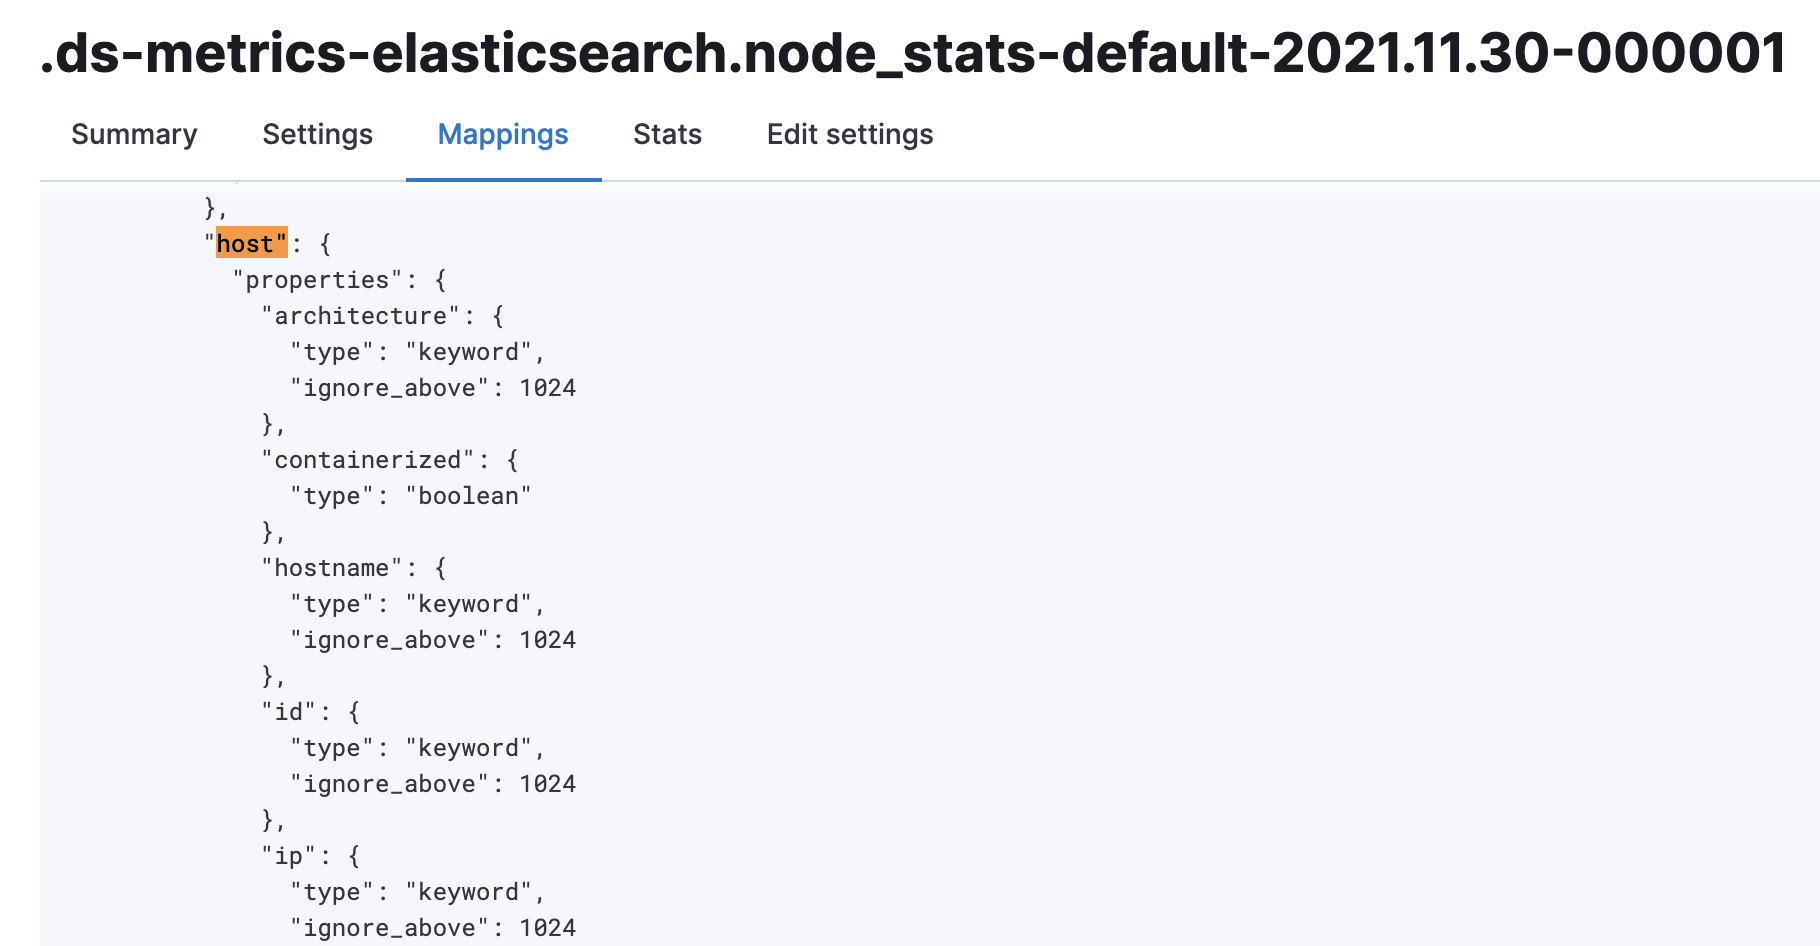
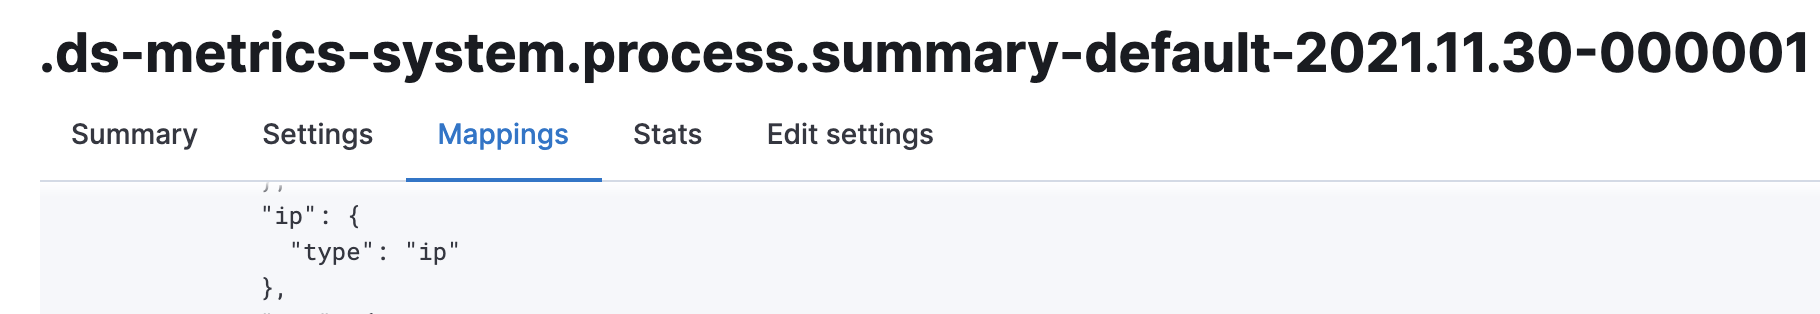
For `metrics-*`:
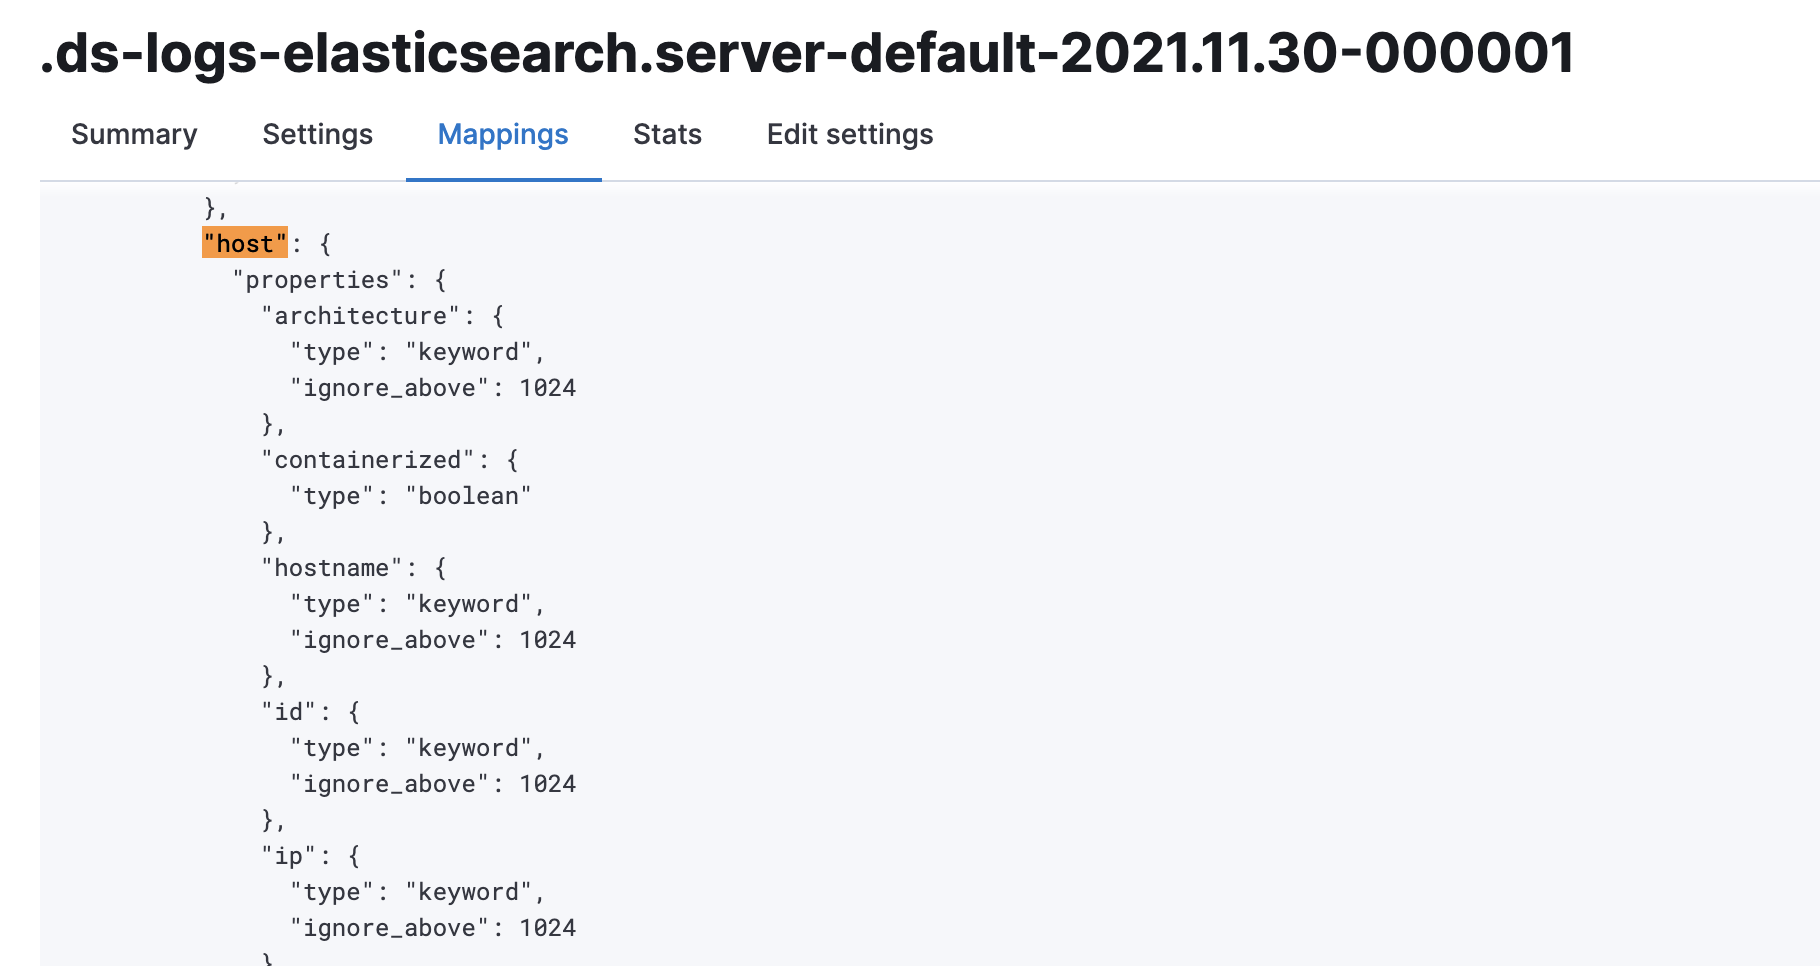
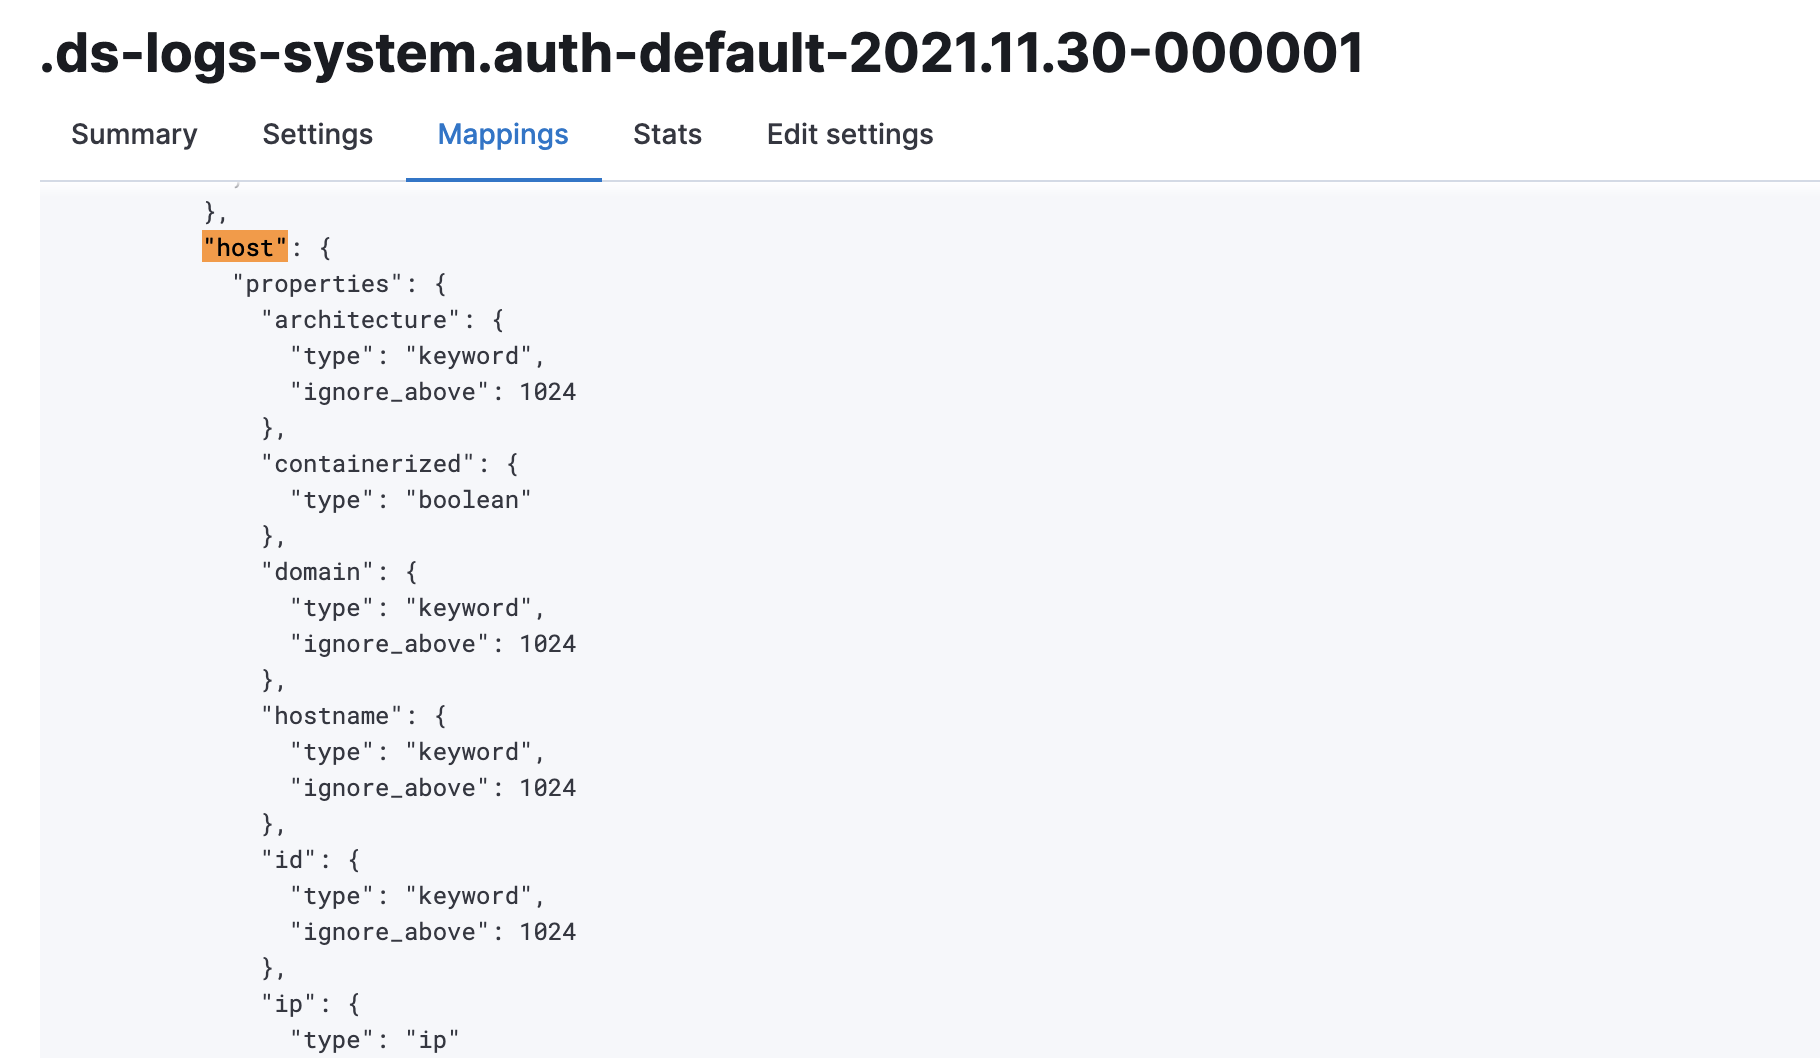
- `host.ip` maps to a `keyword` ❗ vs. `ip` ✅ in the System package
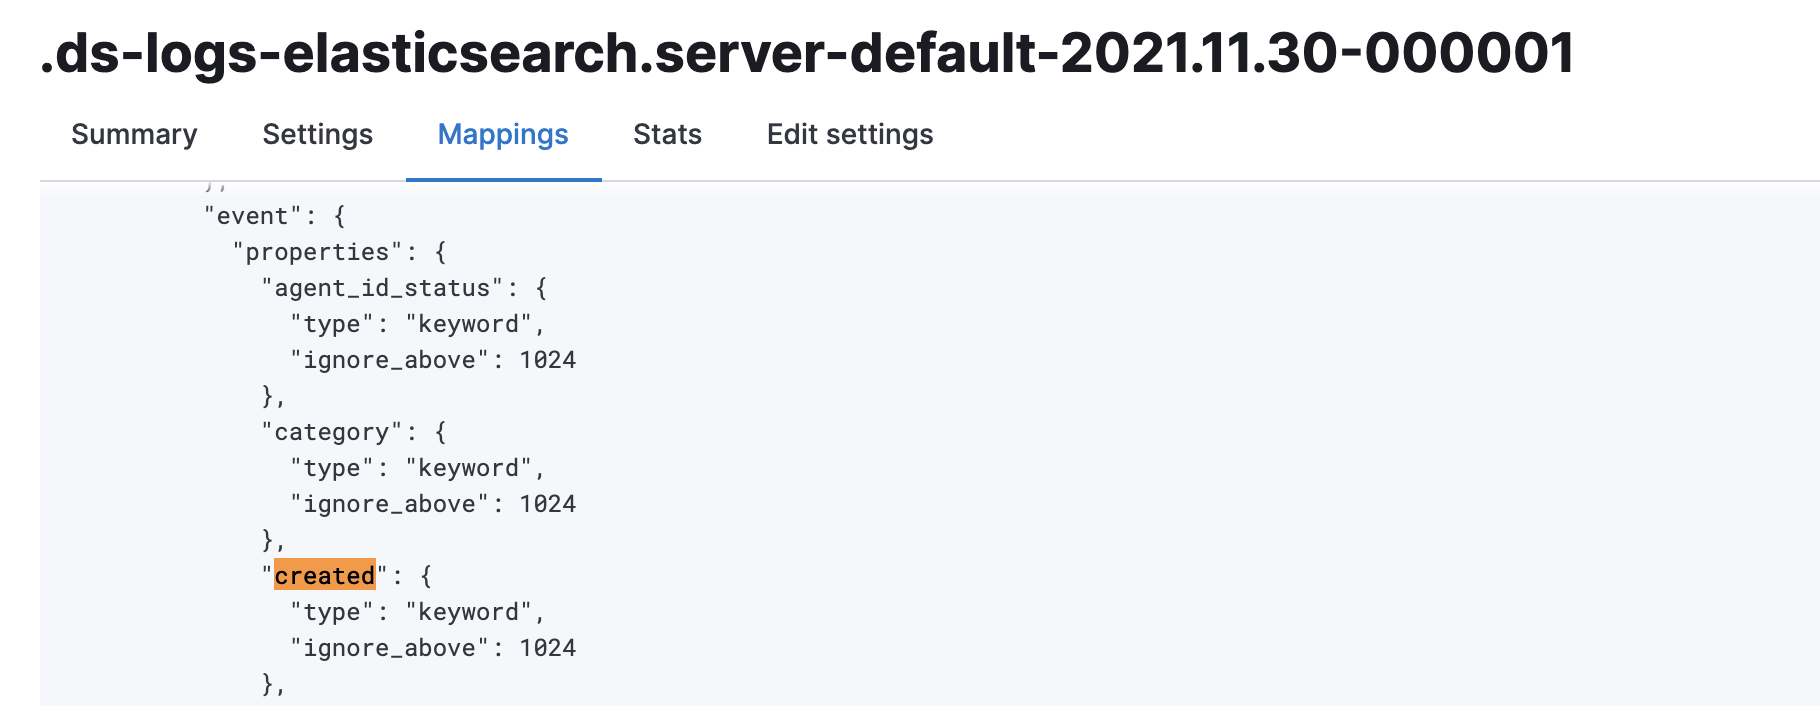
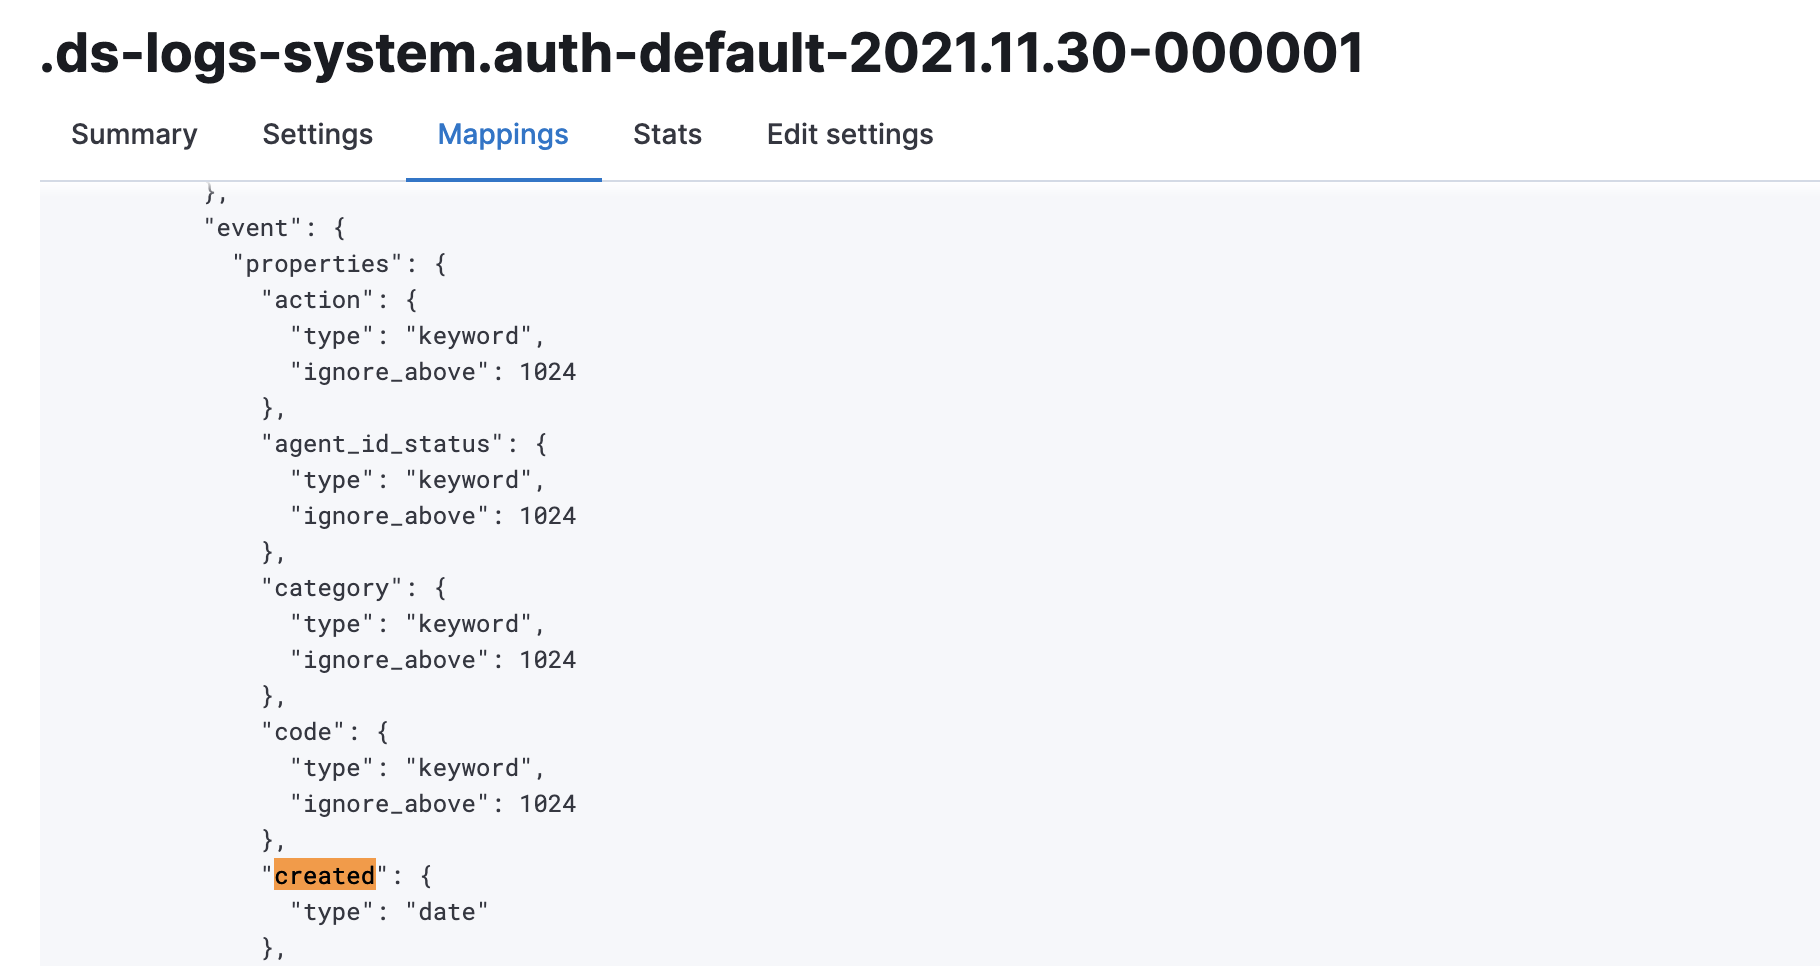
For `logs-*`:
- `event.created` maps to `keyword` ❗ vs. `date` ✅ in the System package
- `host.ip` maps to a `keyword` ❗ vs. `ip` ✅ in the System package
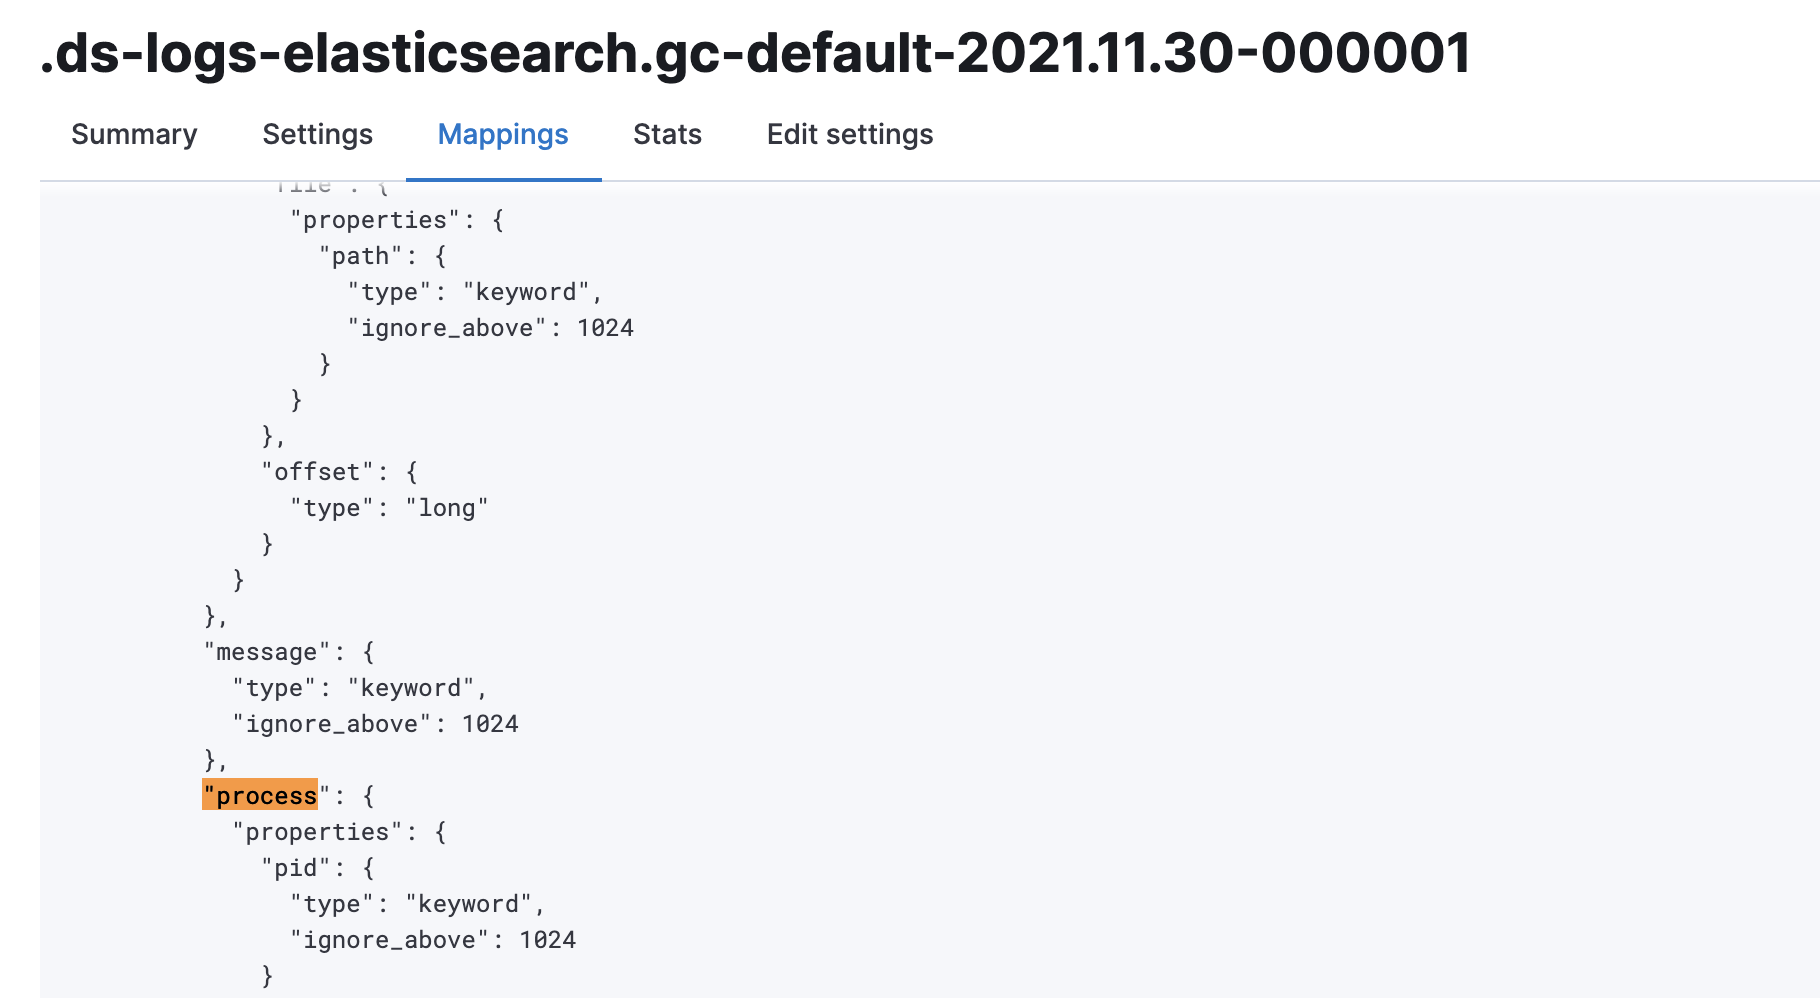
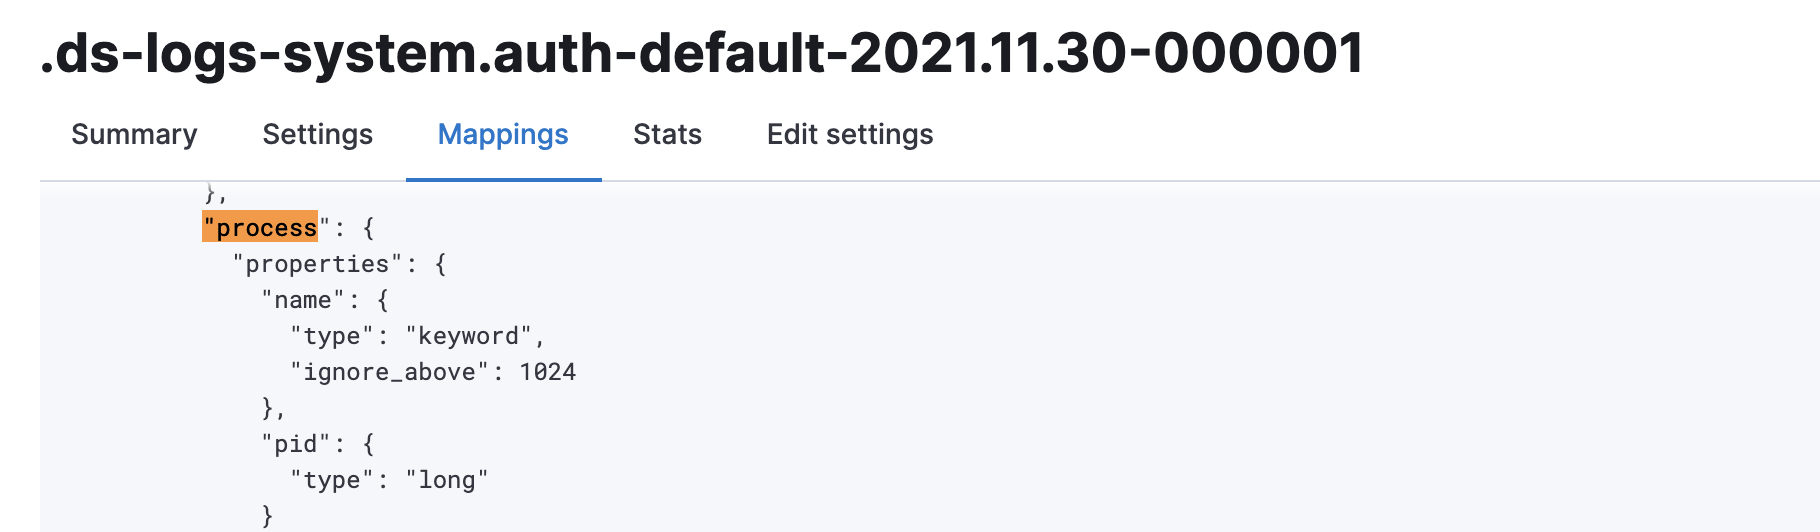
- `process.pid` maps to a `keyword` ❗ vs. `long` ✅ in the System package
Contributor guide
Assessment
This issue has not been assessed yet.