Why? What? Who? How?
- Dominant language
- No language data
- Stars
- 8
- Forks
- 0
- PR merge metrics
- No merged PRs in 30d
Description
# Why?
As noted in https://github.com/dwyl/learn-security/issues/73 the primary reason for using OpenBSD is the "**_secure_ by `default`**" philosophy.
Rather than trying to "harden" Linux, see: https://en.wikipedia.org/wiki/Hardening_(computing) or use a Linux distro that purports to be "secure" but in reality is immature, I prefer to _start_ with a base that is widely regarded as the most secure OS.
# What?
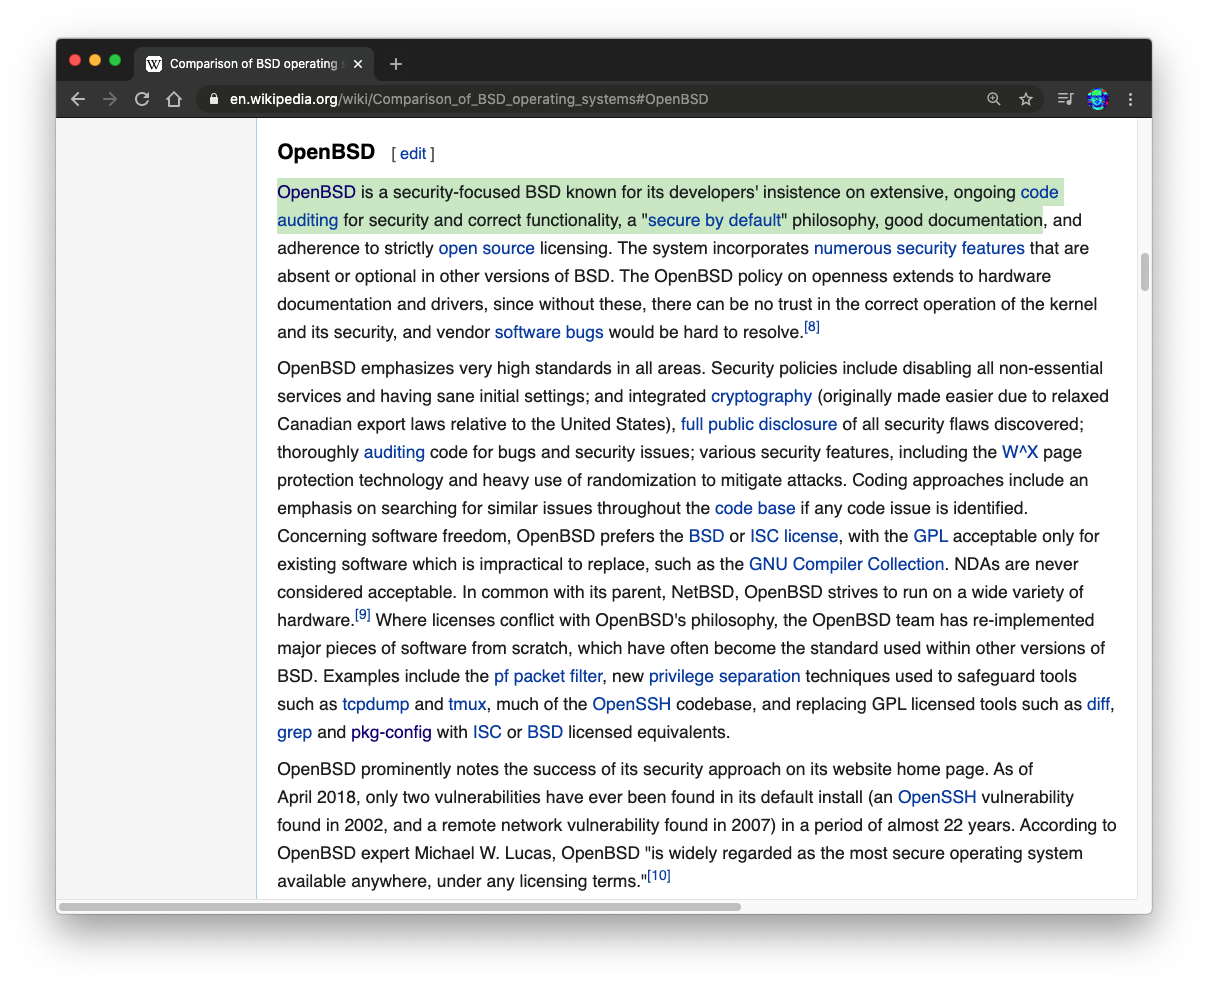
OpenBSD is a security-focused BSD known for its developers' insistence on extensive, ongoing code auditing for security and correct functionality, a "secure by default" philosophy.
https://en.wikipedia.org/wiki/Comparison_of_BSD_operating_systems#OpenBSD
# How?
Thinking of reading the book: **Absolute OpenBSD, 2nd Edition**: #2
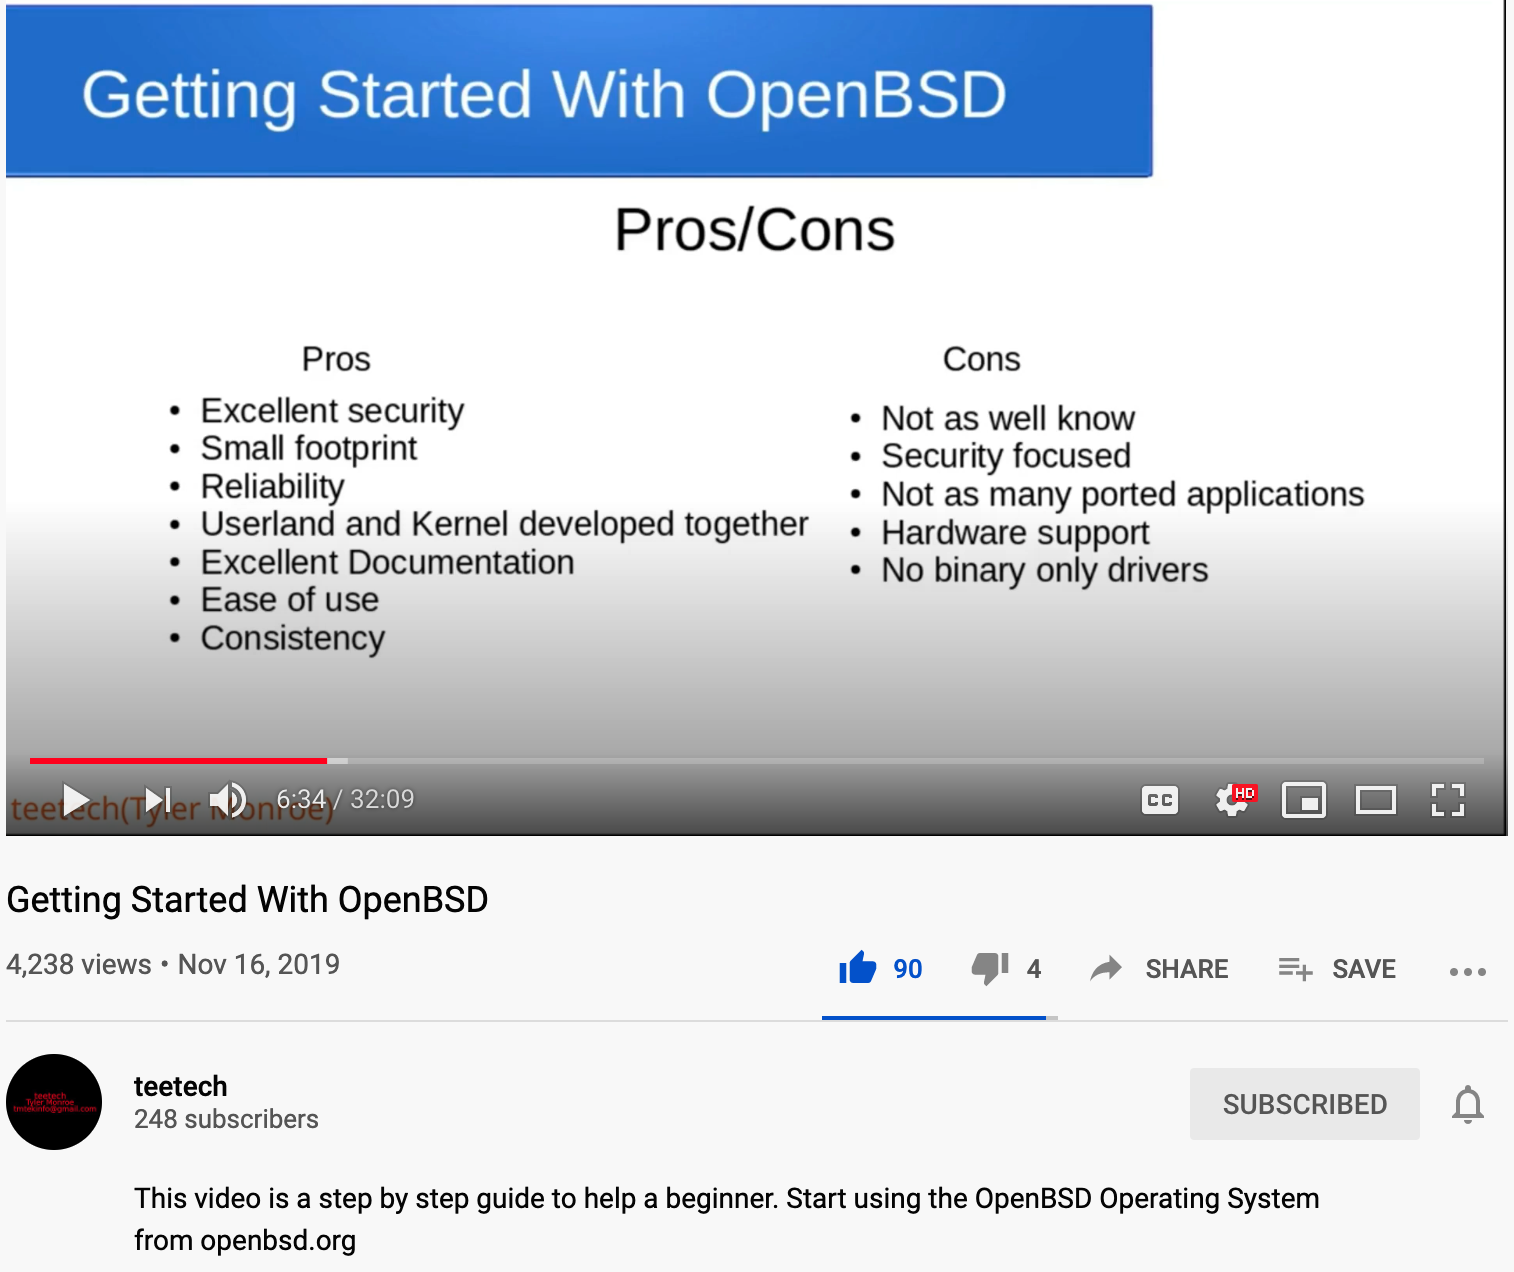
Getting Started With OpenBSD: https://youtu.be/N_6Xs_R3ckM
[](https://youtu.be/N_6Xs_R3ckM0
Even if it takes me a _month_ to learn OpenBSD I think it will end up being a wise investment in the security of our App(s) if it helps to prevent an attacker from gaining access to our production database.
Yes, it will mean fewer people can _support_ our DevOps because [less than 0.1%](https://w3techs.com/technologies/details/os-openbsd) of the Internet uses OpenBSD,
but again, the security
Decent list of resources: https://github.com/ligurio/awesome-openbsd
Contributor guide
No contributing guide indexed for this repository
Assessment
This issue has not been assessed yet.