manifest create not working with --insecure when registry listen on 80
Nobody has claimed this yet.
- Dominant language
- Go
- Stars
- 6.1k
- Forks
- 2.2k
- Avg merge
- 1d 15h
- Merged PRs (30d)
- 43
Description
Description
ubuntu@VM-0-131-ubuntu:~$ docker -D manifest create --insecure  registry.tke.com/library/buildx:latest registry.tke.com/library/buildx:latest-arm64 registry.tke.com/library/buildx:latest-amd64
DEBU[0000] allowing insecure registry for: registry.tke.com
DEBU[0000] endpoints for registry.tke.com/library/buildx:latest-arm64: [{false https://registry.tke.com v2 false false true 0xc420640780} {false http://registry.tke.com v2 false false true 0xc420640780} {false https://registry.tke.com v1 false false true 0xc420640900} {false http://registry.tke.com v1 false false true 0xc420640900}]
DEBU[0000] not continuing on error (*url.Error) Get https://registry.tke.com/v2/library/buildx/manifests/latest-arm64: dial tcp 127.0.0.1:443: connect: connection refused
Get https://registry.tke.com/v2/library/buildx/manifests/latest-arm64: dial tcp 127.0.0.1:443: connect: connection refused
Possible bug:
cli/registry/client/fetcher.go:243
should try http endpoint in next step, but continueOnError return false when connect reset.
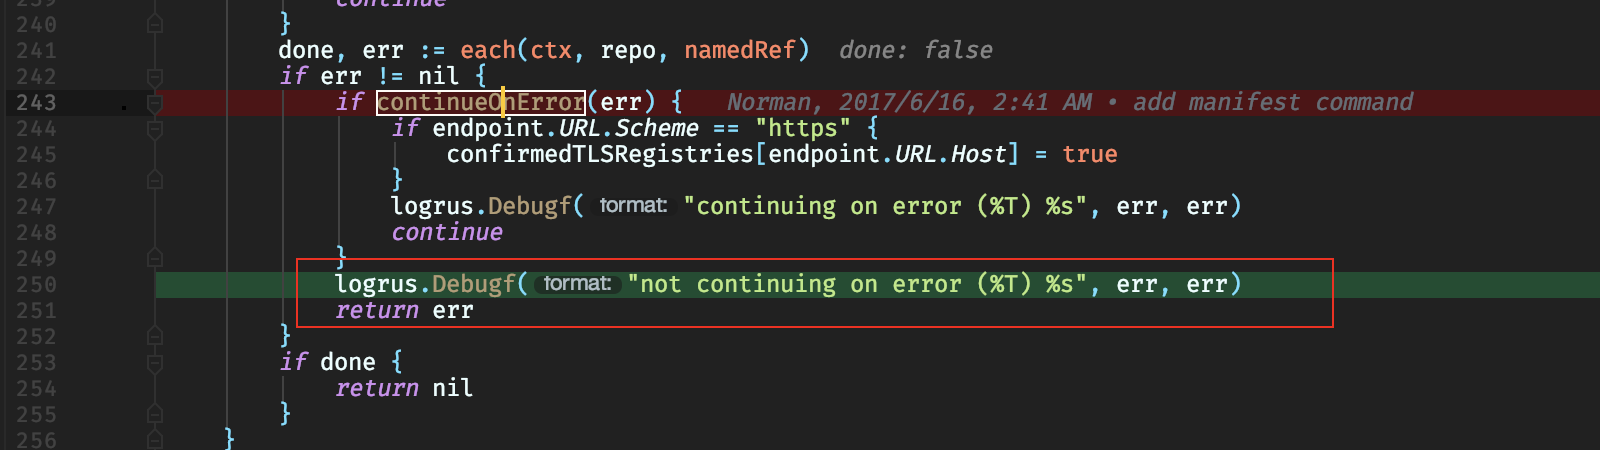
Describe the results you received:
not retry using http
Describe the results you expected:
retry using http
Additional information you deem important (e.g. issue happens only occasionally):
Output of docker version:
Client:
 Version:           18.09.7
 API version:       1.39
 Go version:        go1.10.1
 Git commit:        2d0083d
 Built:             Fri Aug 16 14:20:06 2019
 OS/Arch:           linux/amd64
 Experimental:      true

Server:
 Engine:
  Version:          18.09.7
  API version:      1.39 (minimum version 1.12)
  Go version:       go1.10.1
  Git commit:       2d0083d
  Built:            Wed Aug 14 19:41:23 2019
  OS/Arch:          linux/amd64
  Experimental:     true```

**Output of `docker info`:**
Containers: 2
Running: 1
Paused: 0
Stopped: 1
Images: 1048
Server Version: 18.09.7
Storage Driver: overlay2
Backing Filesystem: extfs
Supports d_type: true
Native Overlay Diff: true
Logging Driver: json-file
Cgroup Driver: cgroupfs
Plugins:
Volume: local
Network: bridge host ipvlan macvlan null overlay
Log: awslogs fluentd gcplogs gelf journald json-file local logentries splunk syslog
Swarm: inactive
Runtimes: runc
Default Runtime: runc
Init Binary: docker-init
containerd version:
runc version: N/A
init version: v0.18.0 (expected: fec3683b971d9c3ef73f284f176672c44b448662)
Security Options:
apparmor
seccomp
Profile: default
Kernel Version: 4.15.0-54-generic
Operating System: Ubuntu 18.04.1 LTS
OSType: linux
Architecture: x86_64
CPUs: 16
Total Memory: 31.26GiB
Name: VM-0-131-ubuntu
ID: RRFF:BEU6:UHXM:D4DL:B73E:AP3V:ZXG7:R7DK:6V5Q:D2HI:R7WI:TQTW
Docker Root Dir: /var/lib/docker
Debug Mode (client): false
Debug Mode (server): false
Username: tkeci
Registry: https://index.docker.io/v1/
Labels:
Experimental: true
Insecure Registries:
registry.tke.com
tke3.global.registry.tke.com
127.0.0.0/8
Live Restore Enabled: false
WARNING: No swap limit support
**Additional environment details (AWS, VirtualBox, physical, etc.):**
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Read cli/registry/client/fetcher.go around line 243, then reproduce the issue with docker -D manifest create --insecure against a registry listening on port 80. Done means the manifest command retries the HTTP endpoint after the HTTPS connection failure; add or update coverage if the surrounding code provides tests.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- go
- Domain
- cli, networking
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 42/100