dependency-check / dependency-check/DependencyCheck
dependency-check report shows in column 'Highest severity' MEDIUM while CVSSv2 has value 8.5 (CVSSv3 has value 6.6)
- Dominant language
- Java
- Stars
- 7.7k
- Forks
- 1.4k
- Avg merge
- 9d 22h
- Merged PRs (30d)
- 13
Description
**Describe the bug**
The Gradle plugin fails with a found vulnerability with value greater than 7.0 during the analyze step:
_Dependency-Analyze Failure:
One or more dependencies were identified with vulnerabilities that have a CVSS score greater than '7.0': CVE-2021-42550
See the dependency-check report for more details._
When I then look at the dependency-check report, I only see vulnerabilities with as 'Highest severity' the value MEDIUM. While I would expect a value of HIGH (because the analyze failed).
See screenshot:

When clicking on the logback-core-1.3.0.jar link, it shows (amongst others):
_CVSSv2:
Base Score: HIGH (8.5)
Vector: /AV:N/AC:M/Au:S/C:C/I:C/A:C
CVSSv3:
Base Score: MEDIUM (6.6)
Vector: CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:U/C:H/I:H/A:H_
See screenshot:
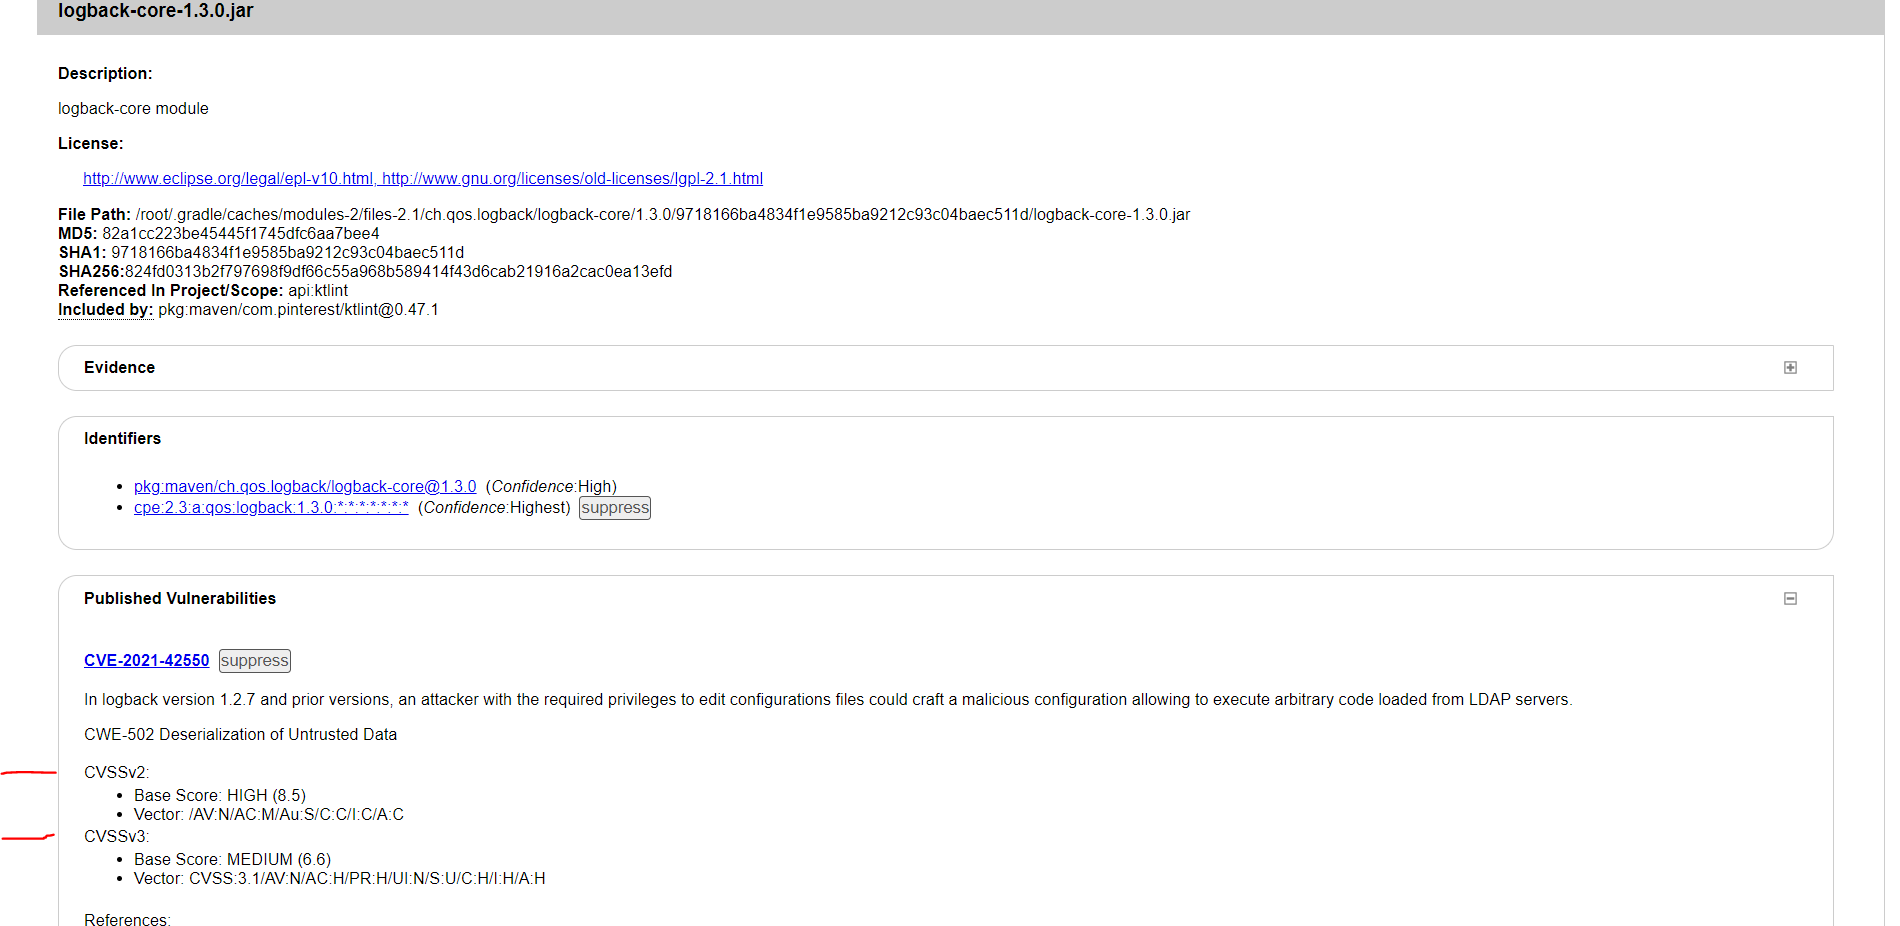
Note that the CVSSv2 score is 8.5 and the CVSSv3 is 6.6. It seems the plugin checks only for the status of the CVSSv3 value? That would be fine if it wouldn't fail the plugin analyze phase on reporting there is a vulnerability with score greater than 7.0 (which indicates a severity of value HIGH).
A solution could be: take the highest of the two CVSS scores and show that in the report column "Highest severity"? So in this case it would show HIGH (not MEDIUM)
**Version of dependency-check used**
The problem occurs using version 7.4.4 and 8.1.2 of the gradle plugin.
**Log file**
Only for now adding the reason why the job (plugin) is failing:
_Dependency-Analyze Failure:
One or more dependencies were identified with vulnerabilities that have a CVSS score greater than '7.0': CVE-2021-42550
See the dependency-check report for more details._
**To Reproduce**
Steps to reproduce the behavior:
1. Have logback-core-1.3.0.jar as dependency in your project and configure the plugin like this:
_dependencyCheck {
failBuildOnCVSS = 7
failOnError = true
}_
3. Run the scan: ./gradlew dependencyCheckAggregate --no-daemon --stacktrace
4. That should fail with the message "One or more dependencies were identified with vulnerabilities that have a CVSS score greater than '7.0': CVE-2021-42550"
5. Open the resulting report dependency-check-report.html
6. See above reported logback-core-1.3.0.jar and the value MEDIUM in the 'Highest severity' column.
**Expected behavior**
Show in the report in the 'Highest severity' column the highest of the CVSSv2 and CVSSv3 score, in this example thus showing HIGH. This would be very useful because I use that column to sort on anything that is HIGH or more critical, to know where to focus on first. Now it won't show me the HIGHs always looking at that column.
**Additional context**
Looks similar/related to https://github.com/jeremylong/DependencyCheck/issues/2462 but isn't exactly the same.
Contributor guide
Assessment
This issue has not been assessed yet.