deepfence / deepfence/ThreatMapper
Per process exploitability & potential attack paths
- Dominant language
- TypeScript
- Stars
- 5.3k
- Forks
- 631
- PR merge metrics
- No merged PRs in 30d
Description
Problem:
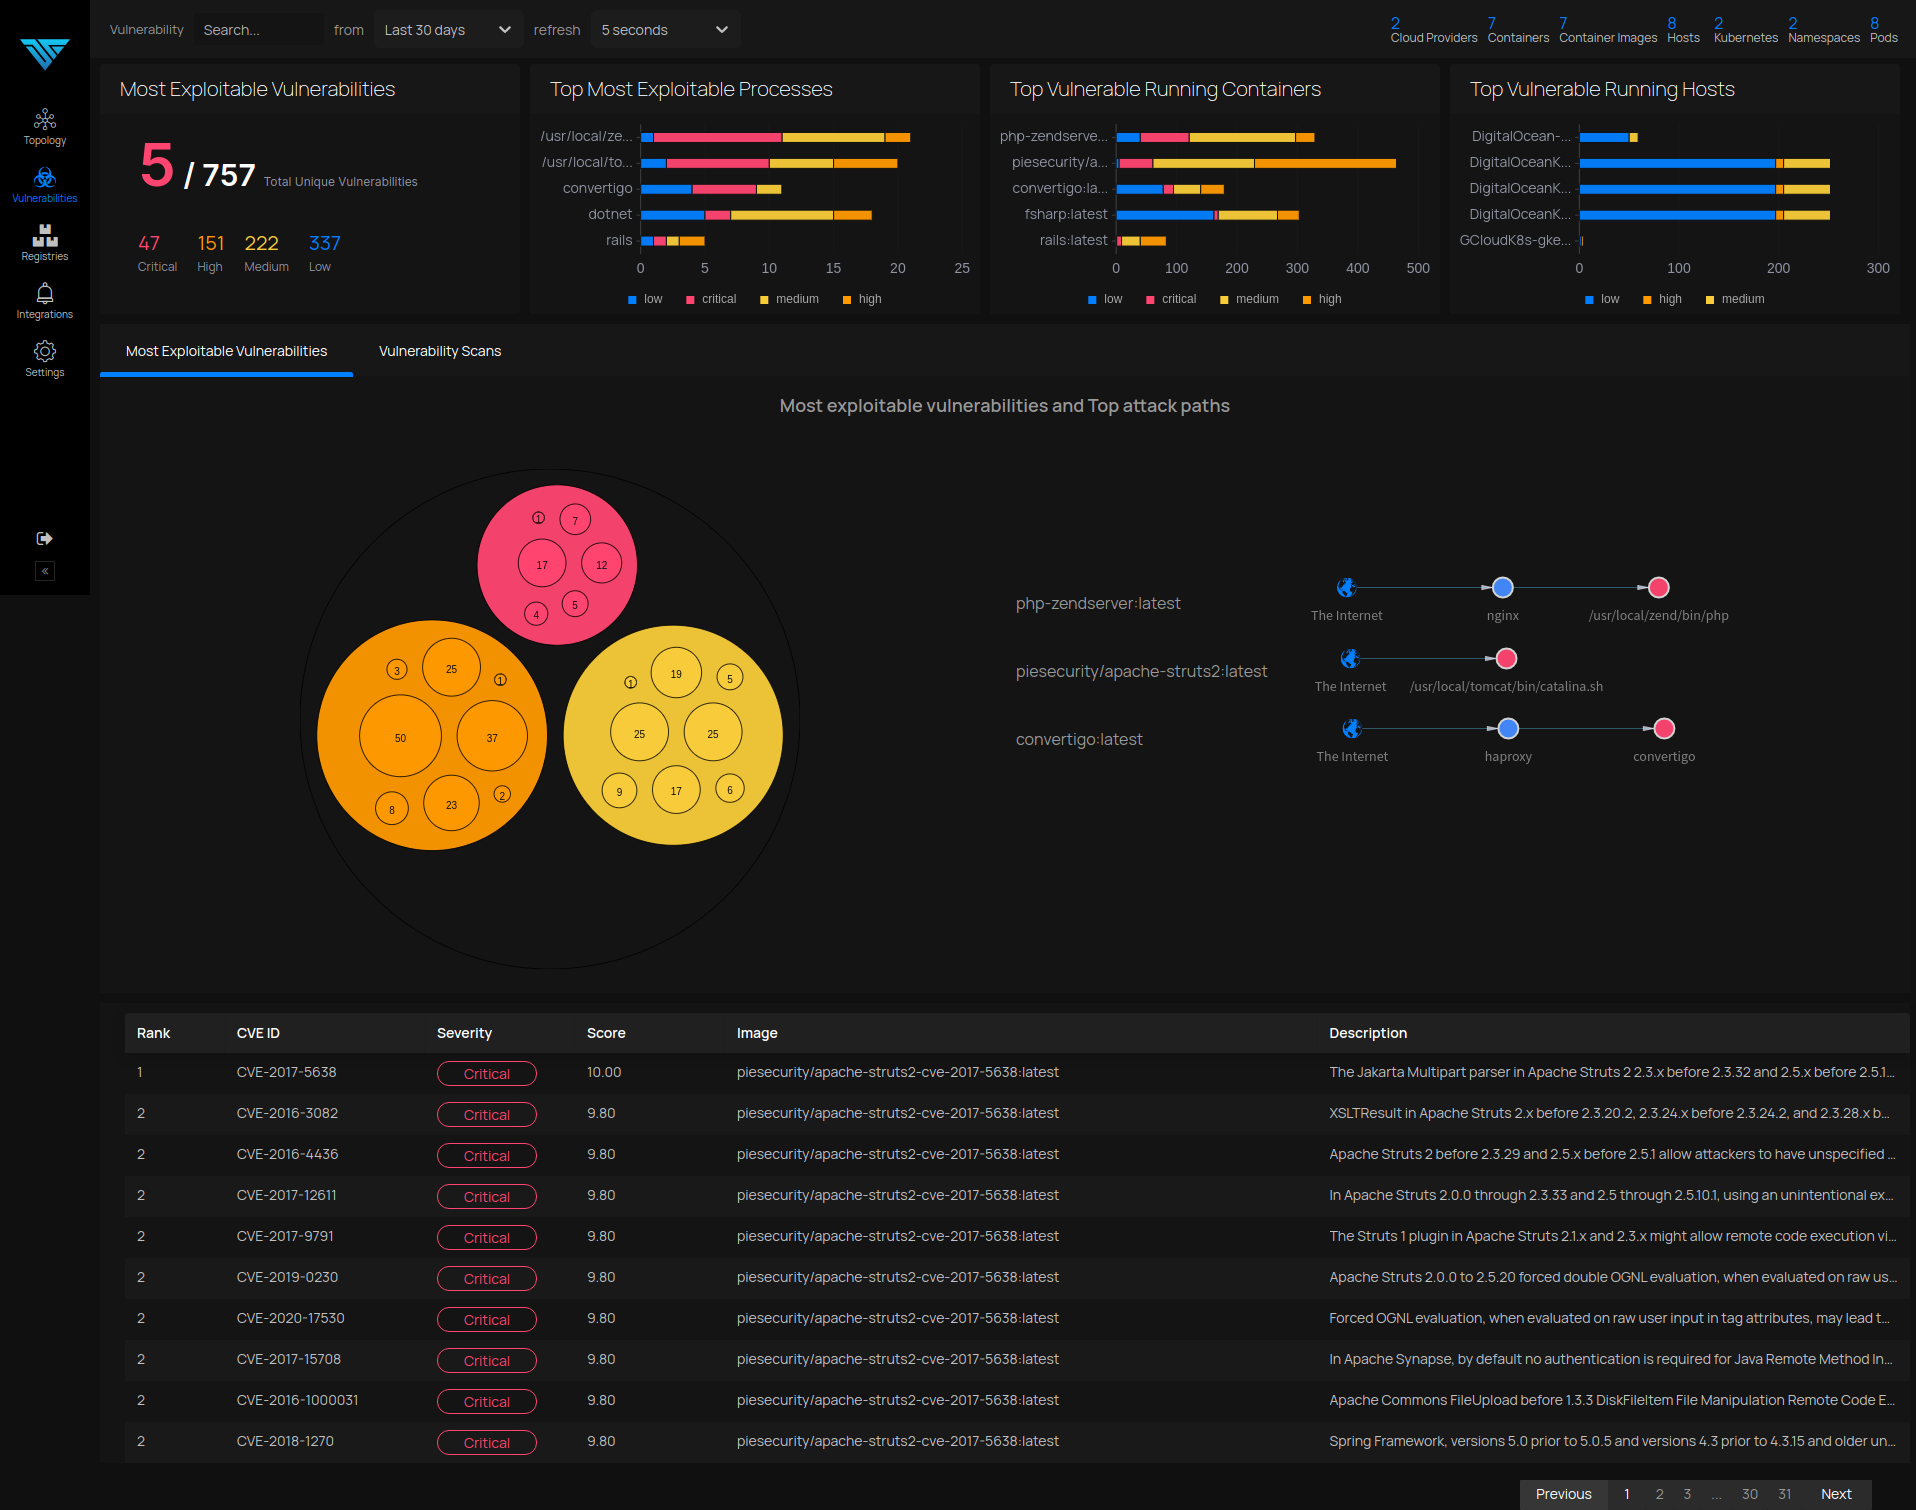
Currently we show most exploitable vulnerabilities per running container and per host. While this helps significantly in prioritisation it can be further improved by adding per process runtime context like which libraries, dependencies are directly are loaded in memory and which of those processes are directly/indirectly doing network I/O.
E.g. At infra level many 1000s of CVEs, per host 100s of them, per container many dozens still but per process this will be a. handful of CVEs so users can prioritise based on criticality of these processes.
Essentially two things here:
A) Track per process executable object and dependency loads (.jar, .py, .so, etc) and add to per process meta data. Essentially maintain a map of vulnerable packages loaded by processes which in turn ensure CVEs locked and loaded per process.
B) On console, overlay the CVEs per process and runtime context like network connections, number of hops from internet and the like.
Details to follow but here is a sample mock up.
Contributor guide
Assessment
This issue has not been assessed yet.