cloudflare / cloudflare/cloudflared
Truncated TCP response
- Dominant language
- Go
- Stars
- 15.6k
- Forks
- 1.4k
- PR merge metrics
- No merged PRs in 30d
Description
We've been troubleshooting a misbehaving `Pi-hole <---> traefik <---> cloudflared` system [here](https://github.com/pi-hole/FTL/issues/1263) and found that `cloudflared` is misbehaving ultimately leading to a failure in DNSSEC validation for domain `bit.ly` inside Pi-hole.
Short summary: When issuing
```
dig @127.0.0.1 -p 5811 +tcp +dnssec DNSKEY ly
```
where `5811` is the port on which `cloudflared` is listening with
```
proxy-dns --address 0.0.0.0 --port 5811 --max-upstream-conns 1 --upstream https://dns11.quad9.net/dns-query
```
we receive an **empty reply** with the **TC bit set**:
```
; <<>> DiG 9.16.1-Ubuntu <<>> @127.0.0.1 -p 5811 +tcp +dnssec DNSKEY ly
; (1 server found)
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 12205
;; flags: qr tc rd ra ad; QUERY: 1, ANSWER: 0, AUTHORITY: 0, ADDITIONAL: 1
[...]
```
(see **`tc`** in `flags: qr tc rd ra ad`). Querying DNS servers such as `1.1.1.1` or `9.9.9.9` with the exact same `dig` command works as expected.
I recorded a pcap from the `dig` command above for easy troubleshooting: [pihole-traefik-udp-bug_cloudflared_1_2.zip](https://github.com/cloudflare/cloudflared/files/7796461/pihole-traefik-udp-bug_cloudflared_1_2.zip)
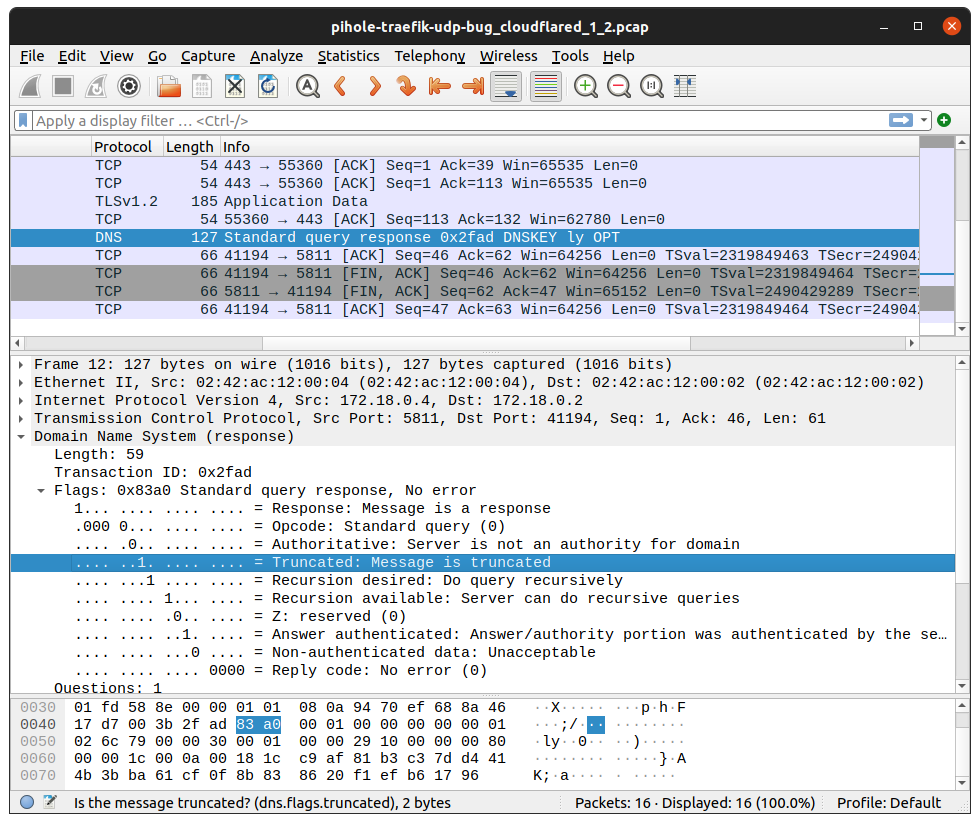
`cloudflared` is used as `docker` container: `raspbernetes/cloudflared:latest`
How can a response over TCP be truncated?
Contributor guide
Assessment
This issue has not been assessed yet.