CFSSL sign gives error if CSR has SAN
- Dominant language
- Go
- Stars
- 9.5k
- Forks
- 1.2k
- PR merge metrics
- No merged PRs in 30d
Description
CFSSL sign gives error if CSR has SAN
CFSSL sign gives following error while create CSR with SAN using CFSSL.
```
{"code":9003,"message":"asn1: syntax error: data truncated"}
```
But If we create the CSR with OpenSSL with SAN and sign using CFSSL it works.
To reproduce that
*profiles.json*
```
{
"signing": {
"default": {
"expiry": "8760h"
},
"profiles": {
"client-server": {
"usages": [
"signing",
"key encipherment",
"client auth",
"server auth"
],
"expiry": "26280h",
"copy_extensions": true
}
}
}
}
```
*ca-csr.json*
```
{
"CN": "Root CA",
"key": {
"algo": "ecdsa",
"size": 521
},
"names": [
{
"C": "IN",
"O": "EnSquare Pvt. Ltd.,"
}
],
"ca": {
"expiry": "262800h"
}
}
```
*csr.json*
```
{
"CN": "Server",
"key": {
"algo": "ecdsa",
"size": 521
},
"names": [
{
"C": "IN",
"O": "EnSquare Pvt. Ltd.,"
}
],
"usages": [
"signing",
"key encipherment",
"client auth",
"server auth"
],
"extensions": [
{
"Id": [2, 5, 29, 17],
"Value": "ZW1haWw6YWJjQGV4YW1wbGUuY29t"
}
]
}
```
### Create CA
Create root ca
```
mkdir ca
cfssl gencert -initca ca-csr.json | cfssljson -bare ca/root-ca
```
### Create CSR
Create CSR with CFSSL and validate the same using openssl
```
cfssl genkey -config profiles.json csr.json | cfssljson -bare ca/server
openssl req -in ca/server.csr -text
```
### Sign CSR with CA
Sign the created CSR using root ca
```
cfssl sign -ca ca/root-ca.pem -ca-key ca/root-ca-key.pem -config profiles.json -profile client-server ca/server.csr | cfssljson -bare ca/server
```
Now got the following error

## Gen CSR with OpenSSL
Generate CSR using OpeenSSL and validate the same
```
openssl ecparam -out ec.pem -name secp521r1
openssl req -new -addext 'subjectAltName = email:abc@example.com' -subj '/C=IN/O=EnSquare Pvt. Ltd.,/CN=Server' -sha512 -newkey ec:ec.pem -out ca/openssl.csr -keyout ca/openssl-key.pem -nodes
openssl req -in ca/openssl.csr -text
```
Sign the created CSR using CFSSL
```
cfssl sign -ca ca/root-ca.pem -ca-key ca/root-ca-key.pem -config profiles.json -profile client-server ca/openssl.csr | cfssljson -bare ca/openssl
```
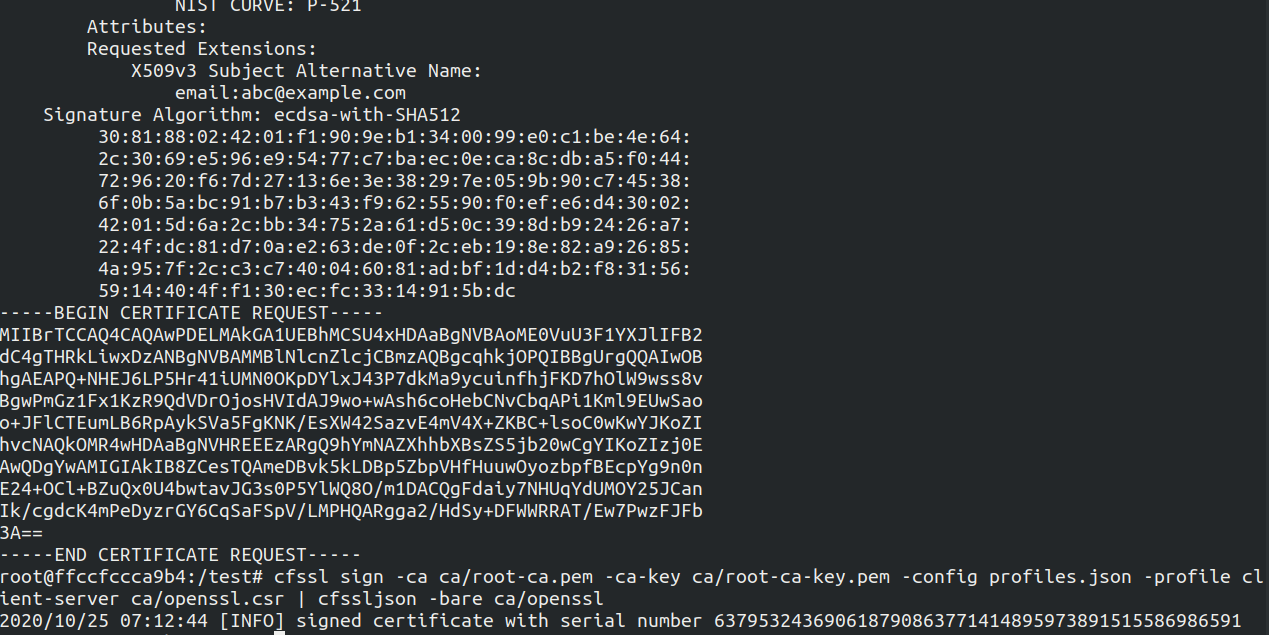
Refer : https://github.com/cloudflare/cfssl/pull/940#issuecomment-624961860
Contributor guide
Research direction
Reproduce the failure with profiles.json, ca-csr.json, and csr.json using cfssl genkey and cfssl sign, then compare the CFSSL-generated CSR with the working OpenSSL CSR. Start at the CFSSL sign entry point and trace SAN extension parsing; done means the CFSSL-generated CSR signs successfully and retains the email SAN.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- go
- Domain
- cryptography, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100