Retrieve open security vulnerabilities
- Dominant language
- Go
- Stars
- 46.3k
- Forks
- 9k
- Avg merge
- 2d 9h
- Merged PRs (30d)
- 89
Description
### Describe the feature or problem you’d like to solve
It would be quite useful for scripting needs to make package security upgrades more efficient to retrieve all open security vulnerabilities, and be able to sort/filter them by severity.
### Proposed solution
Given the following security alerts for a repo:
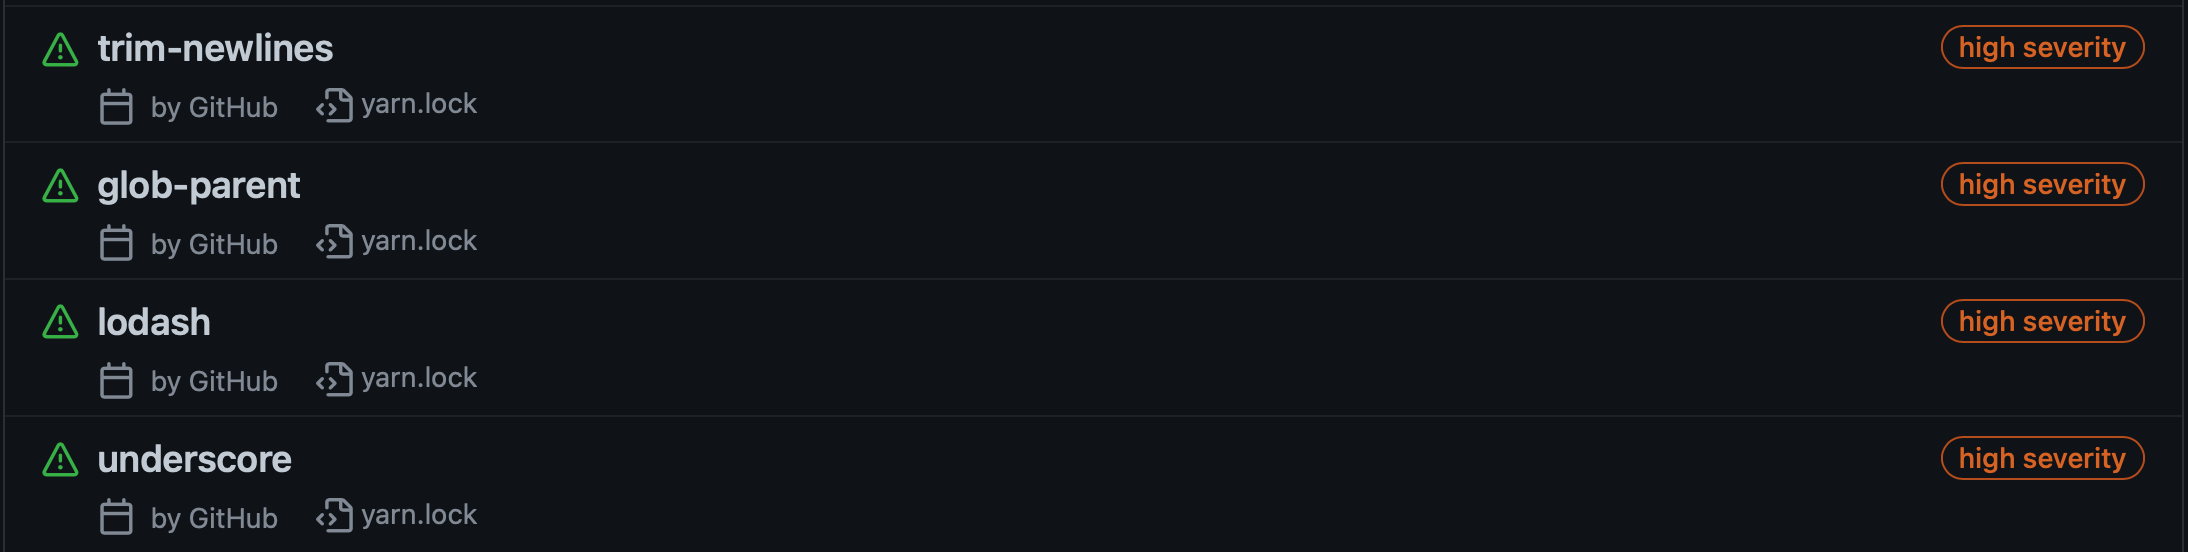
`gh sec list` or `gh security list` could return:
```
Showing 4 of 4 open security alerts in cli/cli:
trim-newlines high 3.0.0 -> 3.0.1
glob-parent high 5.1.0 -> 5.1.2
lodash high 4.17.19 -> 4.17.21
underscore high 1.12.0 -> 1.12.1
```
This would allow scripts to iterate through vulnerable versions (with the `--json` output), find appropriate lock file resolution blocks, delete those blocks, and programmatically run `npm` or `yarn` install to easily bump dependencies with permissive version constraints.
Right now this is O(n) process that *can* be made a bit more simple *if* Dependabot PRs are possible but that's not always the case and it's exceedingly common for organizations like my employer to have a horde of security upgrades to do in one batch. Doing so in discrete PRs is not always a good solution for some repos.
Contributor guide
Assessment
This issue has not been assessed yet.