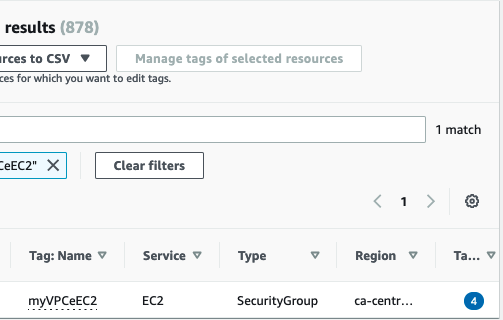
(Tags): Tagging a VPC Interface Endpoint applies the tag on the VPCe Security Group instead of a tag on VPCe
- Dominant language
- TypeScript
- Stars
- 12.9k
- Forks
- 4.6k
- Avg merge
- 1d 19h
- Merged PRs (30d)
- 71
Description
### What is the problem?
Team,
When applying a tag on a VPC Interface Endpoint, the tag gets applied to the Security Group instead of the VPC Endpoint itself.
Code:
```typescript
const vpceEC2 = vpc.addInterfaceEndpoint('vpce-ec2', {
service: ec2.InterfaceVpcEndpointAwsService.EC2,
lookupSupportedAzs: true,
open: true,
privateDnsEnabled: true,
subnets: { subnetType: ec2.SubnetType.PRIVATE_ISOLATED }
});
Tags.of(vpceEC2).add('Name', `myVPCeEC2`);
```
I did a search in Resource Groups Management and the result is as follows:
### Reproduction Steps
Start a new project using cdk init and using lib `"aws-cdk-lib": "2.15.0"`
Add the following code to your stack
Code:
```typescript
const vpcName = "my-cdk-vpc";
const vpc = new ec2.Vpc(this, vpcName, {
cidr: '10.0.0.0/16',
natGateways: 0,
defaultInstanceTenancy: DefaultInstanceTenancy.DEFAULT,
enableDnsHostnames: buildConfig.enableDnsHostnames,
enableDnsSupport: buildConfig.enableDnsSupport,
maxAzs: buildConfig.vpcMaxAZs,
subnetConfiguration: [
{
name: 'private-isolated-',
subnetType: ec2.SubnetType.PRIVATE_ISOLATED,
cidrMask: 24,
}
],
});
const vpceEC2 = vpc.addInterfaceEndpoint('vpce-ec2', {
service: ec2.InterfaceVpcEndpointAwsService.EC2,
lookupSupportedAzs: true,
open: true,
privateDnsEnabled: true,
subnets: { subnetType: ec2.SubnetType.PRIVATE_ISOLATED }
});
Tags.of(vpceEC2).add('Name', `myVPCeEC2`);
```
### What did you expect to happen?
I expected that the VPC Interface Endpoint to have the tag applied to it.
### What actually happened?
The tag was applied to its security group instead.
### CDK CLI Version
2.15.0 (build 151055e)
### Framework Version
v2
### Node.js Version
v14.15.4
### OS
macOS
### Language
Typescript
### Language Version
3.9.7
### Other information
_No response_
Contributor guide
Research direction
Start at the vpc.addInterfaceEndpoint entry point and reproduce the reported Tags.of(vpceEC2).add call from the issue. Trace which resource receives the tag, then verify that the tag is applied to the VPC Interface Endpoint rather than its security group.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- aws, typescript
- Domain
- cloud, networking
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 45/100