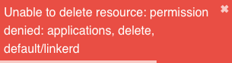
Readonly user error: Unable to delete resource: permission denied: applications, delete, ...
- Dominant language
- Go
- Stars
- 24.2k
- Forks
- 7.9k
- Avg merge
- 1d 6h
- Merged PRs (30d)
- 239
Description
Checklist:
* [x] I've searched in the docs and FAQ for my answer: https://bit.ly/argocd-faq.
* [x] I've included steps to reproduce the bug.
* [x] I've pasted the output of `argocd version`.
**Describe the bug**
ArgoCD supports a `readonly` role:
https://github.com/argoproj/argo-cd/blob/be718e2b6186294e2a84d7cd4789f096e44fc545/assets/builtin-policy.csv#L1
Users with this role shouldn't be encouraged to try to delete objects.
**To Reproduce**
1. Add a `g, user, role:readonly`
1. Log in as that user
1. Browse to a resource
1. Click delete or ⋮, delete
1. Confirm
**Expected behavior**
To the extent possible, if argocd knows a user can't delete resources, the option to delete the resources should be either not shown or not be enabled.
**Screenshots**
**Version**
v1.6.1+159674e
**Logs**
Contributor guide
Research direction
Start with the referenced assets/builtin-policy.csv and the resource browser's Delete or ⋮ action described in the reproduction steps. Reproduce the workflow as a user with role:readonly, then trace where the permission-denied response is surfaced. Done means the delete option is hidden or disabled whenever Argo CD knows the user cannot delete the resource.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- kubernetes
- Domain
- authorization, frontend
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100