Potential secutiry vulnerability in the shared library which kafka-connect-avro-converter-shaded depends on.
- Dominant language
- Java
- Stars
- 15.3k
- Forks
- 3.8k
- Avg merge
- 1d 14h
- Merged PRs (30d)
- 160
Description
Hi, @mostafij-rahman, @Tango2018cc , I'd like to report a vulnerability issue in **org.apache.pulsar:kafka-connect-avro-converter-shaded:2.9.1**.
### Issue Description
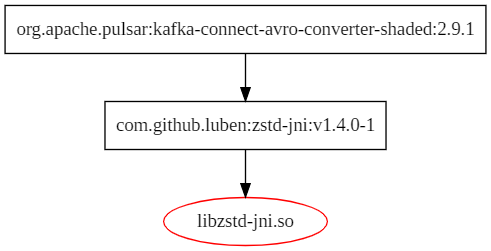
I noticed that **org.apache.pulsar:kafka-connect-avro-converter-shaded:2.9.1** directly depends on **com.github.luben:zstd-jni:v1.4.0-1** in [pom](https://repo1.maven.org/maven2/org/apache/pulsar/kafka-connect-avro-converter-shaded/2.9.1/kafka-connect-avro-converter-shaded-2.9.1.pom). However, as shown in the following dependency graph, **com.github.luben:zstd-jni:v1.4.0-1** sufferes from the vulnerability which the C library **zstd(version:1.4.0)** exposed: [CVE-2021-24031](https://nvd.nist.gov/vuln/detail/CVE-2021-24031).
### Dependency Graph between Java and Shared Libraries
### Suggested Vulnerability Patch Versions
**com.github.luben:zstd-jni:v1.4.9-1** (**>=v1.4.9-1**) has upgraded this vulnerable C library `zstd` to the patch version **1.4.9**.
Java build tools cannot report vulnerable C libraries, which may induce potential security issues to many downstream Java projects. Could you please upgrade this vulnerable dependency?
Thanks for your help~
Best regards,
Helen Parr
Contributor guide
Research direction
Inspect the Maven dependency declaration for org.apache.pulsar:kafka-connect-avro-converter-shaded:2.9.1 and confirm where com.github.luben:zstd-jni:v1.4.0-1 is specified. Update it to version 1.4.9-1 or later, then run the relevant Maven build or dependency verification; done means the artifact no longer pulls the vulnerable zstd version.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- java
- Domain
- security
- Issue type
- Bug
- Difficulty
- 2/5
- Estimated time
- 1-3 hours
- Activity status
- Stale
- Clarity
- Clearly specified
- Newbie friendliness
- 28/100