The kyuubi authz module cannot control the permissions of the “update xxx set xxx where xxx";" type of sql
- Dominant language
- Scala
- Stars
- 2.4k
- Forks
- 1k
- PR merge metrics
- No merged PRs in 30d
Description
### Code of Conduct
- [X] I agree to follow this project's [Code of Conduct](https://www.apache.org/foundation/policies/conduct)
### Search before asking
- [X] I have searched in the [issues](https://github.com/apache/kyuubi/issues?q=is%3Aissue) and found no similar issues.
### Describe the bug
kyuubi authz version : master/1.8.0
ranger version 2.2.0
spark version 3.1.2
iceberg version 0.12.0
I only configure the strategy of select on ranger
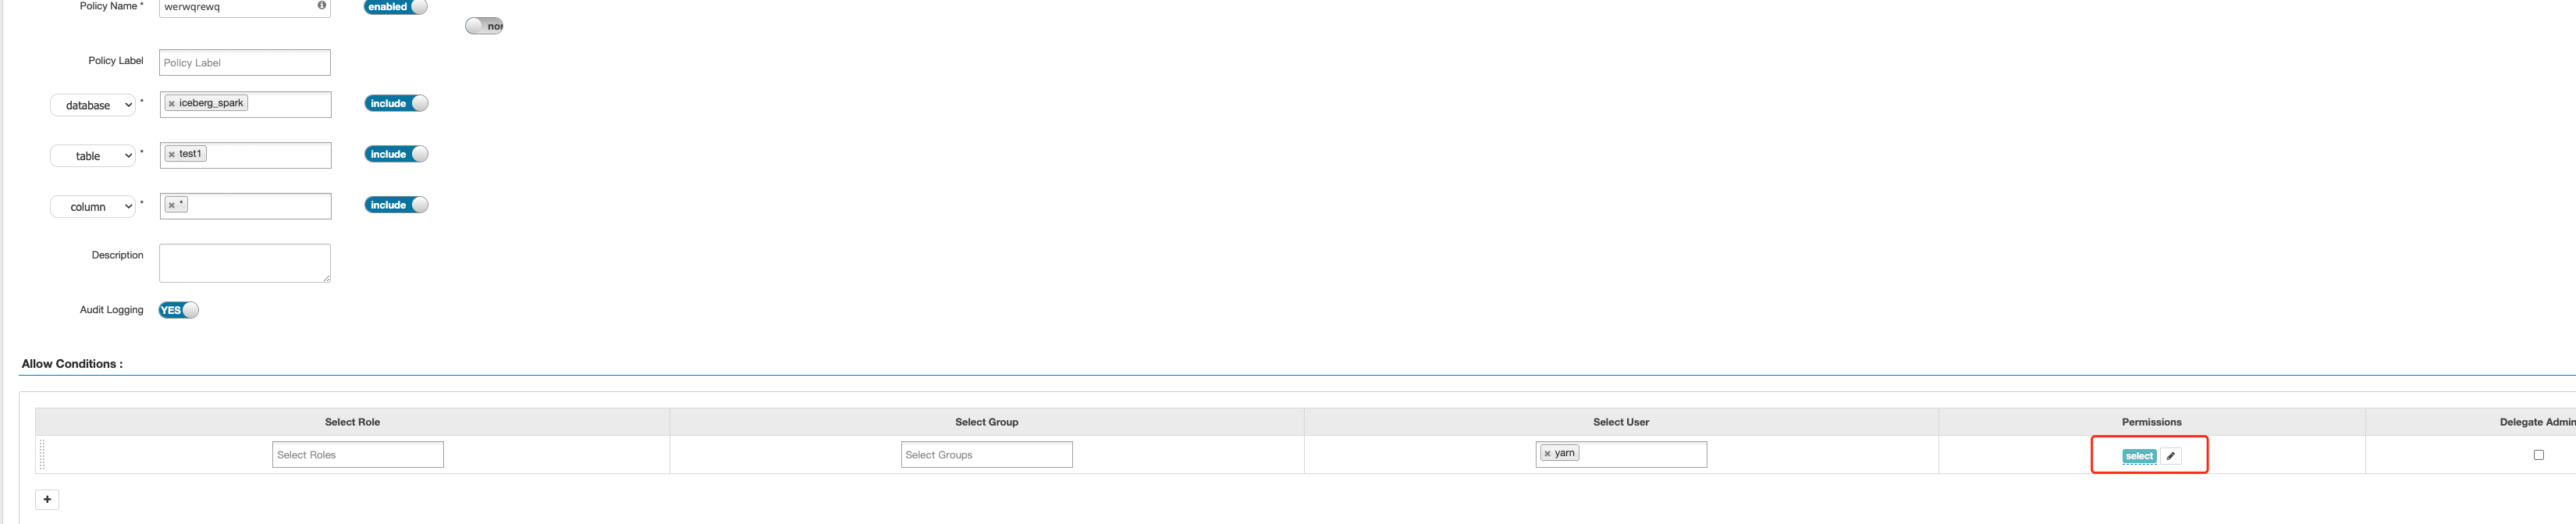
but I can execute this sql: update iceberg_spark.test1 set name="3312" where id="22" successfully

### Affects Version(s)
master
### Kyuubi Server Log Output
_No response_
### Kyuubi Engine Log Output
_No response_
### Kyuubi Server Configurations
_No response_
### Kyuubi Engine Configurations
_No response_
### Additional context
_No response_
### Are you willing to submit PR?
- [X] Yes. I would be willing to submit a PR with guidance from the Kyuubi community to fix.
- [ ] No. I cannot submit a PR at this time.
Contributor guide
Research direction
No source files, tests, or entry points are identified in the issue. Start by reproducing the UPDATE statement with only Ranger SELECT permission under the listed Kyuubi, Ranger, Spark, and Iceberg versions, then trace the authz handling for this SQL form. Done means unauthorized UPDATE statements are rejected while permitted operations continue to work.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- scala, spark, sql
- Domain
- authorization, backend, databases
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 28/100