[Bug] Add AUTHENTICATION_LDAP_FILTER parametes, to fix LdapAuthenticationProviderImpl search condition is valid error
- Dominant language
- Scala
- Stars
- 2.4k
- Forks
- 1k
- PR merge metrics
- No merged PRs in 30d
Description
### Code of Conduct
- [X] I agree to follow this project's [Code of Conduct](https://www.apache.org/foundation/policies/conduct)
### Search before asking
- [X] I have searched in the [issues](https://github.com/apache/incubator-kyuubi/issues?q=is%3Aissue) and found no similar issues.
### Describe the bug
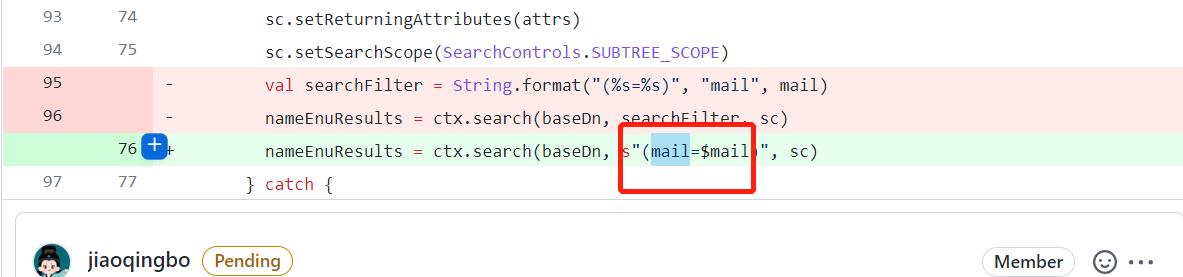
### Affects Version(s)
master
### Kyuubi Server Log Output
_No response_
### Kyuubi Engine Log Output
_No response_
### Kyuubi Server Configurations
_No response_
### Kyuubi Engine Configurations
_No response_
### Additional context
_No response_
### Are you willing to submit PR?
- [X] Yes I am willing to submit a PR!
Contributor guide
Research direction
Start by reproducing the LDAP search-condition error shown in the issue, then inspect LdapAuthenticationProviderImpl and the authentication configuration entry points. Determine how AUTHENTICATION_LDAP_FILTER should be exposed and verify that LDAP authentication succeeds with the configured filter.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- scala
- Domain
- authentication, backend
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100